Menu
How Aztec protects private data from quantum attacks today, and our plan for full post-quantum security.
All blockchains today – L1s, L2s, and shielded pools – make use of elliptic curves somewhere in their stack.
Elliptic curves are used in all sorts of places: signing transactions, validator attestations, data availability (such as blobs), zk-snarks, secret sharing, encryption, etc.
No cryptocurrency project today is 100% quantum-proof.
Nobody has a reliable date for when a quantum computer will break the elliptic-curve cryptography we use today, but we know it’s coming.
For a privacy network, some of the work cannot wait for that uncertainty to resolve. An attacker could collect encrypted data today and keep it until they have the means to decrypt it. This is the so-called “Harvest now; decrypt later” attack. Replacing an encryption scheme ten years from now would not protect the data an attacker already harvested under a classical encryption scheme.
Aztec is already quantum resistant against this type of attack. It was designed from the ground up to allow users to bunker-proof their accounts and data against quantum computers.
However, there is work to be done to make Aztec fully quantum secure and able to function with full privacy in the post-quantum world.
Our roadmap to expand our quantum security has two targets:
The first requires changes to how applications handle private data. The second reaches into the proving system, account authentication, key derivation, validator signatures and Ethereum settlement. Understanding why these need different schedules requires getting into the cryptography.
Years of hard-won experience have taught us that the greatest risk to a network like Aztec is implementation bugs. Our AI audit harness has found critical vulnerabilities, including ones that months of expert human internal and external audits didn’t find. These have been patched in the upcoming v6 Aztec Network release. We have spent the past 18 months hardening our software and cryptography. That work has to continue while we develop their replacements.
AI also changes cryptanalysis. For example, the attack on HAWK (a post-quantum signature scheme) exploited structure specific to that signature scheme and reduced its security enough to end its candidacy for standardization. That is a reason to examine the assumptions and structure of each scheme with care.
Rushing headfirst into new cryptography that has not faced enough scrutiny would expose users to immediate risks, greater than the speculative risks of quantum computers. The Foundation has finite resources, and time spent on the post-quantum migration is time we have to balance against securing the software users depend on today.
Our default approach to changing cryptography is conservative. Any changes to our protocols must be justified, subjected to extraordinary cryptanalysis and have formally-verified implementations.
To make Aztec post-quantum requires several pieces of cryptography. Aztec has an application layer (smart contracts), the Aztec protocol layer, and it settles on Ethereum itself. All three have responsibilities with respect to post-quantum security.
1. Proving System
2. Addresses & Keys
The latter application layer requirements are not on Ethereum’s post-quantum roadmap as they’re a unique requirement of privacy protocols like Aztec and ZCash.
Notice that the bulk of the changes required for user privacy are dictated by the choices of Aztec smart contract developers at the application layer. Apps can adopt post-quantum encryption and signature schemes today on Aztec, and different Aztec smart contract developers can freely explore differing approaches as the state of the art in post-quantum advances.
If and when quantum computers arrive, Aztec is already (uniquely for privacy protocols) protected in two key categories because of our existing design choices.
If I send you private tokens, there’s no onchain public balance update for you to see or query. Private state is stored in notes, so I need to tell you about the existence and contents of your new note for you to be able to use it.
A common solution is for me to publish an encrypted message to a public bulletin board that your wallet can find and decrypt. ZCash pioneered this approach.
Elliptic curve key exchange protocols are well-suited to this, because the amount of data I need to publish to convey “this is for you” and “here’s the ephemeral key you’ll need to decrypt this message” is a single ECDH ephemeral public key; an elliptic curve point; a tiny 32 bytes of info. We like this small communication overhead, because less data means faster tx throughput and cheaper DA costs passed on to users.
But elliptic-curve key exchanges can create a harvest-now-decrypt-later risk. The discrete log of such an ephemeral public key will one day be solvable by a quantum adversary. They could derive all ephemeral secret keys of all messages in the bulletin board. They’d then be able to brute-force combine the resulting list of ephemeral secret keys with a list of all known users’ viewing public keys to effectively derive all decryption keys on the network, to then decrypt all encrypted messages. They’d learn the contents of the note I sent you: the amount and that it belongs to you.
There are a few classical (pre-quantum) solutions to this. They follow from the observation that if an attacker doesn’t know one of: your public key or the ephemeral public key, then they won’t have enough information to decrypt any of your encrypted messages! Wallets are beginning to adopt the following:
Intentionally, most of the public keys in the Aztec protocol are hashed to reduce their leakage to a future post-quantum adversary. The public keys are not even exposed to Aztec smart contracts (which could be malicious).
(Private smart contract protocols even have a niche “harvest now; link later” attack to protect against, whereby a quantum adversary could link all your notes and nullifiers together to reconstruct your entire tx graph. Hashing the nullifier public key resolves this).
The Aztec Protocol is agnostic to the way in which users and applications (smart contracts) share private information between each other. It’s a beautifully flexible protocol because we knew times would change. Smart contract developers can adopt the above conventions today, and indeed many are doing so.
Aztec smart contracts can emit arbitrary bytes of data as “private logs”. These private logs are the intended delivery mechanism for sending encrypted notes. It’s up to smart contract developers how they populate those logs. I.e. they can choose:
Aztec also supports offchain note delivery, which gives applications another secure option. A sender delivers the message through an off-chain side channel that is not visible to harvest-now-decrypt-later attackers.
All this flexibility in today’s Aztec Protocol enables Aztec smart contract developers to explore the tradeoff space in a way that best serves their users and use cases. Choices will need to balance: proving speed; DA costs; discovery of pertinent notes; post-quantum threats.
Of course, most smart contract developers don’t want to think about such things, which is why the Aztec ecosystem has smart contract libraries with off-the-shelf solutions.
Our early 2027 work will focus on hardening these libraries and giving Aztec developers better patterns for protecting their users’ private data, with clear requirements for delivery and secret establishment.
A more comforting solution to post-quantum worries would be for Aztec smart contracts to instead adopt post-quantum secret sharing and encryption schemes.
We’re researching the best approaches and working on some tidy libraries. The good thing is, the agnosticism of the Aztec Protocol means multiple libraries for differing post-quantum secret sharing schemes can be written and adopted by different applications on Aztec.
In most other privacy protocols, the construction of an encrypted note is not constrained by any circuit.
For example, if I send you ZCash tokens, the ‘transfer’ function does not constrain that I have correctly encrypted your note, nor that I have attached the correct ephemeral public key that would enable you to discover and decrypt your encrypted note. I could technically broadcast garbage and you wouldn’t receive your funds. That’s arguably fine in a “simple” transfer protocol. It’s not in my interest to corrupt the encrypted notes that I create for you. After all, you can just claim I didn’t pay you until you do receive a valid and decryptable message.
But when you generalise beyond simple transfers to private smart contracts, there are use cases whereby a sender might not be incentivised to deliver valid data to a recipient. The sender might actually prefer to corrupt a recipient’s data. Imagine a private swap. The contract should not complete the trade if one party receives a commitment to a note whose contents they cannot recover.
In such cases, the private functions (circuits) need to constrain that a recipient will be capable of discovering and decrypting a sender’s encrypted messages. Aztec’s smart contract libraries have rails for this so-called “constrained delivery”. If a use case assumes distrust between sender and recipient, the smart contract developer can enforce their correct adherence to the rules. The protocol then constrains that all private logs emitted by smart contracts are guaranteed to be broadcast – without tampering – to Ethereum blobs.
With this in mind, the constraints required to support post-quantum encryption then become a very important consideration. We’ll need post-quantum libraries that are efficient to prove.
Key and ciphertext sizes matter, but so does the cost of proving the key exchange, encryption and associated checks. A scheme can be fast as native software and expensive inside a circuit.
MIKE, published on 6 October, illustrates why this remains an active research question. It is an isogeny-based non-interactive key-exchange proposal. Its authors report 80-byte public keys and shared-secret computation, including key validation, in 4.9 milliseconds on a 3.3 GHz AMD CPU at their claimed NIST level 1.
Compact keys are attractive for note delivery. We still need to understand its circuit costs and give its security assumptions time to face scrutiny. Those native timings cannot tell us whether it is the right choice for Aztec.
The encryption and proving-system decisions therefore affect each other. Choosing encryption first and discovering that it is prohibitively expensive in the chosen prover would leave us rebuilding one of them.
Choosing the encryption scheme we will prove inside future post-quantum circuits is a separate, later milestone. Applications that need the contract itself to guarantee delivery impose harder requirements on that choice.
Ok, so Aztec provides flexibility for good post-quantum privacy today. And we have plans to roll out even better post-quantum libraries.
But what about the proving system? A post-quantum adversary might be able to forge proofs. Thankfully we have some more time to choose a post-quantum proving system.
Aztec has several proving system requirements that other projects aren’t encumbered by (due to our commitment to both privacy, decentralisation and programmability), which we’ll elaborate on.
Common benchmarks for proving system performance don’t take into consideration all these requirements. Fast client-side recursion in particular is often overlooked.
Aztec uses CHONK, an elliptic-curve and pairing-based proving system built around the requirements of private smart contracts. Users generate proofs on their own devices, and a transaction can involve several private contract calls. Recursion lets us combine those calls into a proof of the transaction without requiring the browser to handle the entire computation as one enormous circuit. CHONK’s design puts low memory use and recursive composition at its centre.
There are tradeoffs you can make to get a faster prover. Some give the verifier more work. A custom “precompile” circuit for an expensive operation can save the prover from executing that operation through thousands of VM instructions, but introduces additional commitments and checks that increases Verifier complexity.
The problem is that, in the recursive setting, your verifier is in your prover. The next proof has to establish that the verifier accepted the previous proof.
I have lost count of the conversations about new prover technology where recursion gets a handwave and a “we’ll deal with it later.” It is a complex, messy problem that is easy to postpone until you need users to generate private transaction proofs in a browser.
Some alternative designs might execute an entire function stack within a single VM instance. That might work for some bounded stack depth. But snarks are gaining traction in web2 too (see zkPassport for example). Bridging between chains also often requires snarks. Privacy protocols should be able to verify traditional snarks for as long as we remain in a pre-quantum world.
Zero knowledge introduces another set of costs. I have heard the same assurances that adding it will be easy and will not affect performance. From personal experience, such claims often disintegrate on contact with reality.
We thought adding zero knowledge to CHONK would be easy. It took us six months and a re-architecture of our recursive proving stack. Modern proof systems have such complexity that throwing randomness into the execution trace and calling it a day almost never works. Adding ZK typically increases proof size and verifier work, which then increases the cost of recursion.
The result is that the real cost of recursion in a production proving system, with all of the edge-cases and exceptions and little additions that pile up, is never as fast as the initial proof-of-concept claims. For Aztec that is a problem because recursion is essential and not an afterthought - we won’t commit to a proving system that can’t meet our extremely tight recursion requirements.
Luckily there are some candidates, and the Ethereum Foundation is doing trailblazing work as one of the few teams that has started to take this problem seriously.
Proof size matters because Aztec transactions travel through a peer-to-peer network. Every node that receives and forwards a proof pays its bandwidth cost. Aztec’s 20kb proofs are “ok”. If it ever becomes a bottleneck we can make them smaller with little effort because we use elliptic curves.
Post-quantum proof systems (the fast ones), on the other hand, have proofs of ~300KB, which is not ok.
Worse, there are zero post-quantum proving systems whose proofs are small enough to gossip across a p2p network whilst achieving acceptable transaction throughput. There are fundamental constraints which mean this is not likely to change!
Fast recursion offers another path. A node could receive two transaction proofs, produce one proof that establishes the validity of both, and forward the aggregate. Other nodes could repeat the process. Transaction data would still have to travel through the network, but the proof overhead could shrink across a batch.
Ethereum’s post-quantum research faces a related problem. Its proposed hash-based validator signatures lack BLS’s cheap native aggregation, so leanVM supplies a proof that many signatures pass verification. The draft EIP-8292 assigns that proving work to aggregators with suitable hardware. Their longer-term roadmap requires full virtual-machine proof aggregations which presents an extremely similar problem to ours.
For the Aztec approach to work on ordinary nodes, aggregation needs to be cheap. My working estimate is that two-to-one aggregation in roughly 20–100 milliseconds on a modern CPU could make it practical.
Nodes receive different transactions at different times, so they will duplicate work. An attacker may try to exploit that duplication. We need to establish how many aggregations one malicious transaction can induce and what happens to throughput under that load.
This problem is currently under-explored and poorly parametrised and substantial work needs to occur before a definitive solution can be decided on.
The main candidates are hash-based systems over binary fields and small prime fields, lattice-based systems, and proposals that combine both prime-field and binary-field representations.
The Flock paper gives a good example of the progress in binary-field proving. Its authors report proving 660,000 BLAKE3 hashes per second on an M4 mac on ten cores.
These are impressive numbers. Hashing is a major part of verifying hash-based proofs, so cheap hashing is good for recursion.
However, binary field systems are weak with regards to integer multiplication. Trustless access to Web2 data is one of the biggest untapped capabilities of blockchain. Private applications should be able to use passport signatures, credit credentials, TLS-based data proofs and signed web tokens without publishing the underlying information. That means dealing with ugly Web2 cryptography: RSA, large-field elliptic curves and integer arithmetic.
Binary-field arithmetic does not behave like integer arithmetic. In particular, integer addition has carries, and multiplication needs a representation and a circuit that handles them. A BLAKE3 benchmark tells us little about the cost of proving a 4096-bit RSA verification. We need to measure the operations our applications will use.
That is what makes hybrid approaches interesting to me: using one commitment both in a binary representation and a prime field representation depending on context. This is an active area of research with limited existing published work, which highlights how rapidly evolving this space is.
Lattice-based proving deserves serious attention too. The Jolt team’s September release replaced the elliptic-curve commitment scheme Dory with Akita, based on Module-SIS. The authors reported faster proving and verification and proofs below 100 KB. Their announcement also described zero knowledge as forthcoming, so those figures do not settle our comparison.
Lattice commitments retain algebraic structure that could be useful for the kinds of composition we rely on. That makes them attractive candidates to investigate, although translating CHONK’s techniques would require work. The field size is a design choice we need to evaluate within each construction; lattices do not impose one universal 128-bit-field requirement.
Much of the suspicion around lattice systems rests on vibes about whether the underlying structure is vulnerable to AI cryptoanalysis. There are good reasons to scrutinize a particular assumption, parameter set or reduction. “It uses lattices” does not supply that scrutiny.
Not all lattice crypto is equal. The fundamental short-integer-solution hardness assumption has had decades of cryptanalysis. Lattice crypto has a degraded reputation because some modern protocols layer on additional, weaker hardness assumptions that have shown to be broken by quantum adversaries. But there is no quantitative evidence to suspect the core harness assumptions of lattice crypto are vulnerable.
Either way, the rate of development gives me confidence that we will have good options. It also makes choosing a winner today premature. We need comparisons that include our applications, recursion, zero knowledge and security parameters together.
In Aztec transactions, digital signatures are private witnesses within private functions of smart contracts (zero-knowledge circuits), which helpfully means we don’t care so much about the size of an individual signature. This gives us more freedom than non-rollups e.g. Ethereum, where signature size directly contributes to their transaction size. This matters because post-quantum digital signatures are typically large.
Similar to other privacy protocols such as ZCash Sapling and Orchard, several Aztec keys are baked-into the preimage of an Aztec address. To enable ‘post-quantumification’ of the Aztec protocol, we’re exploring externalising those keys to a canonical keystore registry. An Aztec address would then cease to be an elliptic-curve public key, and instead would simply be a hash which serves as a lookup into this registry. The registry could store all manner of exotic post-quantum public keys for different use cases.
Aztec uses Poseidon2 throughout the protocol. Poseidon2 is technically post-quantum secure. And while Poseidon2 is secure for our chosen domain, recent breaks over small-field Poseidon signal that we should move to a different hash function in the long-term.
We’re confident that Poseidon2 will remain practically secure for many years, but the writing is on the wall and it would not be wise to use this hash function in Aztec’s future post-quantum system.
We will likely replace it with either Blake2s or Blake3. The Ethereum Foundation are also considering a canonical hash function for their post-quantum roadmap and we’ll more than likely follow their lead here. Binary-field proof systems can trivially handle BLAKE hashes so the need for Poseidon2 will have run its course.
Our proposed selection milestones are:
The encryption milestone needs circuit measurements before we settle the proving-system choice. The proving-system decision needs working recursion and zero knowledge, alongside representative application workloads. These dates give us a sequence for answering those questions.
After selection, we need to replace the cryptography across the system. That includes addresses and key derivation, application-specific key checks inside the kernels, account authentication, validator authentication and the proof chain that ends on Ethereum. We also need to handle existing private state and give users and applications a migration path.
Ethereum supplies another dependency. Aztec’s final proof verification and blob commitments sit within Ethereum’s cryptographic infrastructure. A full post-quantum migration has to account for Ethereum’s upgrades as well as our own.
The roughly three years between the final selection milestone and end of year 2030 leave room for integration to expose problems that isolated benchmarks cannot. Development and integration of multiple novel post-quantum cryptographic primitives into Aztec will be neither simple nor fast. In addition, the entire tech stack will have to be formally verified due to the incredible threat that AI poses with regards to finding and exploiting bugs.
I think Q-day within four years is unlikely, and the roadmap is designed under the assumption that post-quantum work is not the sole focus and obsession of the Aztec Foundation. If there is evidence of faster progress in quantum hardware that would bring forward Q-day, we will be able to accelerate our roadmap by diverting resources to this project.
Developers will not have to wait for that full migration to make better choices about private data. The January work will provide hardened libraries and documented patterns to build against. A developer building a private application will be able to protect the data they create today to stand the test of time.
Core contributors identified a critical vulnerability affecting the V5 Alpha proving system on 27 July 2026 through internal AI-assisted auditing.
V5 remains Alpha software. Critical findings can arise during this phase, and the audit process exists to identify them before broader deployment. This finding places V5 funds, applications, and contract state at risk.
Treat funds and applications on V5 as exposed to a protocol-level failure until contributors complete incident response work and operators carry out the required network actions.
An attacker may be able to exploit a flaw in the current V5 proving system by constructing a proof that passes verification for a transaction the network should reject. If accepted, that transaction could produce a state transition outside the rules V5 intends to enforce.
Contributors cannot determine whether anyone exploited the flaw before this finding. The affected system lacks the information needed to distinguish ordinary accepted transactions from transactions accepted through the flawed proving path. Historical chain activity cannot establish whether exploitation occurred or quantify its impact.
We expect application teams to prepare safeguards in the coming weeks.
Those safeguards may include changes to application controls, deployment procedures, user flows, and migration plans. We expect each team to assess its contracts and determine which protections fit its architecture and users.
We expect teams planning a V5 deployment to pause that work until contributors publish further guidance. We expect teams with live contracts to review their ability to limit user exposure, isolate affected functionality, and move users to fresh deployments if needed.
We expect applications that maintain administrative or emergency controls to assess whether those controls can reduce user risk during the incident timeframe.
Core contributors are working with operators, application teams, and bridge operators as applications add security guards around affected flows.
The findings from this incident will inform the V6 release, including circuit updates that prevent the network from accepting proofs tied to an affected proving system.
V5 launched as Alpha software, with V6 planned for later in 2026. Contributors will publish a security roadmap covering the remaining work and release path.
Reviewers have not identified other high-severity or critical V5 Alpha vulnerabilities at this time.
Internal and external human audits have completed, and contributors continue AI-assisted auditing. Alpha is the period for identifying faults before production deployment.
Dark Forest is a real-time strategy game played across a procedurally generated universe where most of the map is hidden. You cannot see rival players, their planets, or their fleets. You only know what you have explored. Everyone shares one universe, and nobody has the full picture.
In most onchain games, every position and every move is public, because the chain is public. Dark Forest used zero-knowledge proofs to break that assumption: players prove their moves are valid without revealing where those moves came from. The result is a game of hidden information running on a public network.
Dark Forest Aztec ports the original Dark Forest 0.6 to Aztec. It keeps the gameplay from the original and rebuilds the privacy layer on Aztec's programmable privacy.
A note before diving in: this is early, experimental software on Aztec Alpha V5. Treat it as an alpha and play accordingly.
You start on a single home planet with almost the entire map dark. To find anything you mine the universe, running a client that explores coordinates and reveals what sits there: unclaimed planets, resources, and eventually the edges of other players' territory.
You are never handed a view of the board. You earn it one region at a time, and everyone else works under the same fog.
Your home coordinates and your fleet movements are private state, expressed as first-class private notes on Aztec. Your location and where you send energy stay hidden, enforced in the contracts by zero-knowledge cryptography.
What sits onchain is a set of cryptographic commitments. Instead of storing every planet's full details in the open, the contracts store Poseidon2 hashes of entity state. When you make a move, your client supplies the full state, the contract checks it against the stored hash, applies the change under zero-knowledge constraints, and writes a new hash back. Full game state lives offchain and gets rebuilt from public logs by an indexer, which is what renders your map without exposing every player's position.
So you can prove you made a legal move from a planet you own without revealing where that planet is. Aztec applies the same principle to private payments and private contracts.
Four actions carry the game.
Explore. Your explorer sits in the bottom left. Set it running and it uncovers the map around you, surfacing planets, resources, and other players.
Send energy. Most planets produce energy. Click and drag from a planet you own toward a target to capture or weaken it.
Route silver. Asteroid fields produce silver. Move it to your planets and spend it on upgrades, or send it to a Spacetime Rip to convert it into score.
Hunt artifacts. Some planets hold artifacts. Your Gear ship discovers them. Once harvested, you deposit them on planets to boost stats.
Four stats drive most decisions.
Energy is the core resource. Planets generate it over time up to a capacity, and you spend it on everything: claiming planets, reinforcing your own, attacking rivals. Two details matter. Moves are taxed, so a flat percentage of a planet's total capacity burns every time you send energy, which discourages small frequent moves. And energy decays over distance, so send it too far and almost nothing arrives. A common rule of thumb is to let a planet fill to about 75%, then send it down to about 25%.
Defense reduces the damage incoming energy does when it lands. Higher-level planets often have lower defense, but they hold much more energy, so they still take more to capture. Defense matters most on front lines.
Range sets how far a planet can send energy. It governs how fast you expand and how efficiently you move energy inside your own empire, since shorter relative distances mean less decay. Good range also lets you strike deep into an opponent's territory.
Speed sets how quickly a move arrives. Usually secondary, though a fast strike can land before a rival reacts, and some playstyles reward capturing many nearby planets quickly.
Planets can also be upgraded with silver and enhanced with artifacts. Space types carry different multipliers, from mild Nebula to punishing Dead Space, so where a planet sits changes how it plays.
There is a scoreboard, and territory alone does not win it. This round scores two activities: discovering artifacts with your Gear ship, and withdrawing silver through Spacetime Rips.
Point values from the in-game help page:
Silver accrues one point at a time. A single Mythic artifact is worth twenty million of them, so artifact hunting decides rounds and silver withdrawal sets your floor.
Silver has two competing uses. Spend it on upgrades and your planets get stronger, extending range and hardening defense. Withdraw it through a Spacetime Rip and it becomes scored points, but it is gone. Every unit is a choice between building the empire and banking points.
Upgrades tend to win early, since a stronger empire reaches more asteroid fields and finds more artifacts. Late in a round that calculation flips, because a planet you never use is worth less than points already scored.
Artifacts do both jobs at once. They score on discovery, and once deposited they boost a planet's stats, which makes the next expedition easier.
Nothing happens until you find something to act on. Your explorer turns dark space into planets you can capture, asteroid fields you can mine, and artifact-bearing planets you can raid. Sitting still means no new energy, no silver, no score.
Exploring also buys information. The map you have uncovered is an advantage nobody else holds. Knowing where high-level planets sit, which asteroid fields are unclaimed, and where space types shift lets you plan further ahead than someone still working through their starting region.
You find other players as a byproduct. There is no player list. You explore outward until your revealed region touches territory someone already owns: a planet in another player's colors, sitting where you were about to expand. Their home coordinates stay private, so you learn something narrow. Someone is here, roughly this direction, holding this much. You infer the rest, and you have no way of knowing whether they found you first.
You have three broad options.
Stay quiet and keep growing. Nothing forces you to engage. Keep exploring elsewhere, keep routing silver, keep upgrading. Your positions stay private, so silence costs you only time, which is what you want if they are stronger. The risk is that they are doing the same thing faster.
Fortify the border. If the contact sits somewhere you cannot lose, spend energy hardening the planets facing them. Defense is worth most where an attack will actually land. This keeps the option to fight without committing to one.
Attack. Send enough energy to overwhelm the target's defense and the planet becomes yours, along with its production and its position as a staging post. Higher-level planets are the prize and take proportionally more to crack.
Attacking costs more than energy. A move that lands tells your rival where you strike from, and that you are close enough to be worth answering. Retaliation can then come from directions you have not explored, launched from planets you cannot see.
Everyone plays one shared universe in real time. No turns, no lobbies. Energy regenerates whether you are watching or not, moves stay in flight while you sleep, and rivals expand while you are away from the screen.
Most strategy games let you watch a threat approach. Here you tend to see the consequences: a planet you owned this morning in someone else's colors, an incoming move you notice once it is already close.
That produces a particular kind of paranoia. You are trying to find everyone else while avoiding being found, and every expansion is a strategic bet that the space ahead is empty.
Information becomes tradeable, because it is scarce. Players compare notes, warn each other about aggressive neighbors, and agree who expands where, then break those agreements when the scoreboard makes it worth breaking.
A fully onchain game where players cannot see each other's positions is hard to build, and building it well says something about the platform underneath.
Hidden state, private notes, and client-side proving are the same building blocks behind private applications across Aztec. Dark Forest is a way to watch them work.
Dark Forest Aztec is playable now as an alpha. Expect a learning curve; the original was famous for it. DFArchon maintains onboarding material and a community for new players. Round One is live. The universe is dark, and everyone else is out there somewhere. Go find them, quietly.
Gas on Aztec is known as Fee Juice and is used to pay for transaction costs. This is the same as $ETH on Ethereum. Some apps will handle transaction costs for you under the hood, but if you are using a browser extension wallet, you will not be able to send transactions without it. Fee Juice can be obtained by bridging the $AZTEC token on Ethereum to the Aztec Network L2. This means that under the hood, all activity that happens on Aztec is underpinned by the $AZTEC token bridged into the network. Some bridges like Shield (by human.tech) handle this for you, allowing you to allocate a portion of your bridged transaction to convert into Fee Juice and land in your wallet automatically.
Assets and transactions on the Aztec Network can be either public or private. If you bridge publicly, your tokens will arrive as public, traceable tokens visible to all. Privately bridging, on the other hand, will give you private assets that are visible only to you. These assets can then be sent privately to another user or wallet without ever revealing who you are, what tokens were sent, how many, or who the recipient is.
Like tokens on the Aztec Network, Fee Juice (gas) can also be public or private. The reason for this is that even if what you are sending is private, the gas you spend to execute that transaction could still be visible if you are using public Fee Juice, potentially revealing transaction patterns and activity. Private Fee Juice keeps your entire transaction footprint hidden. When you send a private transaction, you can use private Fee Juice, and when you send a public transaction, you can use public Fee Juice, which means your transaction costs are always aligned with the type of transaction you're making.
Aztec has native fee abstraction, which means apps could let you pay for transactions in any token you want, or cover your fees entirely. Apps like Nyx may choose to cover part or all of a user's transaction costs, or allow you to pay in tokens that are convenient for you. This means you will most likely never see Fee Juice in an app; instead, you'll pay in whatever makes sense for what you're doing, on your terms. Similarly, you might never even see an Aztec wallet at all, because the app itself becomes your interface that you connect to using your MetaMask wallet.
If you're using a browser extension like Azguard, you'll manage Fee Juice directly in your wallet alongside your private and public balances, converting between tokens as needed to cover transaction costs.
When you bridge tokens in, you'll need enough Fee Juice to cover the cost of your first transaction, then you'll need to monitor how much Fee Juice you have available to make transactions. Browser wallets will allow you to send either publicly or privately to other users and will default to using either public or private Fee Juice depending on the type of transaction. Both private Fee Juice and public Fee Juice will appear by default in your token list.
How you handle Fee Juice depends on where you're transacting: apps can abstract it away entirely and let you pay in any token, while a browser wallet like Azguard puts it in your hands to manage across public and private balances. Match your gas to your transaction, keep private activity private down to the fee, and you move on your terms.
The Aztec Network today activated Alpha V5, a major protocol upgrade passed by token-holder governance and executed onchain. Alpha V5 reduces private-transaction proving times by more than 2x compared to the previous version, lowers the cost of a fully private transaction by roughly 50%, resolves the critical issues found in V4, and sees the first wave of apps go live. Users can now send private transactions and earn yield on Aave simply by connecting their Ethereum wallets on Nyx, bridge from Ethereum to Aztec using Shield or TRAIN, privately collect NFTs on RavenHouse, or play Dark Forest Aztec, a hidden-information strategy game in a universe that lives entirely onchain.
"Alpha V5 continues Aztec's work at the frontier of client-side proving, with cryptographic breakthroughs that cut proving times by more than half this release," said Zac Williamson, Co-founder, Aztec Foundation. "We believe Aztec is now the fastest system in the world for proving a fully private transaction entirely on a user's own device, and every release moves the industry closer to private transactions at public transaction speeds."
As the only decentralized privacy L2, Aztec is the credibly neutral privacy layer for Ethereum. Aztec allows anyone to write smart contracts that include both private and public aspects – every private transaction is proven on the user's own device, so no operator, sequencer, or intermediary can see the data. The Alpha V5 proving improvements come from cryptographic advances that make this client-side proving faster than any prior release. The network remains in alpha, but with V5 it is ready for teams to begin building and deploying applications.
Making private transactions practical comes down to how quickly a proof can be generated on a user's own device, without offloading that work to a server that would learn what the user is doing. On Alpha V5, proving a private token transfer natively now takes approximately 2.5 seconds on a consumer laptop, down from 5.2 seconds on V4, and about 6.8 seconds in a browser, down from 12.5 seconds. Across every measured transaction flow, client-side proving times improved by approximately 2x compared with V4.

Alpha V5 lowers ECDSA signature-verification cost by approximately 2x, speeds up Poseidon2 hashing by approximately 3x, and reduces the protocol circuit gate count by approximately 50% (gate count is the number of individual operations a proving circuit must perform, and it is the main driver of how long a proof takes to generate). Each of these lowers the amount of work a device performs to prove a transaction, and the reduction in gate count in particular compounds across every proof the network generates.
Alpha V5 launches the first wave of apps on a network where privacy is built into the protocol rather than managed by an operator. On other networks that claim privacy, transactions still pass through an operator or node that reads them in plaintext, or depend on a viewing key that a third party holds, so users rely on someone else to protect their data and to decide when it gets disclosed. On Aztec, every private transaction is proven on the user's own device, so the app, the sequencer, and any operator never need to see the underlying data. Nyx is one of these apps, allowing users to privately send transactions and privately earn yield on Aave.
"On Ethereum, everything you do is public. That's why we built Nyx: a private account governed by your Ethereum wallet", said Nikhil, Co-founder of Nyx. "Now you can send, receive and earn in private. Nyx was the first app live on the Aztec Alpha, and we're excited to expand participation to more users with the added stability of Alpha V5."
Other apps on Alpha V5 include Azguard and Nethermind (wallets), Shield, TRAIN, and RavenHouse (bridges), and the Aztecscan block explorers. Also launching is Dark Forest Aztec, a game where users explore a universe, control planets, manage planetary energy, expand territory, and launch attacks through strategic play with private state and hidden actions.

Transaction fees on Aztec come from two main sources: the cost of proving a transaction and the cost of verifying the rollup proof on Ethereum. Alpha V5 reduces both. It lowers the network's proving-cost parameter by 50%, and it reduces the L1 gas required to verify a rollup proof by approximately 40%. Because rollup proofs are verified on Ethereum and that cost is shared across all transactions in a batch, the L1 reduction lowers fees for every user, while the lower proving-cost parameter reduces the per-transaction proving fee directly. Together, these bring the average cost of a fully private token transfer to under a $0.05 transaction cost.
Alpha V5 also hardens the network on several fronts. It resolves critical vulnerabilities found in Alpha V4 along with additional bugs discovered since launch. Aztec's bug bounty program on Cantina also drew more than 234 security researchers to participate. The network remains in alpha, and further bugs may surface as usage grows, but each release has closed the issues found in the last and strengthened the protocol against new ones. With the critical V4 issues resolved and these safeguards in place, Alpha V5 is stable enough for teams to begin building and deploying applications.
Alpha V5 is live now, view the Alpha V5 landing page for a full list of features, performance updates, and live apps to explore.
Aztec is the only decentralized, privacy-first Layer 2 on Ethereum. Developers write private and public logic in the same smart contract, and private functions are executed and proven on the user's own device, so no operator sees the underlying data. The protocol is upgraded through onchain governance, and the network settles to Ethereum. For more information, visit aztec.network.
All blockchains today – L1s, L2s, and shielded pools – make use of elliptic curves somewhere in their stack.
Elliptic curves are used in all sorts of places: signing transactions, validator attestations, data availability (such as blobs), zk-snarks, secret sharing, encryption, etc.
No cryptocurrency project today is 100% quantum-proof.
Nobody has a reliable date for when a quantum computer will break the elliptic-curve cryptography we use today, but we know it’s coming.
For a privacy network, some of the work cannot wait for that uncertainty to resolve. An attacker could collect encrypted data today and keep it until they have the means to decrypt it. This is the so-called “Harvest now; decrypt later” attack. Replacing an encryption scheme ten years from now would not protect the data an attacker already harvested under a classical encryption scheme.
Aztec is already quantum resistant against this type of attack. It was designed from the ground up to allow users to bunker-proof their accounts and data against quantum computers.
However, there is work to be done to make Aztec fully quantum secure and able to function with full privacy in the post-quantum world.
Our roadmap to expand our quantum security has two targets:
The first requires changes to how applications handle private data. The second reaches into the proving system, account authentication, key derivation, validator signatures and Ethereum settlement. Understanding why these need different schedules requires getting into the cryptography.
Years of hard-won experience have taught us that the greatest risk to a network like Aztec is implementation bugs. Our AI audit harness has found critical vulnerabilities, including ones that months of expert human internal and external audits didn’t find. These have been patched in the upcoming v6 Aztec Network release. We have spent the past 18 months hardening our software and cryptography. That work has to continue while we develop their replacements.
AI also changes cryptanalysis. For example, the attack on HAWK (a post-quantum signature scheme) exploited structure specific to that signature scheme and reduced its security enough to end its candidacy for standardization. That is a reason to examine the assumptions and structure of each scheme with care.
Rushing headfirst into new cryptography that has not faced enough scrutiny would expose users to immediate risks, greater than the speculative risks of quantum computers. The Foundation has finite resources, and time spent on the post-quantum migration is time we have to balance against securing the software users depend on today.
Our default approach to changing cryptography is conservative. Any changes to our protocols must be justified, subjected to extraordinary cryptanalysis and have formally-verified implementations.
To make Aztec post-quantum requires several pieces of cryptography. Aztec has an application layer (smart contracts), the Aztec protocol layer, and it settles on Ethereum itself. All three have responsibilities with respect to post-quantum security.
1. Proving System
2. Addresses & Keys
The latter application layer requirements are not on Ethereum’s post-quantum roadmap as they’re a unique requirement of privacy protocols like Aztec and ZCash.
Notice that the bulk of the changes required for user privacy are dictated by the choices of Aztec smart contract developers at the application layer. Apps can adopt post-quantum encryption and signature schemes today on Aztec, and different Aztec smart contract developers can freely explore differing approaches as the state of the art in post-quantum advances.
If and when quantum computers arrive, Aztec is already (uniquely for privacy protocols) protected in two key categories because of our existing design choices.
If I send you private tokens, there’s no onchain public balance update for you to see or query. Private state is stored in notes, so I need to tell you about the existence and contents of your new note for you to be able to use it.
A common solution is for me to publish an encrypted message to a public bulletin board that your wallet can find and decrypt. ZCash pioneered this approach.
Elliptic curve key exchange protocols are well-suited to this, because the amount of data I need to publish to convey “this is for you” and “here’s the ephemeral key you’ll need to decrypt this message” is a single ECDH ephemeral public key; an elliptic curve point; a tiny 32 bytes of info. We like this small communication overhead, because less data means faster tx throughput and cheaper DA costs passed on to users.
But elliptic-curve key exchanges can create a harvest-now-decrypt-later risk. The discrete log of such an ephemeral public key will one day be solvable by a quantum adversary. They could derive all ephemeral secret keys of all messages in the bulletin board. They’d then be able to brute-force combine the resulting list of ephemeral secret keys with a list of all known users’ viewing public keys to effectively derive all decryption keys on the network, to then decrypt all encrypted messages. They’d learn the contents of the note I sent you: the amount and that it belongs to you.
There are a few classical (pre-quantum) solutions to this. They follow from the observation that if an attacker doesn’t know one of: your public key or the ephemeral public key, then they won’t have enough information to decrypt any of your encrypted messages! Wallets are beginning to adopt the following:
Intentionally, most of the public keys in the Aztec protocol are hashed to reduce their leakage to a future post-quantum adversary. The public keys are not even exposed to Aztec smart contracts (which could be malicious).
(Private smart contract protocols even have a niche “harvest now; link later” attack to protect against, whereby a quantum adversary could link all your notes and nullifiers together to reconstruct your entire tx graph. Hashing the nullifier public key resolves this).
The Aztec Protocol is agnostic to the way in which users and applications (smart contracts) share private information between each other. It’s a beautifully flexible protocol because we knew times would change. Smart contract developers can adopt the above conventions today, and indeed many are doing so.
Aztec smart contracts can emit arbitrary bytes of data as “private logs”. These private logs are the intended delivery mechanism for sending encrypted notes. It’s up to smart contract developers how they populate those logs. I.e. they can choose:
Aztec also supports offchain note delivery, which gives applications another secure option. A sender delivers the message through an off-chain side channel that is not visible to harvest-now-decrypt-later attackers.
All this flexibility in today’s Aztec Protocol enables Aztec smart contract developers to explore the tradeoff space in a way that best serves their users and use cases. Choices will need to balance: proving speed; DA costs; discovery of pertinent notes; post-quantum threats.
Of course, most smart contract developers don’t want to think about such things, which is why the Aztec ecosystem has smart contract libraries with off-the-shelf solutions.
Our early 2027 work will focus on hardening these libraries and giving Aztec developers better patterns for protecting their users’ private data, with clear requirements for delivery and secret establishment.
A more comforting solution to post-quantum worries would be for Aztec smart contracts to instead adopt post-quantum secret sharing and encryption schemes.
We’re researching the best approaches and working on some tidy libraries. The good thing is, the agnosticism of the Aztec Protocol means multiple libraries for differing post-quantum secret sharing schemes can be written and adopted by different applications on Aztec.
In most other privacy protocols, the construction of an encrypted note is not constrained by any circuit.
For example, if I send you ZCash tokens, the ‘transfer’ function does not constrain that I have correctly encrypted your note, nor that I have attached the correct ephemeral public key that would enable you to discover and decrypt your encrypted note. I could technically broadcast garbage and you wouldn’t receive your funds. That’s arguably fine in a “simple” transfer protocol. It’s not in my interest to corrupt the encrypted notes that I create for you. After all, you can just claim I didn’t pay you until you do receive a valid and decryptable message.
But when you generalise beyond simple transfers to private smart contracts, there are use cases whereby a sender might not be incentivised to deliver valid data to a recipient. The sender might actually prefer to corrupt a recipient’s data. Imagine a private swap. The contract should not complete the trade if one party receives a commitment to a note whose contents they cannot recover.
In such cases, the private functions (circuits) need to constrain that a recipient will be capable of discovering and decrypting a sender’s encrypted messages. Aztec’s smart contract libraries have rails for this so-called “constrained delivery”. If a use case assumes distrust between sender and recipient, the smart contract developer can enforce their correct adherence to the rules. The protocol then constrains that all private logs emitted by smart contracts are guaranteed to be broadcast – without tampering – to Ethereum blobs.
With this in mind, the constraints required to support post-quantum encryption then become a very important consideration. We’ll need post-quantum libraries that are efficient to prove.
Key and ciphertext sizes matter, but so does the cost of proving the key exchange, encryption and associated checks. A scheme can be fast as native software and expensive inside a circuit.
MIKE, published on 6 October, illustrates why this remains an active research question. It is an isogeny-based non-interactive key-exchange proposal. Its authors report 80-byte public keys and shared-secret computation, including key validation, in 4.9 milliseconds on a 3.3 GHz AMD CPU at their claimed NIST level 1.
Compact keys are attractive for note delivery. We still need to understand its circuit costs and give its security assumptions time to face scrutiny. Those native timings cannot tell us whether it is the right choice for Aztec.
The encryption and proving-system decisions therefore affect each other. Choosing encryption first and discovering that it is prohibitively expensive in the chosen prover would leave us rebuilding one of them.
Choosing the encryption scheme we will prove inside future post-quantum circuits is a separate, later milestone. Applications that need the contract itself to guarantee delivery impose harder requirements on that choice.
Ok, so Aztec provides flexibility for good post-quantum privacy today. And we have plans to roll out even better post-quantum libraries.
But what about the proving system? A post-quantum adversary might be able to forge proofs. Thankfully we have some more time to choose a post-quantum proving system.
Aztec has several proving system requirements that other projects aren’t encumbered by (due to our commitment to both privacy, decentralisation and programmability), which we’ll elaborate on.
Common benchmarks for proving system performance don’t take into consideration all these requirements. Fast client-side recursion in particular is often overlooked.
Aztec uses CHONK, an elliptic-curve and pairing-based proving system built around the requirements of private smart contracts. Users generate proofs on their own devices, and a transaction can involve several private contract calls. Recursion lets us combine those calls into a proof of the transaction without requiring the browser to handle the entire computation as one enormous circuit. CHONK’s design puts low memory use and recursive composition at its centre.
There are tradeoffs you can make to get a faster prover. Some give the verifier more work. A custom “precompile” circuit for an expensive operation can save the prover from executing that operation through thousands of VM instructions, but introduces additional commitments and checks that increases Verifier complexity.
The problem is that, in the recursive setting, your verifier is in your prover. The next proof has to establish that the verifier accepted the previous proof.
I have lost count of the conversations about new prover technology where recursion gets a handwave and a “we’ll deal with it later.” It is a complex, messy problem that is easy to postpone until you need users to generate private transaction proofs in a browser.
Some alternative designs might execute an entire function stack within a single VM instance. That might work for some bounded stack depth. But snarks are gaining traction in web2 too (see zkPassport for example). Bridging between chains also often requires snarks. Privacy protocols should be able to verify traditional snarks for as long as we remain in a pre-quantum world.
Zero knowledge introduces another set of costs. I have heard the same assurances that adding it will be easy and will not affect performance. From personal experience, such claims often disintegrate on contact with reality.
We thought adding zero knowledge to CHONK would be easy. It took us six months and a re-architecture of our recursive proving stack. Modern proof systems have such complexity that throwing randomness into the execution trace and calling it a day almost never works. Adding ZK typically increases proof size and verifier work, which then increases the cost of recursion.
The result is that the real cost of recursion in a production proving system, with all of the edge-cases and exceptions and little additions that pile up, is never as fast as the initial proof-of-concept claims. For Aztec that is a problem because recursion is essential and not an afterthought - we won’t commit to a proving system that can’t meet our extremely tight recursion requirements.
Luckily there are some candidates, and the Ethereum Foundation is doing trailblazing work as one of the few teams that has started to take this problem seriously.
Proof size matters because Aztec transactions travel through a peer-to-peer network. Every node that receives and forwards a proof pays its bandwidth cost. Aztec’s 20kb proofs are “ok”. If it ever becomes a bottleneck we can make them smaller with little effort because we use elliptic curves.
Post-quantum proof systems (the fast ones), on the other hand, have proofs of ~300KB, which is not ok.
Worse, there are zero post-quantum proving systems whose proofs are small enough to gossip across a p2p network whilst achieving acceptable transaction throughput. There are fundamental constraints which mean this is not likely to change!
Fast recursion offers another path. A node could receive two transaction proofs, produce one proof that establishes the validity of both, and forward the aggregate. Other nodes could repeat the process. Transaction data would still have to travel through the network, but the proof overhead could shrink across a batch.
Ethereum’s post-quantum research faces a related problem. Its proposed hash-based validator signatures lack BLS’s cheap native aggregation, so leanVM supplies a proof that many signatures pass verification. The draft EIP-8292 assigns that proving work to aggregators with suitable hardware. Their longer-term roadmap requires full virtual-machine proof aggregations which presents an extremely similar problem to ours.
For the Aztec approach to work on ordinary nodes, aggregation needs to be cheap. My working estimate is that two-to-one aggregation in roughly 20–100 milliseconds on a modern CPU could make it practical.
Nodes receive different transactions at different times, so they will duplicate work. An attacker may try to exploit that duplication. We need to establish how many aggregations one malicious transaction can induce and what happens to throughput under that load.
This problem is currently under-explored and poorly parametrised and substantial work needs to occur before a definitive solution can be decided on.
The main candidates are hash-based systems over binary fields and small prime fields, lattice-based systems, and proposals that combine both prime-field and binary-field representations.
The Flock paper gives a good example of the progress in binary-field proving. Its authors report proving 660,000 BLAKE3 hashes per second on an M4 mac on ten cores.
These are impressive numbers. Hashing is a major part of verifying hash-based proofs, so cheap hashing is good for recursion.
However, binary field systems are weak with regards to integer multiplication. Trustless access to Web2 data is one of the biggest untapped capabilities of blockchain. Private applications should be able to use passport signatures, credit credentials, TLS-based data proofs and signed web tokens without publishing the underlying information. That means dealing with ugly Web2 cryptography: RSA, large-field elliptic curves and integer arithmetic.
Binary-field arithmetic does not behave like integer arithmetic. In particular, integer addition has carries, and multiplication needs a representation and a circuit that handles them. A BLAKE3 benchmark tells us little about the cost of proving a 4096-bit RSA verification. We need to measure the operations our applications will use.
That is what makes hybrid approaches interesting to me: using one commitment both in a binary representation and a prime field representation depending on context. This is an active area of research with limited existing published work, which highlights how rapidly evolving this space is.
Lattice-based proving deserves serious attention too. The Jolt team’s September release replaced the elliptic-curve commitment scheme Dory with Akita, based on Module-SIS. The authors reported faster proving and verification and proofs below 100 KB. Their announcement also described zero knowledge as forthcoming, so those figures do not settle our comparison.
Lattice commitments retain algebraic structure that could be useful for the kinds of composition we rely on. That makes them attractive candidates to investigate, although translating CHONK’s techniques would require work. The field size is a design choice we need to evaluate within each construction; lattices do not impose one universal 128-bit-field requirement.
Much of the suspicion around lattice systems rests on vibes about whether the underlying structure is vulnerable to AI cryptoanalysis. There are good reasons to scrutinize a particular assumption, parameter set or reduction. “It uses lattices” does not supply that scrutiny.
Not all lattice crypto is equal. The fundamental short-integer-solution hardness assumption has had decades of cryptanalysis. Lattice crypto has a degraded reputation because some modern protocols layer on additional, weaker hardness assumptions that have shown to be broken by quantum adversaries. But there is no quantitative evidence to suspect the core harness assumptions of lattice crypto are vulnerable.
Either way, the rate of development gives me confidence that we will have good options. It also makes choosing a winner today premature. We need comparisons that include our applications, recursion, zero knowledge and security parameters together.
In Aztec transactions, digital signatures are private witnesses within private functions of smart contracts (zero-knowledge circuits), which helpfully means we don’t care so much about the size of an individual signature. This gives us more freedom than non-rollups e.g. Ethereum, where signature size directly contributes to their transaction size. This matters because post-quantum digital signatures are typically large.
Similar to other privacy protocols such as ZCash Sapling and Orchard, several Aztec keys are baked-into the preimage of an Aztec address. To enable ‘post-quantumification’ of the Aztec protocol, we’re exploring externalising those keys to a canonical keystore registry. An Aztec address would then cease to be an elliptic-curve public key, and instead would simply be a hash which serves as a lookup into this registry. The registry could store all manner of exotic post-quantum public keys for different use cases.
Aztec uses Poseidon2 throughout the protocol. Poseidon2 is technically post-quantum secure. And while Poseidon2 is secure for our chosen domain, recent breaks over small-field Poseidon signal that we should move to a different hash function in the long-term.
We’re confident that Poseidon2 will remain practically secure for many years, but the writing is on the wall and it would not be wise to use this hash function in Aztec’s future post-quantum system.
We will likely replace it with either Blake2s or Blake3. The Ethereum Foundation are also considering a canonical hash function for their post-quantum roadmap and we’ll more than likely follow their lead here. Binary-field proof systems can trivially handle BLAKE hashes so the need for Poseidon2 will have run its course.
Our proposed selection milestones are:
The encryption milestone needs circuit measurements before we settle the proving-system choice. The proving-system decision needs working recursion and zero knowledge, alongside representative application workloads. These dates give us a sequence for answering those questions.
After selection, we need to replace the cryptography across the system. That includes addresses and key derivation, application-specific key checks inside the kernels, account authentication, validator authentication and the proof chain that ends on Ethereum. We also need to handle existing private state and give users and applications a migration path.
Ethereum supplies another dependency. Aztec’s final proof verification and blob commitments sit within Ethereum’s cryptographic infrastructure. A full post-quantum migration has to account for Ethereum’s upgrades as well as our own.
The roughly three years between the final selection milestone and end of year 2030 leave room for integration to expose problems that isolated benchmarks cannot. Development and integration of multiple novel post-quantum cryptographic primitives into Aztec will be neither simple nor fast. In addition, the entire tech stack will have to be formally verified due to the incredible threat that AI poses with regards to finding and exploiting bugs.
I think Q-day within four years is unlikely, and the roadmap is designed under the assumption that post-quantum work is not the sole focus and obsession of the Aztec Foundation. If there is evidence of faster progress in quantum hardware that would bring forward Q-day, we will be able to accelerate our roadmap by diverting resources to this project.
Developers will not have to wait for that full migration to make better choices about private data. The January work will provide hardened libraries and documented patterns to build against. A developer building a private application will be able to protect the data they create today to stand the test of time.
The Aztec Network today activated Alpha V5, a major protocol upgrade passed by token-holder governance and executed onchain. Alpha V5 reduces private-transaction proving times by more than 2x compared to the previous version, lowers the cost of a fully private transaction by roughly 50%, resolves the critical issues found in V4, and sees the first wave of apps go live. Users can now send private transactions and earn yield on Aave simply by connecting their Ethereum wallets on Nyx, bridge from Ethereum to Aztec using Shield or TRAIN, privately collect NFTs on RavenHouse, or play Dark Forest Aztec, a hidden-information strategy game in a universe that lives entirely onchain.
"Alpha V5 continues Aztec's work at the frontier of client-side proving, with cryptographic breakthroughs that cut proving times by more than half this release," said Zac Williamson, Co-founder, Aztec Foundation. "We believe Aztec is now the fastest system in the world for proving a fully private transaction entirely on a user's own device, and every release moves the industry closer to private transactions at public transaction speeds."
As the only decentralized privacy L2, Aztec is the credibly neutral privacy layer for Ethereum. Aztec allows anyone to write smart contracts that include both private and public aspects – every private transaction is proven on the user's own device, so no operator, sequencer, or intermediary can see the data. The Alpha V5 proving improvements come from cryptographic advances that make this client-side proving faster than any prior release. The network remains in alpha, but with V5 it is ready for teams to begin building and deploying applications.
Making private transactions practical comes down to how quickly a proof can be generated on a user's own device, without offloading that work to a server that would learn what the user is doing. On Alpha V5, proving a private token transfer natively now takes approximately 2.5 seconds on a consumer laptop, down from 5.2 seconds on V4, and about 6.8 seconds in a browser, down from 12.5 seconds. Across every measured transaction flow, client-side proving times improved by approximately 2x compared with V4.
Alpha V5 lowers ECDSA signature-verification cost by approximately 2x, speeds up Poseidon2 hashing by approximately 3x, and reduces the protocol circuit gate count by approximately 50% (gate count is the number of individual operations a proving circuit must perform, and it is the main driver of how long a proof takes to generate). Each of these lowers the amount of work a device performs to prove a transaction, and the reduction in gate count in particular compounds across every proof the network generates.
Alpha V5 launches the first wave of apps on a network where privacy is built into the protocol rather than managed by an operator. On other networks that claim privacy, transactions still pass through an operator or node that reads them in plaintext, or depend on a viewing key that a third party holds, so users rely on someone else to protect their data and to decide when it gets disclosed. On Aztec, every private transaction is proven on the user's own device, so the app, the sequencer, and any operator never need to see the underlying data. Nyx is one of these apps, allowing users to privately send transactions and privately earn yield on Aave.
"On Ethereum, everything you do is public. That's why we built Nyx: a private account governed by your Ethereum wallet", said Nikhil, Co-founder of Nyx. "Now you can send, receive and earn in private. Nyx was the first app live on the Aztec Alpha, and we're excited to expand participation to more users with the added stability of Alpha V5."
Other apps on Alpha V5 include Azguard and Nethermind (wallets), Shield, TRAIN, and RavenHouse (bridges), and the Aztecscan block explorers. Also launching is Dark Forest Aztec, a game where users explore a universe, control planets, manage planetary energy, expand territory, and launch attacks through strategic play with private state and hidden actions.
Transaction fees on Aztec come from two main sources: the cost of proving a transaction and the cost of verifying the rollup proof on Ethereum. Alpha V5 reduces both. It lowers the network's proving-cost parameter by 50%, and it reduces the L1 gas required to verify a rollup proof by approximately 40%. Because rollup proofs are verified on Ethereum and that cost is shared across all transactions in a batch, the L1 reduction lowers fees for every user, while the lower proving-cost parameter reduces the per-transaction proving fee directly. Together, these bring the average cost of a fully private token transfer to under a $0.05 transaction cost.
Alpha V5 also hardens the network on several fronts. It resolves critical vulnerabilities found in Alpha V4 along with additional bugs discovered since launch. Aztec's bug bounty program on Cantina also drew more than 234 security researchers to participate. The network remains in alpha, and further bugs may surface as usage grows, but each release has closed the issues found in the last and strengthened the protocol against new ones. With the critical V4 issues resolved and these safeguards in place, Alpha V5 is stable enough for teams to begin building and deploying applications.
Alpha V5 is live now, view the Alpha V5 landing page for a full list of features, performance updates, and live apps to explore.
Aztec is the only decentralized, privacy-first Layer 2 on Ethereum. Developers write private and public logic in the same smart contract, and private functions are executed and proven on the user's own device, so no operator sees the underlying data. The protocol is upgraded through onchain governance, and the network settles to Ethereum. For more information, visit aztec.network.
Crypto is in a long night. It is no secret that the industry is facing challenging circumstances and there has been a clear consolidation of the industry. Right now we are seeing a focus on real traction, demonstrable value projects shipping practical solutions that will meaningfully reach users.
Some of that discipline is overdue. However, in times like these the properties that made crypto structurally different begin to look expendable. Decentralization slows you down. It makes upgrades harder. It makes institutional sales harder. It removes the control surfaces that the existing financial world knows how to buy.
We used to accept those costs as the price of building something durable. But, in a famine, they look like unaffordable affectations. Discarding them wholesale, however, is like selling the land out from under our feet.
Permissionless, uncensorable transaction networks with rich composability - this is the clay from which our industry was grown. The long term commercial health of our industry depends on preserving these properties in an age of privacy and institutional adoption.
These trade-offs become more challenging and pernicious when privacy is involved. Privacy is the narrative for crypto in 2026, and for good reason. It’s the missing piece that will deliver the traction and real use-cases that the industry so desperately needs.
The challenges of decentralization multiply under the constraints of privacy and what we are seeing in the industry is not a pivot, but a complete capitulation of all of the differentiable value that made crypto valuable.
I have spent nearly a decade building a network that marries programmable privacy with decentralization. A network where users keep their data, where applications are composable with one another, where transactions can settle without a privileged party learning everyone’s business or deciding which products are allowed to exist. That required new cryptography, new programming models, new state architecture, new wallets, and a fairly insane number of tradeoffs that are invisible until you try to build the thing yourself. There are easier products to ship.
A centralized privacy service can give institutions something legible quickly, replicating how the existing financial sector works: a responsible operator, a viewing key, a way to block transactions, a way to explain the whole thing to a risk committee. Some of these products will be useful. Some will be good businesses. But they are not the thing we came here to build.
Institutional and enterprise adoption is one of the core growth areas in this crypto-winter and the playbook is simple: use the language of crypto as a skin-suit to sell products and services that pattern match onto existing financial rails, with their need for complete visibility, censorship, centralized network operators and all of the liabilities this incurs.
This is a tempting bargain because it shortens the path to adoption. It gives buyers and regulators a shape they understand. A company. A contract. A switch. But the moment you accept that bargain, the system changes character. It may still be encrypted. It may still contain proofs. It may still call itself private. But, it now behaves like and is an operated service.
There is a party with privileged knowledge and privileged control. Builders must shape themselves around it. Institutions negotiate with it. Regulators may pressure it. Attackers target it. Users ultimately depend on it. By a backdoor I mean something specific: a network or protocol-level viewing key where the product developer does not control who can see their users’ data, especially when paired with network-level controls that can block transactions or ban smart contracts entirely. I do not mean application-level controls. I do not mean user-authorised disclosure. I do not mean a dapp deciding that users must prove something before using it. Regulated applications will need rules. The issue is that the disclosure boundary of your application belongs to somebody else, and the same layer that sees can also decide whether your users are allowed to transact. In short, users lack a platform that has credible neutrality.
Privacy on top of centralized rails is fatal. If one party can see everything and stop anything, that party may be treated as responsible for seeing and stopping.
This compounds into substantial platform risk. If an entity builds on top of such a system they must surrender visibility and control to the network operator to satisfy their liabilities without consideration for yours. Decentralization and ultimately credible neutrality is the difference between whether you own durable infrastructure or are renting a service whose rules can change on a whim. Worse, you cannot “just build things”. For novel transaction flows approval must be sought and granted. Tell me, would Ethereum have grown if every smart contract deployment required approval from the Ethereum Foundation?
Privacy needs the same freedom. A private credit market, for example, touches identity, collateral, repayment history, payment flows, liquidation logic, lender disclosures, auditor access and borrower privacy. If every component lives inside a different permissioned service, each with its own operator and viewing assumptions, that is a bureaucratic friction that negates blockchain’s core value proposition; composability.
A decentralized and credibly neutral privacy network prevents the settlement layer from becoming the single place where all surveillance and censorship obligations naturally accumulate. It allows product developers to scope their code to satisfy their own narrow requirements without consideration for the obligations of a centralized operator.
A lot of today’s privacy narrative treats architecture as if it were a detail. It is not. You cannot take a transparent ledger, staple confidentiality onto the edge, add a viewing key for comfort, and expect to get programmable private infrastructure.
If the state model is not private from the ground up you get wrappers, third party tools, data custodians, ad hoc disclosure paths and a pile of assumptions that every application drags into the next. Developers do not get a normal programming model where private contracts can call private contracts and users keep state on their own devices. They do not get composability.
The difference matters. In a real private execution environment, users generate transactions locally. They do not outsource their intent to a third party who learns what they are doing. Private contracts interact through a state model designed for privacy. The network settles proofs without becoming the party that knows everyone’s business. Privacy is part of the architecture.
This is why Aztec has taken so long. We built something that makes programmable private state and decentralised settlement live inside the same system. That means proving systems that run on consumer hardware, a transaction architecture built around local private execution, and a programming model where privacy is idiomatic and just works out of the box.
A centralized service can skip much of this. It can hold the key, run the prover, approve the flow and call the result privacy. It gets to market faster because it is not trying to arrive at the same place.
Adding decentralization does not make obligations disappear. Applications, issuers, frontends, custodians and regulated businesses will continue to exist in a web of obligations and responsibilities. Anyone pretending otherwise is unserious.
The question is where those obligations live. If they are pushed into the settlement layer, the settlement layer is no longer credibly neutral. It needs visibility into everyone and controls over everyone.
The better answer is selective disclosure. Users and applications should prove specific facts to specific parties for specific purposes. A regulated application may need to know that a user passed a check, that a transaction satisfies a policy, or that an auditor can inspect a particular flow. None of that requires the base network to hold a permanent key into everyone’s activity.
This will be harder to explain to the existing world. New infrastructure always fails to fit the categories built for the old infrastructure. Bitcoin did not arrive as a neatly regulated bank product. Ethereum did not wait for every lawyer to understand smart contracts. Stablecoins and DeFi forced institutions, regulators and users to develop new language around rails that kept existing.
If the standard for privacy infrastructure is to plug into the old world without changing anything, the answer will always be a service with a backdoor. And the result will be to catch crumbs falling from the tables of the old world.
The market we should be building is, well, a market. A private financial system that compounds: assets, liquidity, identity, credentials, credit and applications interacting through a shared settlement layer without forcing users to surrender their data to whoever sits in the middle.
Traditional finance is built out of vertically integrated information silos. Those silos are its moat. Banks, exchanges, custodians, payment processors and data brokers all benefit from controlling the information that flows through them. A global private settlement layer attacks that advantage directly. It lets liquidity and credentials move while outsourcing information custody to neutral cryptographic infrastructure.
A company wants a moat. A settlement layer wants surface area. A permissioned privacy provider can ration access, raise fees, exclude applications, shape disclosure rules and define acceptable use around its own risk tolerance. These are products pretending to be networks, and not durable financial infrastructure. What bothers me is this compounding category confusion. Networks adding protocol-level viewing keys and transaction controls are using the same language as decentralised programmable privacy, and commentators are treating them as variations of the same thing. They are not.
We have spent nine years walking the hard road. Now, just as we are close, the market has lost faith. Everyone is reaching for whatever lifeline looks immediate. Some of those lifelines will be real. Some will make money. But if crypto responds to its long night by rebuilding financial privacy as permissioned services, then we will have survived by surrendering the property that made the industry worth building.
Markets can grow when the platform is removed from the position where it can dictate the rules. It would be perverse to forget that lesson while building privacy, the domain where control over information matters most.
Crypto is in a famine. The land is struggling. We could sell our land for a pittance and survive the season. But the famine will pass, and when it does the land will blossom again. Without the land we are nothing.
We have struggled immensely to create a permissionless network that can marry privacy with decentralisation: an indestructible network whose users cannot be surveilled and whose transactions cannot be censored. This is the soil we have to grow our crops. To surrender a backdoor or a centralized operator for temporary relief is to sell our land for the price of a stablecoin. And we cannot sell the land.
Follow Zac on X to get more insights
Follow Aztec on X for updates & breaking news
Privacy has become a baseline requirement for L1s and L2s who care about bringing real-world users onchain. Users don't want their activity broadcast to competitors or the general public, but applications operating at scale also need some form of auditability, whether for regulators, compliance requirements, or tax reporting. Selective disclosure resolves that tension: privacy by default, with the ability to prove specific facts when required. What separates these networks is not whether they offer that switch, but who gets to hold it.
Aztec, Canton, Starknet, Tempo, and zkSync all offer some form of privacy with selective disclosure, but under the hood they make fundamentally different architectural decisions about who can see your data and who can turn your privacy off. Those decisions determine whether your privacy stays under your own control or sits behind a switch that someone else operates.
Three questions reveal where these networks actually diverge:
The answers determine whether your privacy off-switch is held by a policy, by an operator's good behavior, or by you alone through a cryptographic proof. As you'll see in this post, there are legitimate reasons to use each one with different tradeoffs. Aztec is the only network, however, where that switch stays in the user's hands, answering all three questions without putting a permissioned set of operators or a standing viewing key in control of your privacy. That gives developers the flexibility to build apps that comply with applicable laws while still keeping full privacy under the user's control.
This article will compare the privacy approaches of Aztec, Canton, Starknet, Tempo, and zkSync to give developers insight into the privacy tradeoffs of each network.
Here’s how each network handles the selective disclosure privacy off-switch, and who has control over your privacy:
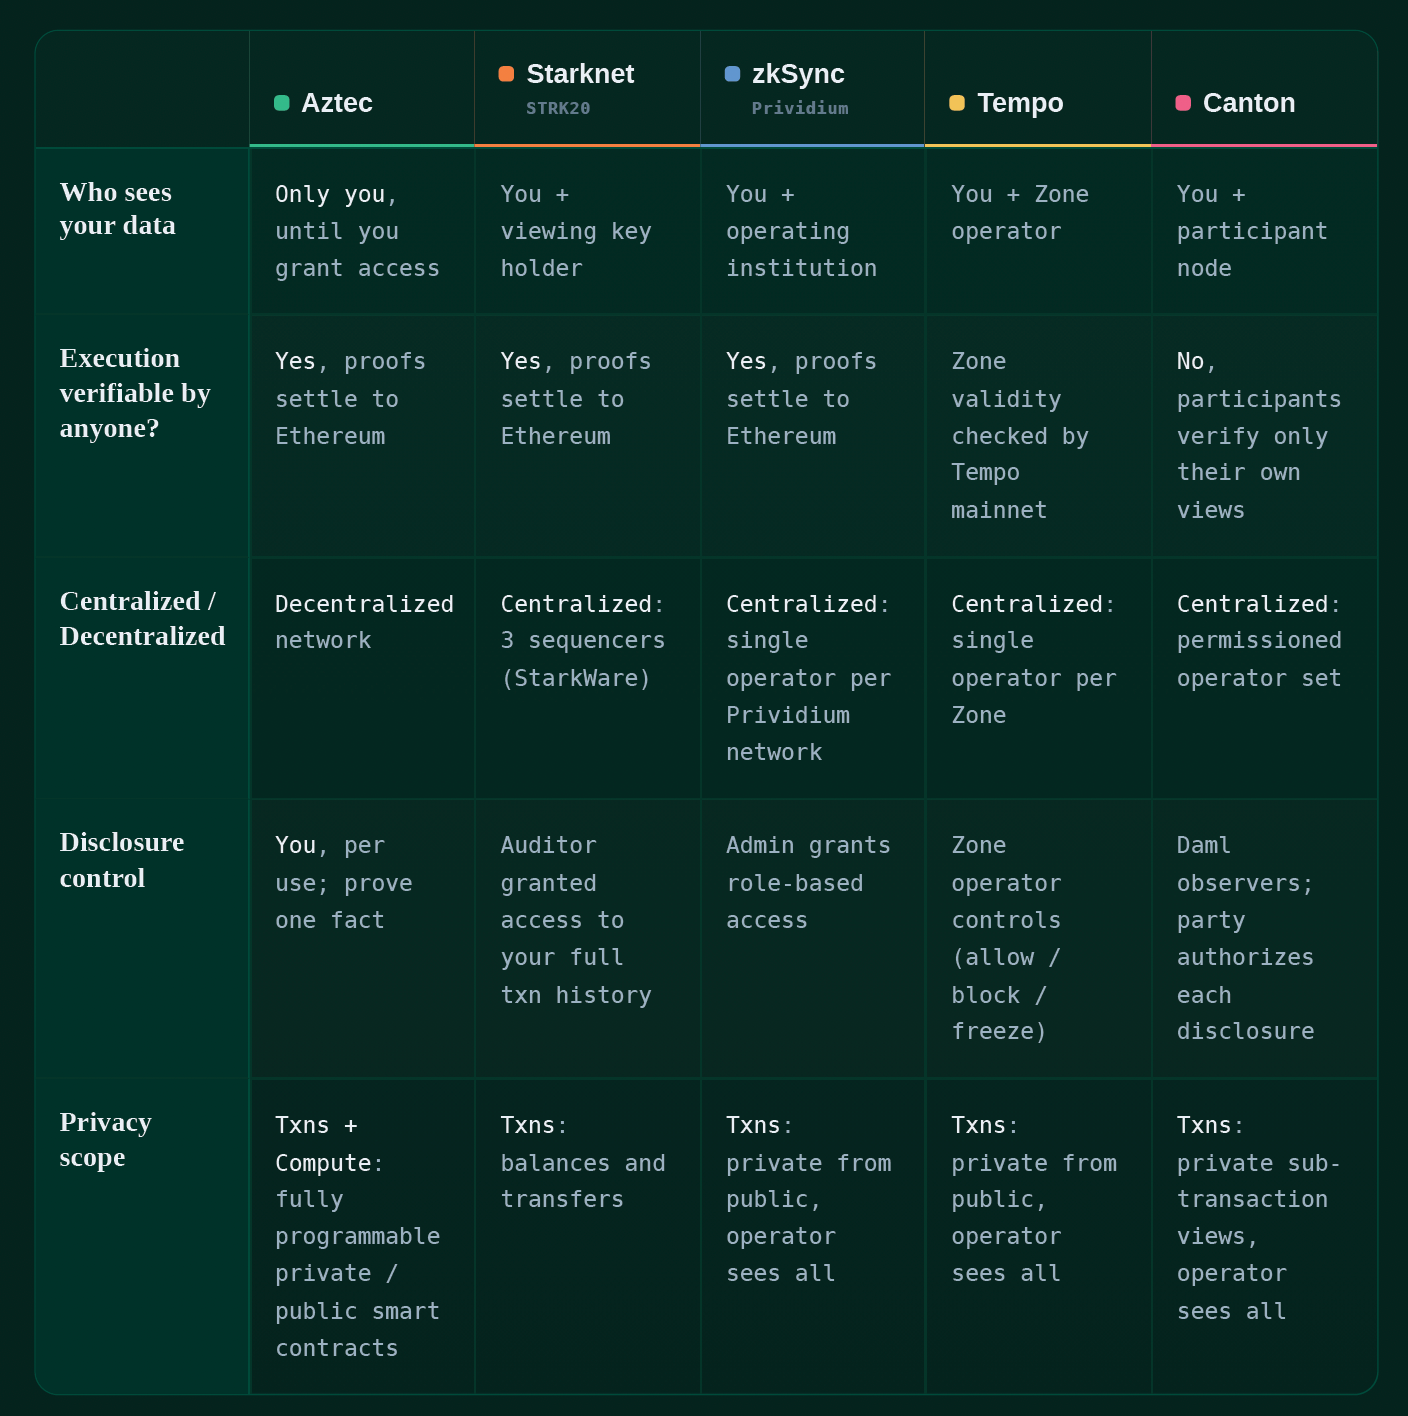
Each of these networks offers privacy with selective disclosure, but each rests on a different network design with its own tradeoffs. We have ordered them by who holds your privacy off-switch, starting with designs where a third party controls access to your data and ending with designs where that control stays with you. At the top, the switch sits behind a policy promise and an honest operator, and further down it is replaced by proofs that the user generates and controls.
Canton keeps data private by controlling viewing permissions for the various actors on its network. A transaction splits into per-participant views, so each party receives only the sub-transactions that name it, and the parts it is not entitled to never reach it. The sequencer and mediator move those views without reading them, which is real privacy against those roles.
However, the data is still read in plaintext by the participant nodes that host the relevant parties, and in the common regulated-asset pattern where the issuer is a signatory on its own token, the issuer's node sees every transfer. The harder gap is verification, because no third party can reconstruct the global ledger, so correctness rests on the confirming nodes staying honest and their keys staying safe. In practice the off-switch sits with those nodes rather than with you, since you cannot see when your data is read and cannot stop it.
Tempo is designed for payments and uses validity proofs to verify that each zone is executing correctly, while still giving the zone operator full plaintext visibility into every transaction within that zone. Privacy comes from Tempo Zones, which are parallel execution environments connected to the Tempo mainnet.
By design, the zone operator has visibility into all transactions within the zone, while users see only their own and the public sees only a proof that the zone is valid. Token issuers set compliance controls, allowlists, blocklists, and freezes, enforced across zones. The mainnet checks each zone's validity, so execution is verified, while the operator still reads every transaction in plaintext and holds the off-switch over what is revealed. Your privacy is from the public, not from the operator.
zkSync Prividium adds the verifiability piece that Canton lacks. Every batch produces a validity proof settled to Ethereum, so a compromised operator cannot forge state or mint tokens from nothing without also forging a proof, which it cannot do. The tradeoff is that the operator processes every transaction in plaintext and decides who sees what, which means the off-switch stays with the operator and your privacy is from the outside world rather than from the operator itself.
This tradeoff has legitimate uses in high-trust institutional environments. If Bank of America, JPMorgan, and Wells Fargo are transacting on a shared network, a zone where BofA's infrastructure processes BofA-originated transactions satisfies internal control requirements while still delivering genuine ZK privacy from the other banks and the rest of the world. Where this model breaks down is in lower-trust environments where giving an operator full plaintext access and the switch that comes with it holds back product design possibilities.
Starknet's STRK20 breaks from relying on an operator for privacy. It shields ERC-20 balances and transfers in a privacy pool, and every private transaction carries a zero-knowledge proof generated client-side, so no operator sees your plaintext in order to build it.
Disclosure is where STRK20 diverges from Aztec. To join the Starknet Privacy Pool, you register an encrypted viewing key onchain, and it sits there for the life of your participation. On a regulatory request, a designated auditing entity can decrypt that key and trace your complete transaction history, forwards and backwards. StarkWare calls this ‘not a backdoor’ but a carefully scoped access mechanism, and the safeguard is a policy promise that the auditor decrypts only when required. The privacy is cryptographic, but the off-switch is a standing key that someone else holds and can flip whether or not you are watching.
On Aztec your private state lives as encrypted private data that only you can decrypt. The contract developer can choose what state is public and what is private, and whether your encrypted private data is emitted onchain as a private log or shared off-chain instead.
Your transactions get proven client-side on your own device, so no sequencer or operator sees your unencrypted private data. Those proofs settle to Ethereum, which gives the same integrity anchor marketed by Prividium, with every transaction verified and no forged state, but without a single operator who reads your data. The base protocol decentralizes sequencing, proving, and governance, so there is no operator to choose and trust in the first place.
Disclosure is your choice too: you decide who learns your private data, and whether they learn it in encrypted or decrypted form. To grant discovery without readability, you share an app-specific tagging secret that lets an auditor find your data in encrypted form without being able to decrypt and read it. This is enough to prove things calculated from that data, such as a tax basis or a profit and loss figure. Granting permission to actually read the data works differently. There's no per-contract read key you can hand out, because decryption uses your master viewing key, which would unlock all your data across every contract. So instead of sharing a key, you share the data itself, plus a proof that your plaintext is what encrypts to the on-chain ciphertext.
Aztec has true selective disclosure in that you can selectively share it, and nothing else you don’t need to. This is app specific, meaning that private data discoverability access on one app does not grant access on another. Most importantly, the off-switch stays in your hands, and you never need to trust the network to handle access to any of your private data and activity.
This is not just conceptual: here is a working proof-of-concept of this model on Aztec. PrivPNL takes you from private DEX trades through a tagging-key disclosure to a browser-generated ZK proof of your PnL. The auditor verifies a proof while the prover only has to reveal the amount they owe, and your portfolio stays private.
Canton keeps the switch with the participant nodes that read your data in plaintext, so disclosure rests on those nodes staying honest rather than on anything you control. Tempo similarly gives the off-switch to a zone-based node operator, but allows you to verify the correctness of transactions using validity proofs. Prividium hardens that promise with a proof settled to Ethereum, a real improvement, but the operator still reads every transaction and still decides who sees what. This can work well for large institutions, but small to medium sized enterprises are left with the same privacy as their current banks unless they run their own Prividium nodes. STRK20 moves the switch into a standing viewing key and asks you to trust that a designated auditor reaches for it only when needed. In each of these models the real question is not whether your privacy can be switched off, but who gets to do the switching, and whether you would even know it happened.
Aztec takes the operator and the standing key out of the question entirely. You keep the data, you generate the proof, and you disclose the result, one fact at a time and only when you choose to. The off-switch never leaves your hands, and no operator, auditor, or node can reach it on your behalf. This is one of the benefits of a network that offers fully programmable, privacy-preserving smart contracts that put you in control.
Selective disclosure is how privacy survives contact with a regulator, and the model you pick decides who can open your history when you are not looking. On Aztec, that answer is no one but you.
Dive into the technical details: Try a live demo of selective disclosure on Aztec and read the technical article on how it was built.
Integrate with Aztec: Reach out if you are interested in integrating privacy into your project.
Aztec is built on one idea: smart contracts on Ethereum where developers choose what is public and what is private. That doesn't just mean shielded transactions. It means who acts (identity), what they transact (state), and how they execute (computation) can all be private. Aztec makes end-to-end privacy possible; even the contracts themselves can be private.
But privacy also has to be practical. Aztec integrates private and public execution in the same contract, so apps can seamlessly weave together private and public state. Every account is a smart contract, letting users grant granular, revocable access for selective disclosure, which is useful for compliance, tax reporting, or agent permissions.
Finally, Aztec is a decentralized L2, with 3,500+ sequencers participating in the network today. That permissionlessness is what makes Aztec a credible foundation for a global privacy layer.
In this article we’re going to explore the Aztec stack and how we make programmable privacy a reality. We’ll answer questions like ‘what can you do on Aztec?’, ‘how does it all work?’, and ‘what are the core layers of the system that makes it all possible?’
The four layers of the Aztec stack, all live today on the Alpha network:
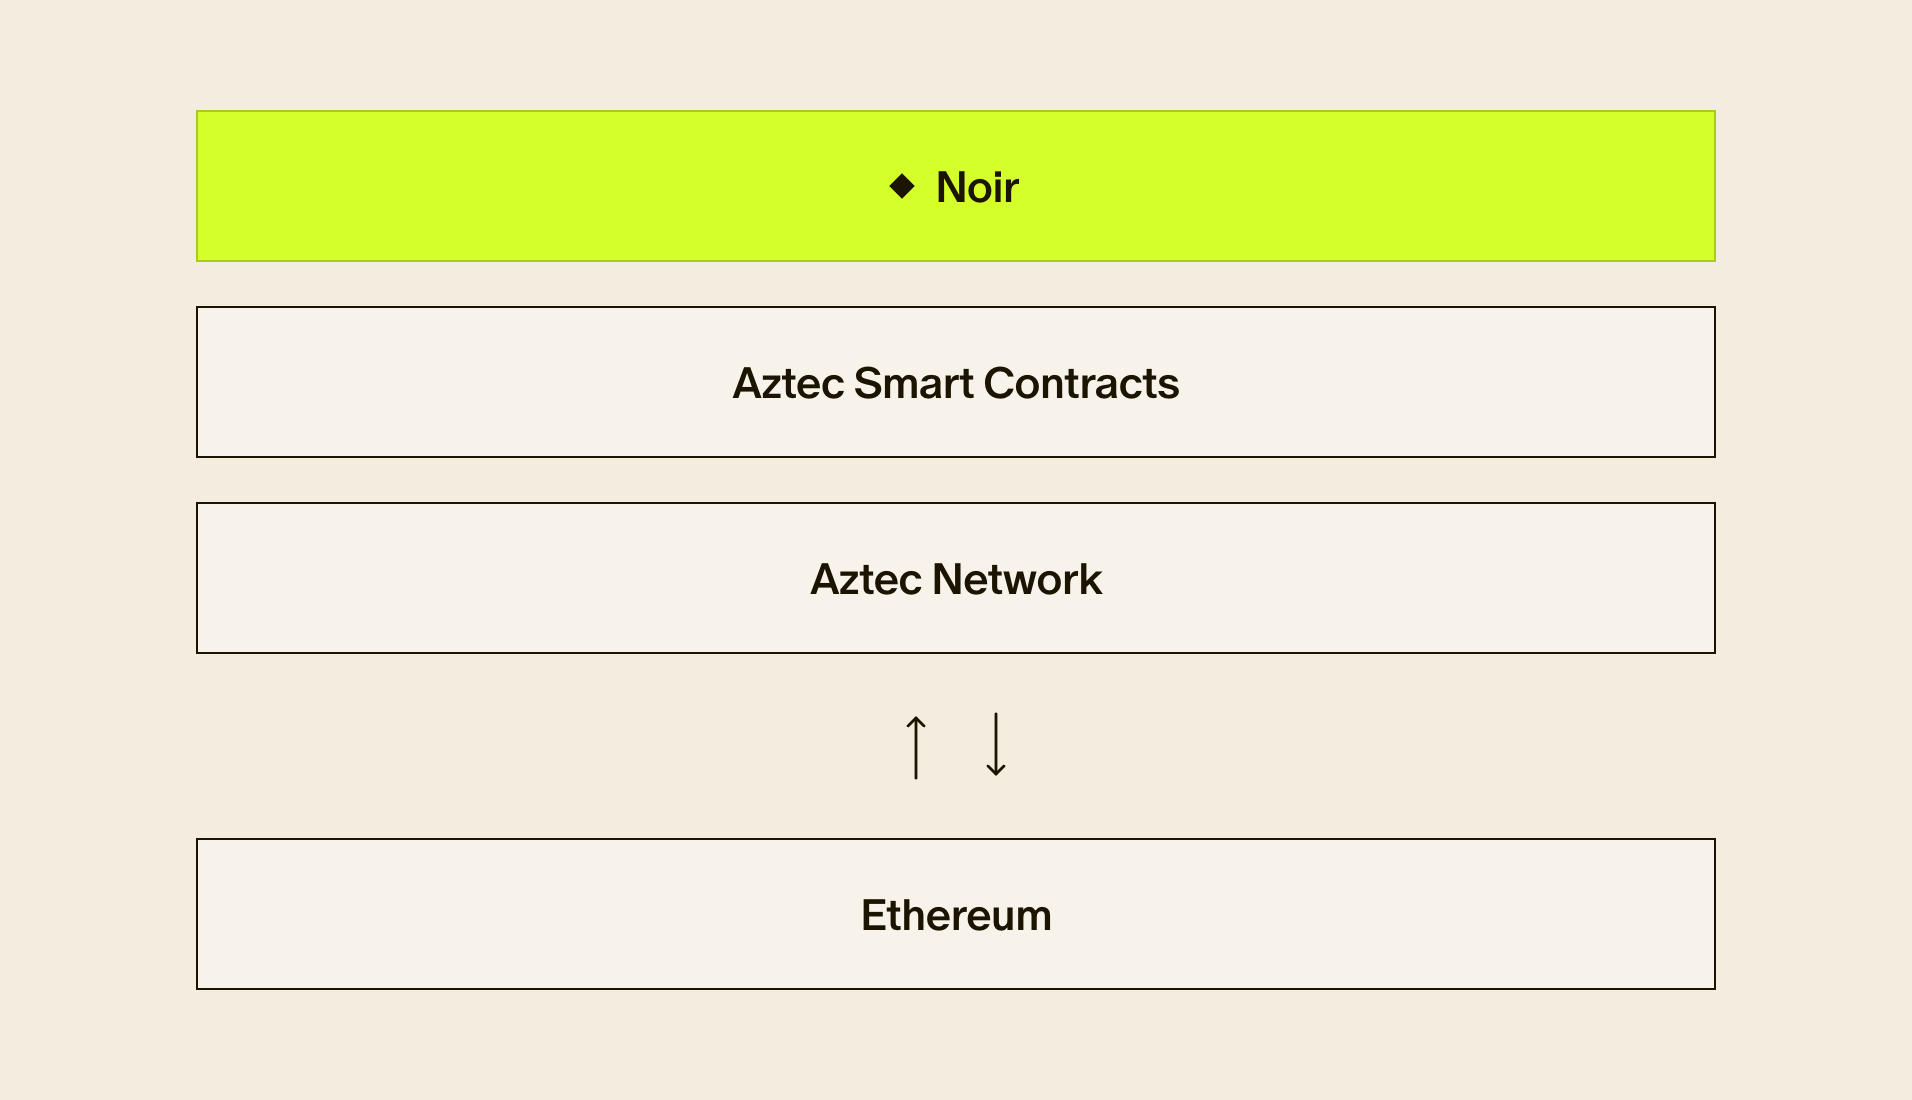
Aztec smart contracts are written in Noir, a programming language with Rust-like syntax optimized for writing private programs. Noir is an open-source project developed by Aztec and is now the industry-leading language for writing private apps using zero-knowledge proofs. Let’s dive into what Noir is, and why we use it as the building block for writing smart contracts.
Writing zk programs is extremely difficult without a background in cryptography. When developing Noir, our first goal was to create a highly optimized and easy-to-write zk Domain Specific Language (zkDSL) where developers don’t need to know any of the underlying mathematics. As a result, Noir handles all the cryptographic complexities, and will automatically convert your code into fancy zk circuits.
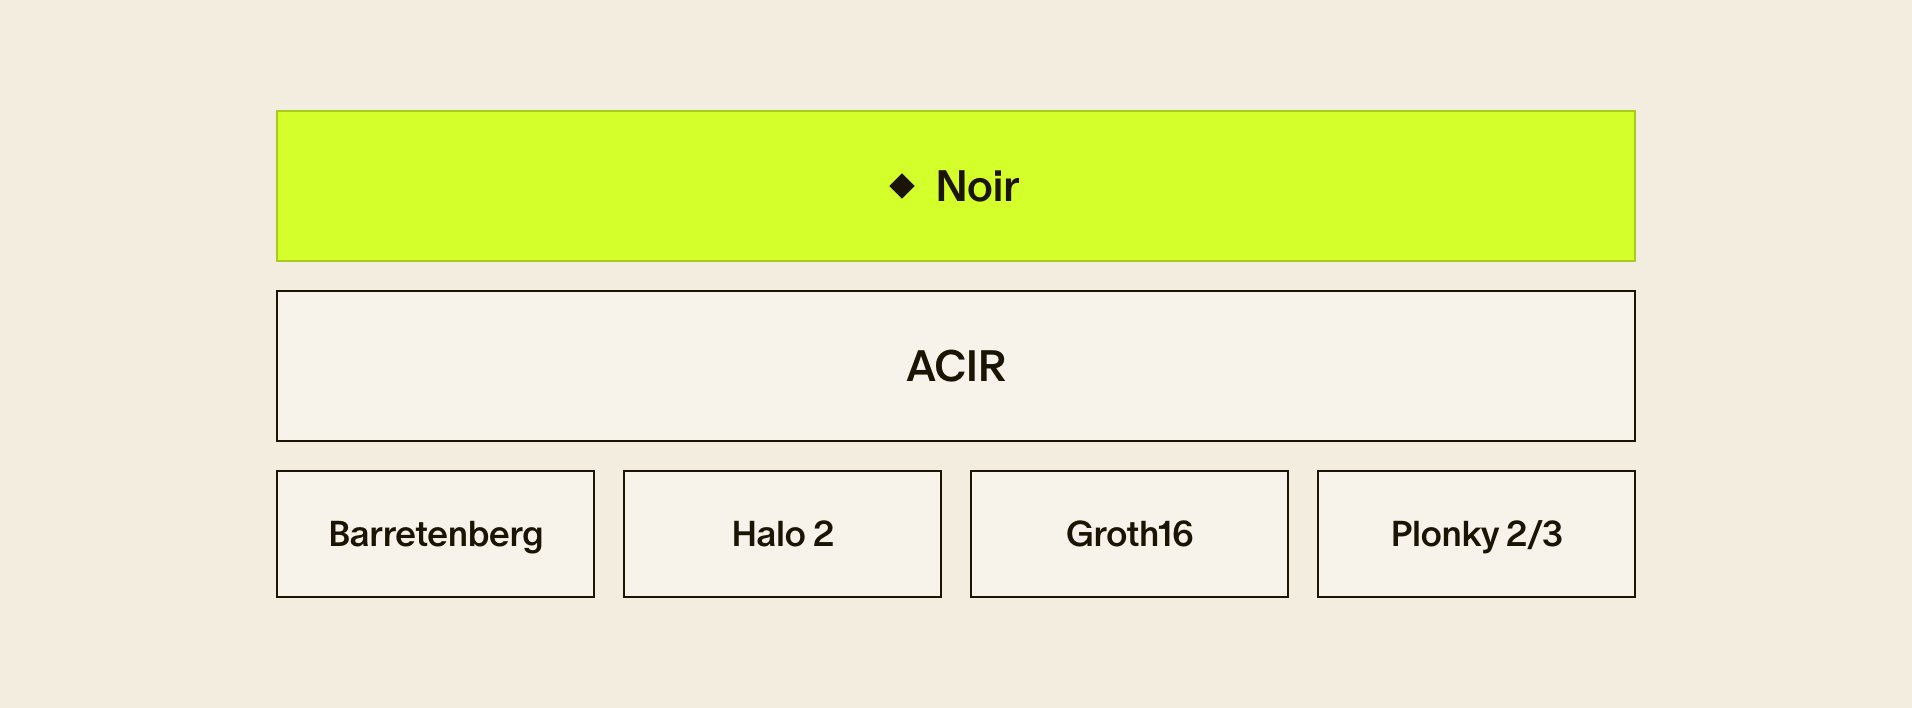
Noir compiles down to the Abstract Circuit Intermediate Representation (ACIR), an adaptable intermediary language that makes it easy to plug in a variety of popular proving backends. These proving backends, such as Aztec’s Barretenberg proving system, take the compiled zero-knowledge circuits and generate proofs attesting to the validity of the program’s execution, all without revealing any private inputs. From authorization systems that keep a password on the user's device, to complex onchain state channels with recursive proofs to verify offchain state; Noir and a proving backend handle everything from compilation to cryptography for you.
In addition to simplifying the developer experience, we also wanted to make it intuitive to specify which elements you want to keep private and which you want to make public. With Noir, privacy is baked in as a default, so all variables and functions are automatically kept completely private, and executed on the user’s device.
If you want to make any part of your code public, you can do so by simply adding a pub attribute.
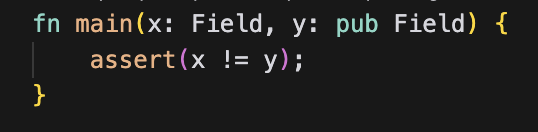
Noir on its own is great for writing programs that need to execute stateless functions, such as proving that you reside in a specific country based on passport data, or that you hold a certain number of tokens without revealing how many. Projects are already starting to build with Noir outside of Aztec on Base, Scroll, Starknet, and other chains. However, if you are looking to write privacy-preserving apps that store private state data onchain, it’s helpful to utilize a smart contract library that deliberately handles those complexities for you. That’s exactly what we’ve built at Aztec and what we’ll explore in the next section.

Aztec smart contracts leverage Noir to create apps with onchain private and public state. This section covers how smart contracts work on Aztec and how you deploy and interact with your contracts.
An Aztec smart contract is a set of public and private functions written in Noir, deployed on the Aztec Network. They are written using the Aztec.nr framework which handles all the cryptography under the hood for managing private and public state and interacting with other contracts on the network.
To build useful applications, developers need to be able to incorporate both private and public components into their contracts. For example, an onchain voting contract might want to keep the information of the voter private and prevent someone from voting twice, but publicly display how many votes have been cast, and the outcome.
Because contracts are written in Noir, this functionality is as easy as adding a ‘private’ annotation above your function. The following function will be executed privately on the user device, allowing a user to cast a vote without revealing their address:
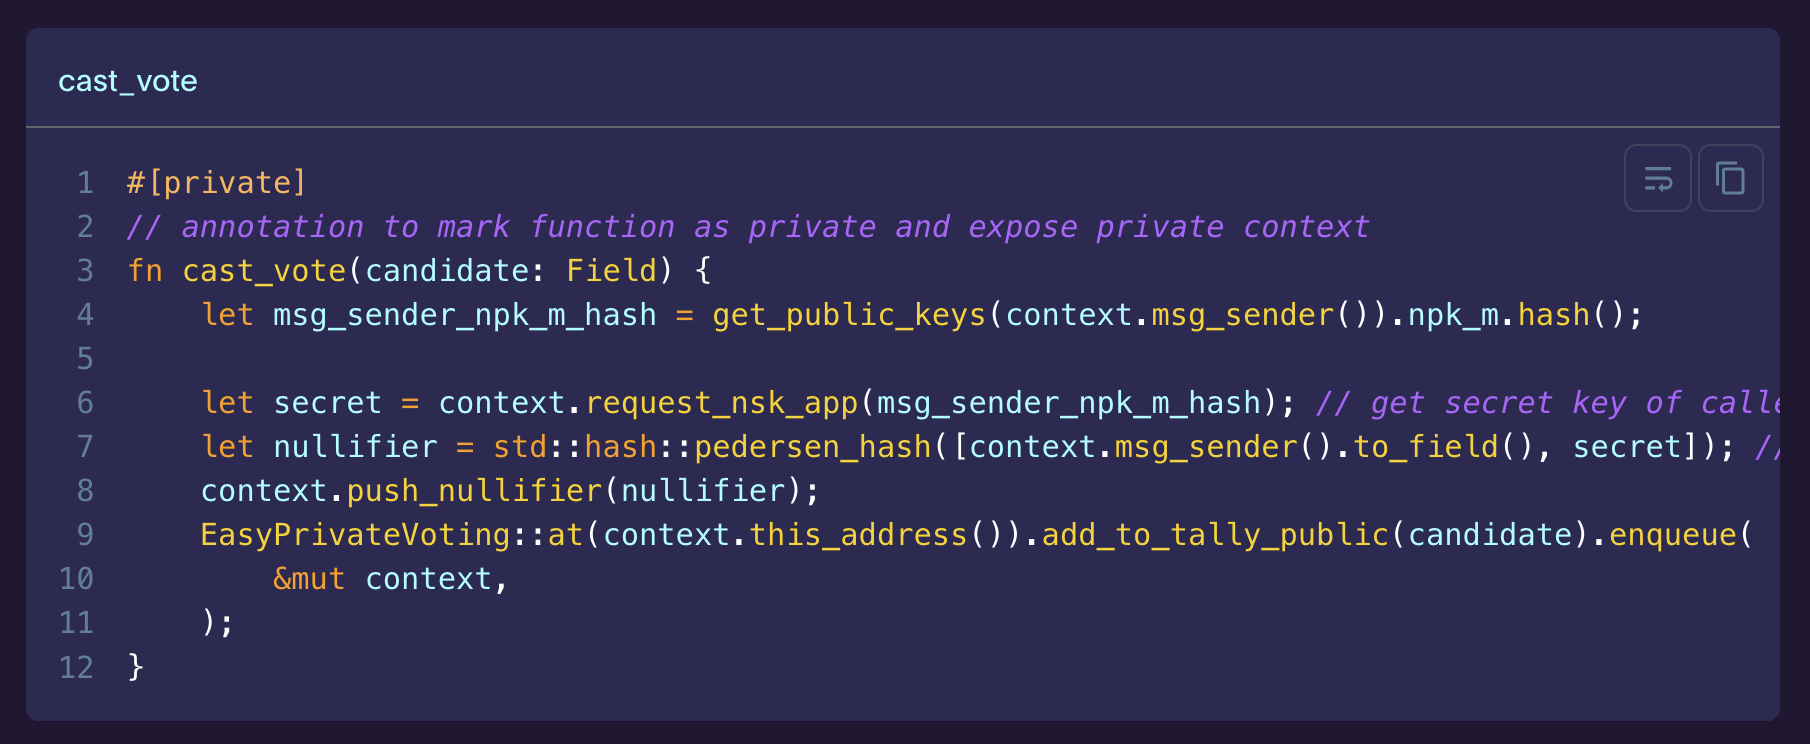
The output of this private, local execution will be sent to the network, where the correctness of execution is verified and public function calls are executed. The following function is designed to be executed publicly, adding a vote to the total tally without revealing where it came from.
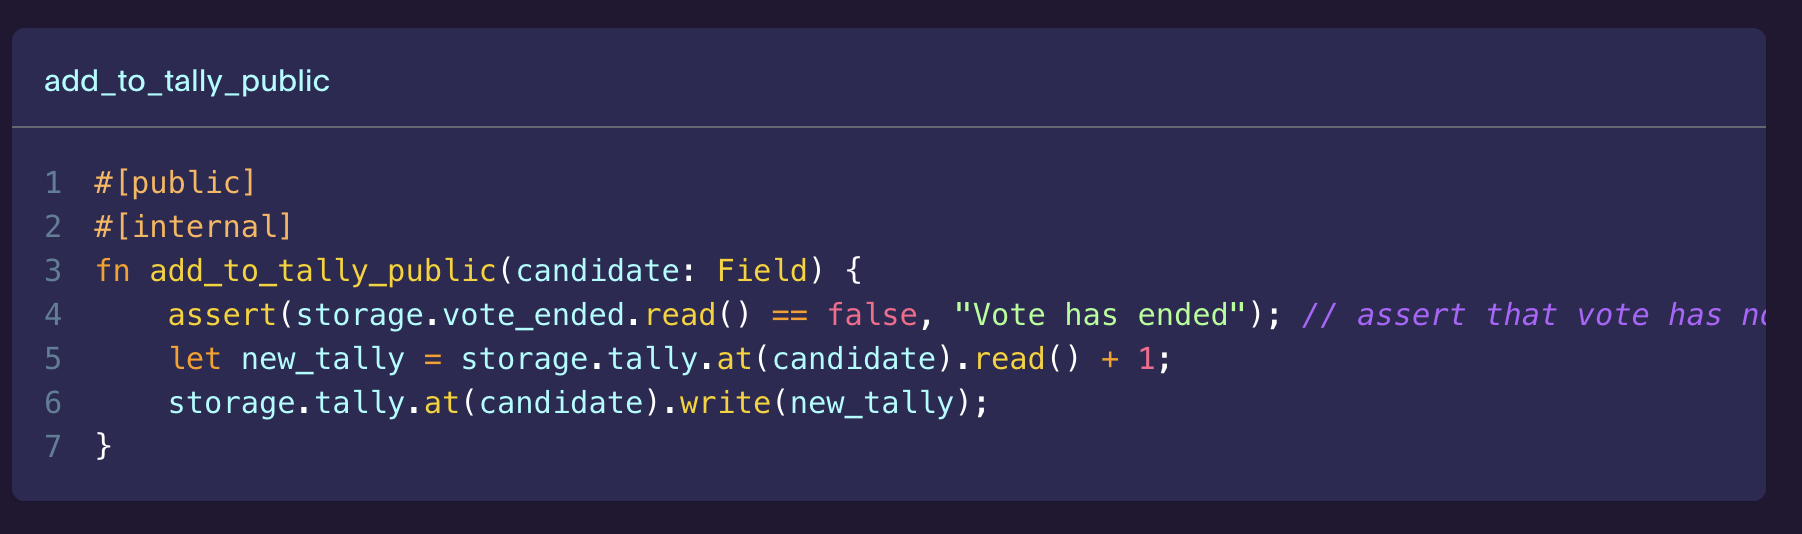
To seamlessly weave together private and public components that can easily interact with onchain state, Aztec smart contracts utilize the Aztec.nr framework to execute private functions on the user’s device and bundle the proofs for these transactions together with the public functions that will be executed by the Aztec Virtual Machine (AVM).
This framework adds the functionality needed to build onchain, privacy-preserving apps, including defining contracts, accessing private or public context, and interacting with the Aztec Network. Similar to how a vanilla Noir program would compile down into zk circuits, Aztec smart contracts are compiled into zk circuits for private functions or AVM bytecode for public functions, and stored in the Aztec contract tree.
Aztec accounts are also written as smart contracts, implementing what is known as account abstraction. Account abstraction allows application developers to create programmable accounts to dramatically improve user experience, including social recovery, sponsored transactions, and multi-factor authentication. It also makes compliance practical, allowing for granular access controls on accounts.
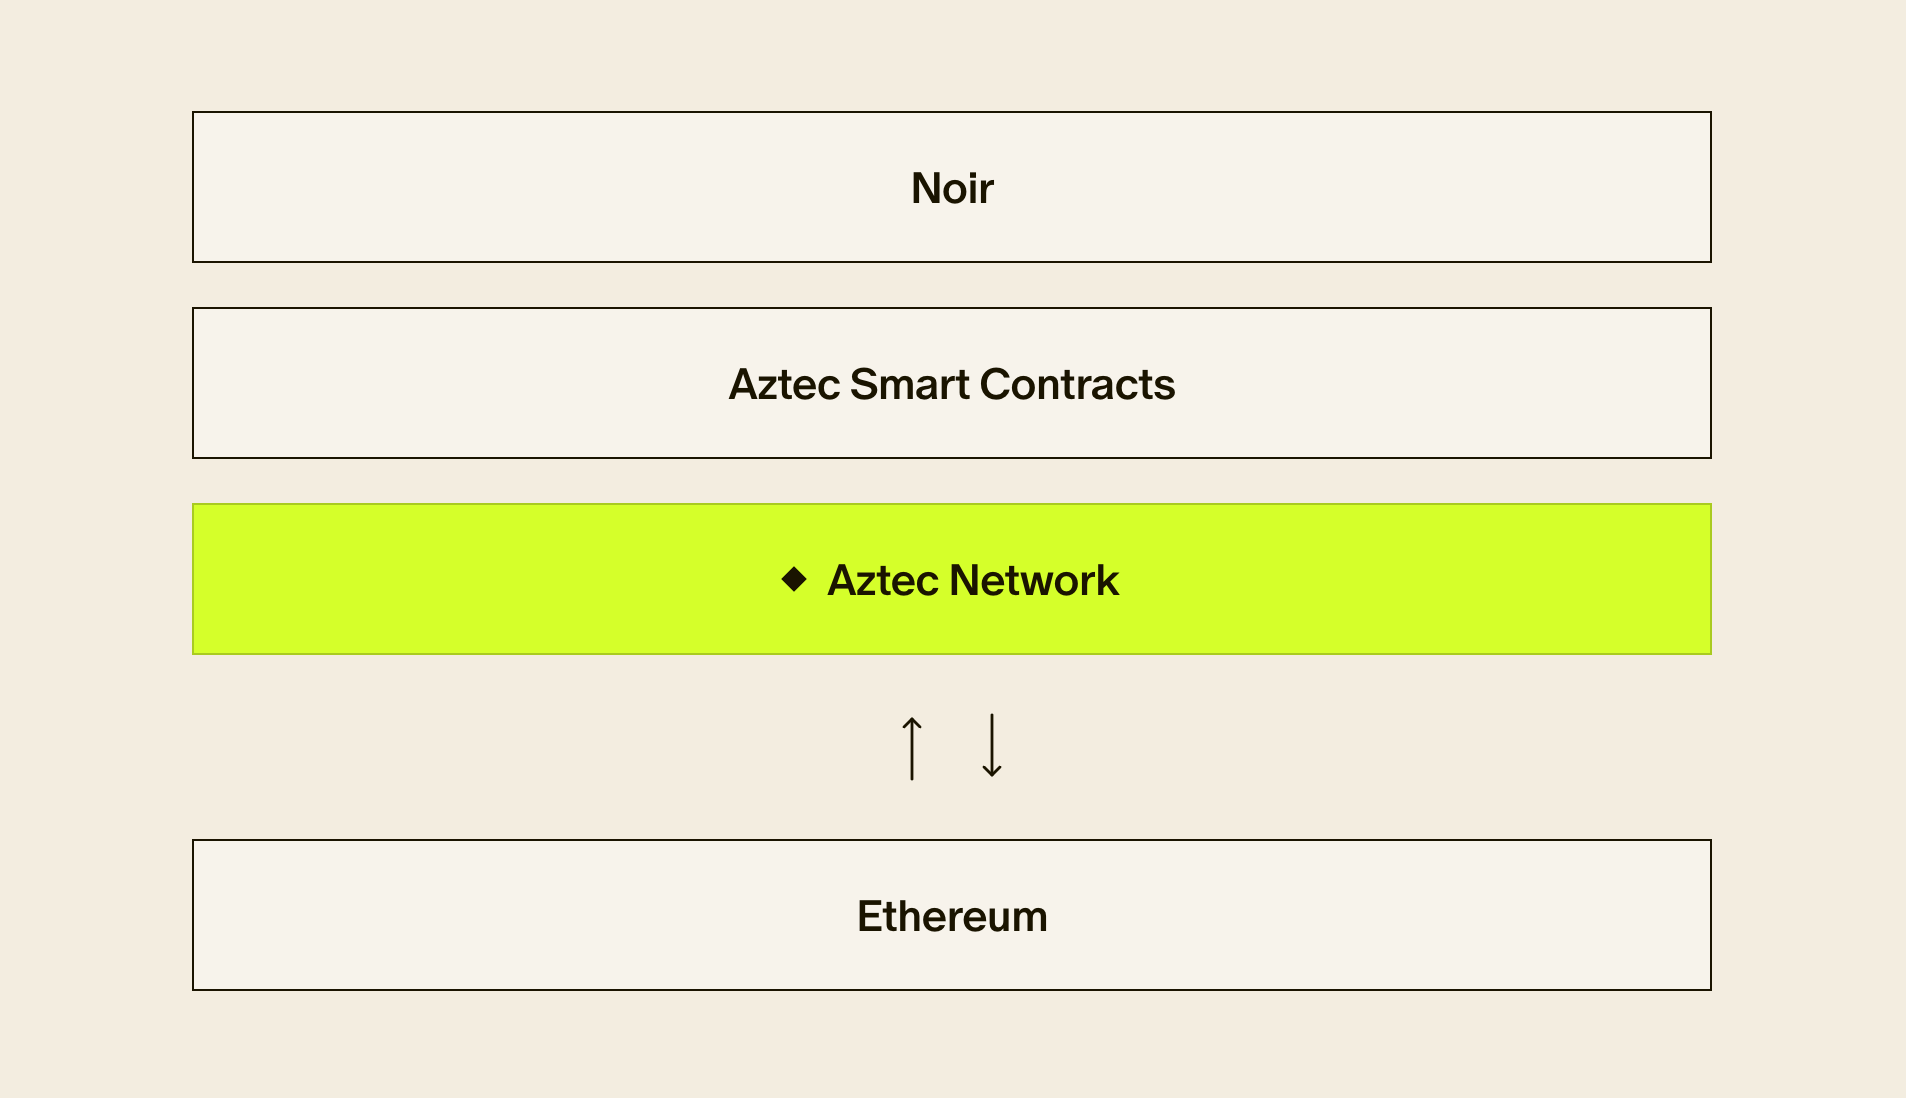
The Aztec Network is the only decentralized L2 on Ethereum. There are currently over 3,500 sequencers running the alpha network. View the live block explorer for the alpha network.
In order for a network to fully protect users and their data, it must guarantee three levels of privacy:
When you write Aztec smart contracts, everything listed above is taken care of for you. As discussed in the previous two sections, you can easily opt into privacy protections at a granular level by weaving together public and private functions.
To understand how all of these components fit together, let’s examine how a transaction is executed on the Aztec Network.
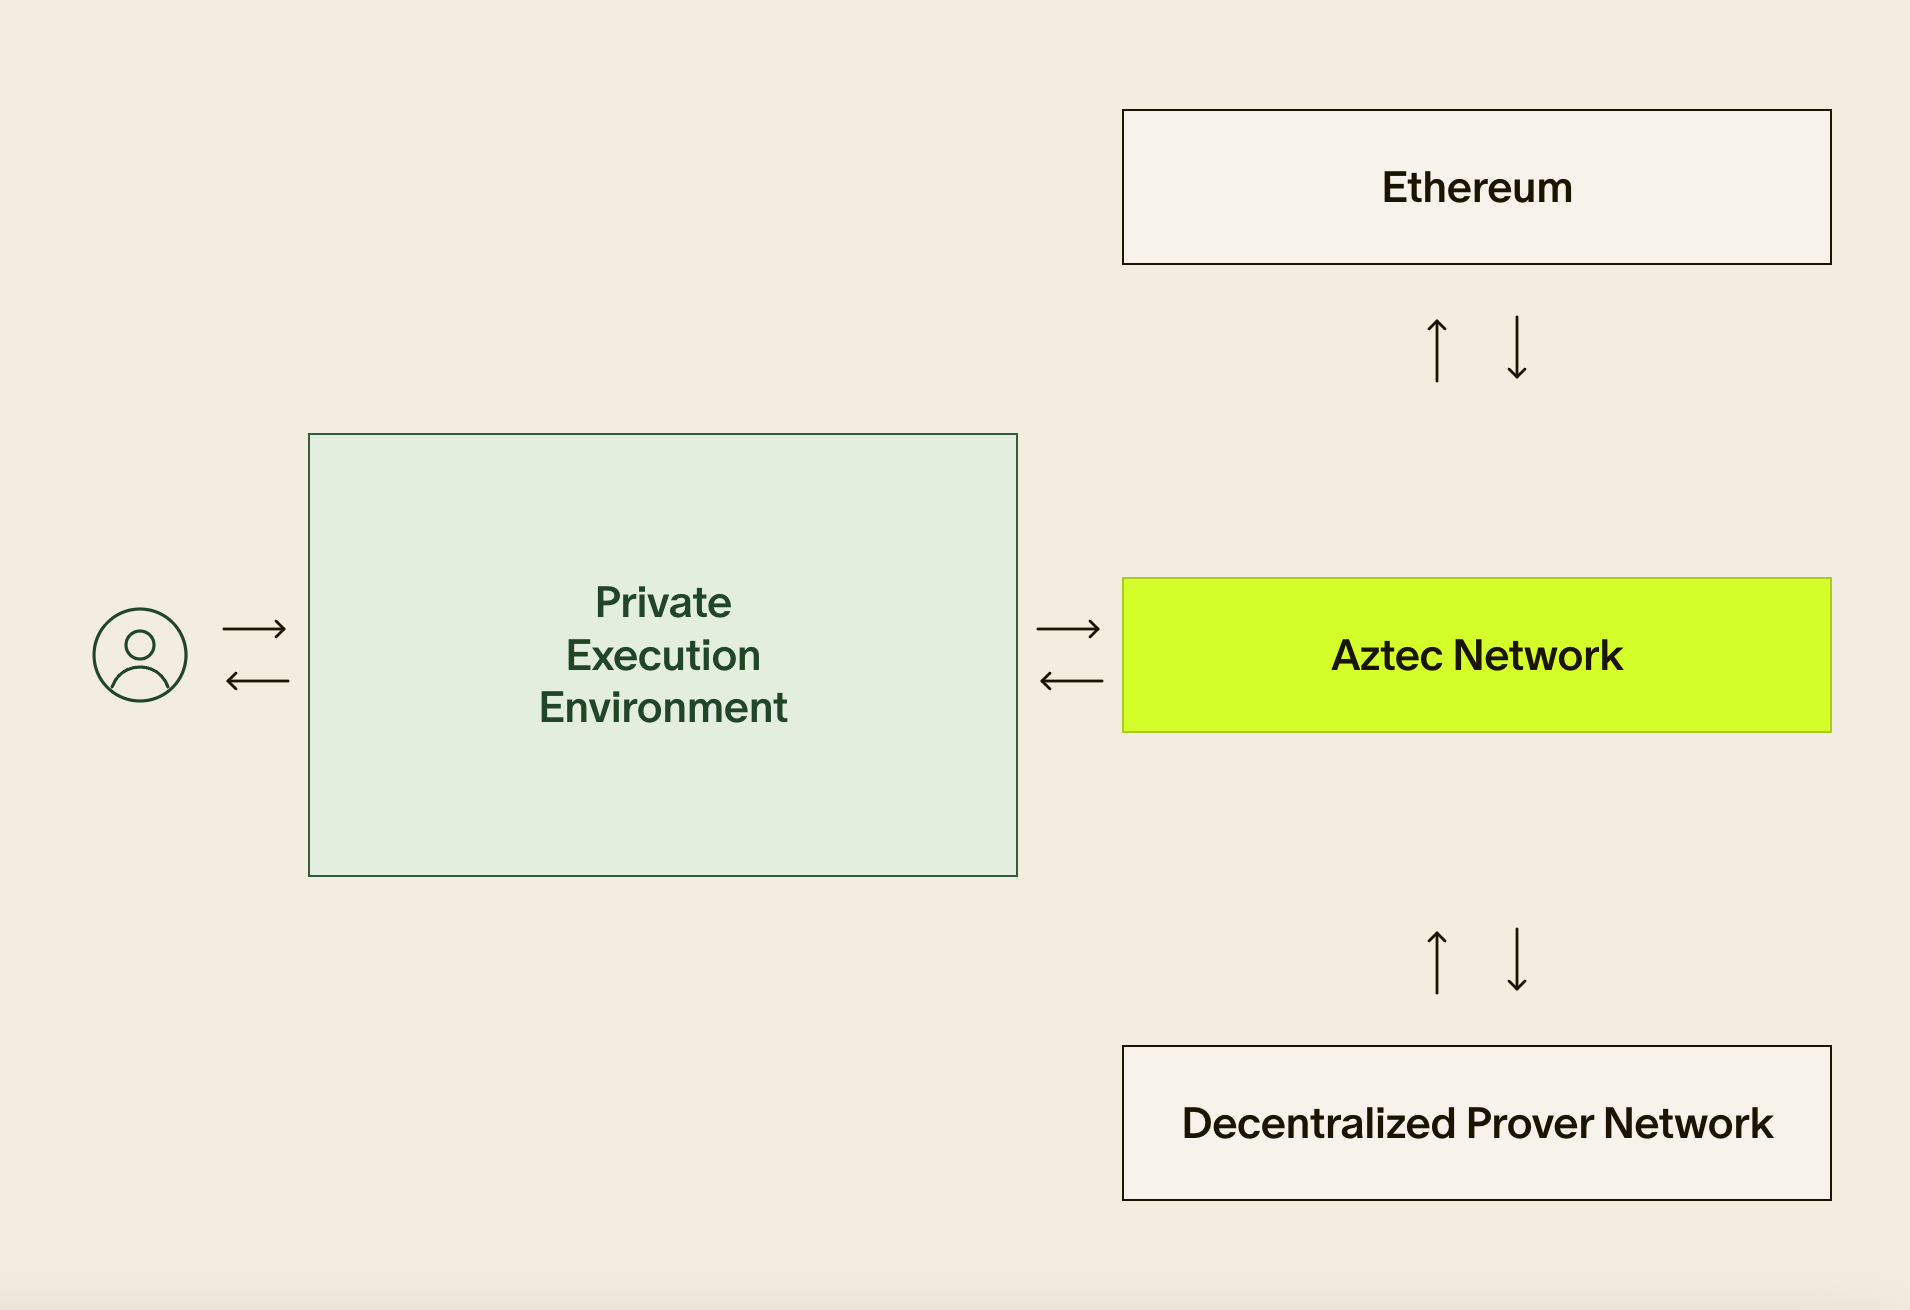
When a user interacts with your application, private functions are executed client-side on the user’s device: a phone, a personal computer, etc. This happens in a private execution environment (PXE) that is able to create highly-efficient zk proofs even on browsers and mobile devices. Any private state updates are added to the state of the network in an append-only database (UTXO tree). Because the proof is generated client-side, no information can be leaked about the inputs, outputs, accounts, or even the functions that were executed.
On the other hand, public transactions are bundled together with the private client-side proofs and sent off to the Aztec Network, powered by a decentralized network of independent community-run sequencers. Sequencers check the validity of private execution proofs, execute any public functions and update the public state, propose blocks, and publish state updates (“diffs”) to Ethereum L1. Sequencers also coordinate with a decentralized network of provers who compute the final proof for every Aztec “epoch” - defined as a contiguous sequence of 32 L2 blocks - and publish it to Ethereum. Any public functions executed by sequencers update an account-based database similar to Ethereum.
Sequencer and prover roles are fully permissionless. Anyone can spin up the required hardware and join the sequencer set or run provers and start bidding to produce proofs of Aztec epochs.
Aztec delivers on a simple but powerful idea: smart contracts on Ethereum where you choose what's public and what's private across identity, data, and compute. The four layers we've walked through are what make that possible.
Noir gives developers a Rust-like language for writing zero-knowledge programs without a cryptography background, with privacy as the default. Aztec smart contracts build on Noir through the Aztec.nr framework, letting you weave private and public functions into a single contract and use account abstraction to unlock granular access controls for compliance, tax reporting, and selective disclosure. The Aztec Network is the only decentralized L2 on Ethereum, with over 3,500 sequencers powering end-to-end programmable privacy across data, identity, and compute. And it all settles to Ethereum, inheriting L1's economic security.
The result is the first practical platform for privacy on Ethereum, and a credible candidate to become the global settlement layer of the future.
Now it's your turn to build. Head to docs.aztec.network to ship your first privacy-preserving app.
Follow Aztec on X for updates on the current state of the network.
Last week, PSE published an insightful and comprehensive user-research piece on private transfers on Ethereum. They interviewed 38 teams in the space and asked what's broken, what's missing, what builders wish they had. The list reads like a wishlist of features every privacy app on L1 is currently trying to engineer towards. It's the kind of rigorous, builder-grounded research the privacy ecosystem has needed.
We read the list. It's the list we've been building against for years.
Aztec solves all of these problems. Every requested feature already lives on Aztec. The proving system, the private contract language, the decentralized network, the privacy wallet architecture, the key model, the snark-friendliness: all of Aztec was built against this list before it was a list.
What follows is a walkthrough. For each of PSE's top technical findings, here's the feature builders are asking for, and how it works on Aztec today.
Ethereum Problem: Proof generation is too slow on user devices, especially mobile. Elliptic-curve pairing operations are a specific bottleneck. Server-side proving is a censorship and privacy leak vector. Sub-second proving was the stated threshold.
Aztec solution: Proving on Aztec runs locally in the PXE (Private eXecution Environment, pronounced "pixie"), so no data ever leaves the user's device. Chonk, our client-side zk proving system, is ruthlessly optimised for fast recursive proving on low-memory devices like phones, native and in-browser. Years of optimization have already gone in, and we're still finding more. It’s best in class and we haven’t even merged-in GPU acceleration yet!
The slow pairing checks that PSE's interviewees called out as a bottleneck aren’t a problem with Aztec; pairings are simply batched together and deferred away from the user's device, handled by the more powerful network instead, without leaking any information. With such a powerful local prover, there’s little need to outsource proving to an untrusted party.
Ethereum Problem: Verifying a ZK proof on Ethereum is prohibitively expensive. A Groth16 proof for a private transfer costs several hundred thousand L1 gas. A Halo2 (KZG Plonk) proof can cost approximately one million gas
Aztec solution: Aztec amortises L1 verification gas across all transactions in the rollup. At current network throughput, that cost is split across roughly 2,000 users per proof. Later this year, it’s slated to be split across ~20,000. Rollup costs are also partially subsidised by Aztec block rewards.
Net result: hundreds of L1 gas per user instead of millions. Plus cheap L2 gas. The user pays pennies for an Aztec transaction.
Ethereum Problem: Wrapping and unwrapping tokens leaks privacy and breaks composability. Smart contracts can't easily interact with encrypted balances. Private state is isolated; contract state is normally shared.
Aztec solution: Private state is not isolated on Aztec. The private state of one contract can be composed with that of another. This can unlock new privacy-preserving DeFi patterns directly on Aztec.
A single private transaction can call a stack of private functions across multiple contracts, with private inputs, private state transitions, and privacy over which functions were even executed and how many. Observers see that a transaction landed. They do not see what happened inside it. Stew on that for a second: a call stack of nested private functions across contracts written by different developers, each causing state transitions, all completely private.
Aztec also runs public functions, similar to Ethereum, inside the same smart contract, so you can build existing DeFi primitives on Aztec.
For Ethereum DeFi specifically, Aztec has a tidy L1-to-L2 messaging layer. Private balances can be unshielded to interact with L1 protocols and shielded back, without leaking who did the interaction and without leaky public gas payments. And for private DeFi primitives that need genuinely shared private state (state nobody knows the value of, but which anyone can mutate), people have built Aztec contracts that compose conventional Aztec private state with co-snark or FHE sidecars.
Private and public state are peers inside a single Aztec smart contract. Builders mix and match.
Ethereum Problem: Entry and exit points are the dominant privacy leak, not the protocol itself. Depositing and quickly withdrawing makes identity analysis trivial.
Aztec solution: The main fix is to stop crossing the boundary so often. (Or even if you do cross the boundary, Aztec has leakage protections).
Imagine if thousands of private smart contracts lived on the same network and could call each other without leaking which contracts were called, which arguments were passed, or what was returned. Imagine they all shared one global note tree and one global nullifier tree. That's Aztec. Once funds are inside, users don't need to keep crossing the private/public boundary to do useful things: Aztec is its own rich environment for composable, private execution of smart contracts.
Even when a private function does need to call a public function – be it an L1 DeFi contract, or a native public function within Aztec – the developer controls the information they reveal; not the protocol. The call can even be "incognito" to hide msg_sender. A single environment for many private apps to thrive also means re-usable tooling for builders.
Ethereum Problem: Privacy features (per-dapp addresses, private transfers) aren't natively integrated into major wallets. Reliance on dapp-specific UIs damages UX.
Aztec solution: Ethereum wallets weren't built for any of this, and they don't need to be: the chain underneath them has no private state to protect. Aztec wallets are an entirely new category of software.
Aztec wallets are able to manage all these new privacy-centric concepts:
Aztec wallets are in active development, and this is an area where we expect many teams to build different wallets that are customized to various user needs. An early wallet is already baked into the protocol for developers to start using today.
Ethereum Problem: Encrypted tokens and many privacy protocols depend on external networks for encryption, decryption, or relaying. Threshold-decryption committees and TEE hardware vendors are added trust assumptions on top of the chain itself.
Aztec solution: Aztec's private and public execution environments are not reliant on external networks. Aztec is its own decentralised network: ~4,000 validators stake on it, block proposers are randomly selected, a random committee attests, and a decentralised set of provers proves the rollup's execution. Validity is ultimately backed by cryptographic proofs settled on Ethereum.
External networks (co-snark networks, TEEs, MPC or FHE sidecars) become an opt-in choice for the specific case of private shared state. The trust tradeoffs there are something the contract developer signs up for explicitly, not a tax every user pays on every transaction by default.
Ethereum Problem: Keccak is inefficient to prove inside ZK circuits. There is no native support for a ZK-friendly hash like Poseidon.
Aztec solution: Poseidon2 is enshrined across the entire Aztec protocol, for rapid proving of every tx. Every Aztec state tree, the proving system, the innards of the protocol; everywhere. Reading and writing state inside a circuit is as cheap as it gets.
Keccak, SHA, and Blake hashes are still available through optimised Noir libraries when contracts need them for L1 interoperability. The default is ZK-friendly; the L1-friendly hashes are there when you reach for them.
Ethereum Problem: Syncing private state (scanning for incoming notes and events) is a client-side bottleneck. Users wait for scans to complete before seeing their balance. Tachyon-style oblivious sync was cited as a path forward.
Aztec solution: Brute-force syncing of private state is rarely needed. Most real-world use cases involve a sender and recipient who can establish a shared secret offchain first.
From that shared secret, both parties can derive a sequence of random-looking “tags”. Each encrypted note log is prepended with the next tag in the sequence. The recipient already knows the next tag, so they know exactly what to query. Note discovery happens in seconds, not minutes. The scheme slots cleanly into PIR or mixnet approaches for extra privacy on the query itself, and smart contracts that don't trust senders to use the correct tag can just constrain it inside the circuit.
That’s not to say that Aztec requires interactivity between all senders and recipients. For genuinely non-interactive use cases (recipient can't talk to the sender before the transfer), Aztec enables devs to customize both their log emission and their note-discovery logic however they like. (Aztec also has ways to speed up the brute-force scanning approach from "scan the whole chain" to "scan a tiny subset of non-interactive handshake txs"
Ethereum Problem: Shielded pools are fragmented across dapps and chains, reducing the effective privacy set for all users. Each new privacy protocol must bootstrap its own.
Aztec solution: There is one global note tree and one global nullifier tree on Aztec, shared by every smart contract on the network. Every private app contributes to and draws from the same privacy set. No per-app bootstrap. No walled gardens.
Private payments, private swaps, lending, payroll, treasury, identity attestations: all of them land in the same global commitment set, by construction.
Ethereum Problem: Ethereum developer tooling lacks support for private transfers and private state. Standards for private tokens, compliance, and wallet interactions are missing. Many privacy teams are small, with short runway and expensive audits.
Aztec solution: Aztec ships the full toolchain for private contracts: Noir for writing private logic, the Aztec smart contract framework with macros that hide the protocol mess so devs can focus on app logic, the PXE for keys / state / syncing / proof generation, a JS SDK, a local node for testing, a CLI, and a real, live, decentralised L2.
The mental overhead of building a privacy protocol on Aztec collapses to "just write the app logic." Here is an example of a complete private transfer function on Aztec:
#[authorize_once("from", "authwit_nonce")]
#[external("private")]

fn transfer_in_private(from: AztecAddress, to: AztecAddress, amount: u128, authwit_nonce: Field) {
    self.storage.balances.at(from).sub(amount).deliver(MessageDelivery.ONCHAIN_CONSTRAINED);
    self.storage.balances.at(to).add(amount).deliver(MessageDelivery.ONCHAIN_CONSTRAINED);
}
Look at how simple that is.
A two-line function body.
Two lines.
Aztec takes care of the rest.
Behind those #[...] macros, the framework handles: caller authorisation, note syncing, fetching notes from the user's private db, Merkle membership proofs against the global note tree, safe nullifier creation (without leaking master secrets to the circuit), randomness for new notes, encrypted ciphertext generation, log tagging for fast recipient discovery, and public-input population. The PXE handles key management, private state, and proof generation. The smart contract itself contains its own message-processing logic for log discovery, decryption, and storage on the recipient side.
If you want whitelists, blacklists, association sets, custom tx authorisation, viewing-key hierarchies, temporary view access, selective disclosure to specific counterparties, just import a Noir library. Want something more adventurous than private payments? Same toolchain.
PSE's findings are not ten unrelated bugs. They're the same problem refracted ten ways: privacy retrofitted onto a chain that was not designed for it yields bad tradeoffs.
Aztec was designed against this list before it was a list. One global note tree and one global nullifier tree. Private and public state inside the same contract. Compose calls between private contracts without leaking anything. Fast client-side proving on phones via Chonk. Snark-friendliness everywhere. Rollup-amortised L1 gas costs, fractions of a cent per user. Native account abstraction with private fee paymasters. No painfully slow private state syncing: a tagging-based note discovery scheme that runs in seconds. An entirely new category of wallet that treats privacy as a first-class concern. Simple, high-level smart contract syntax that collapses a basic private token transfer function into two lines.
There were 10 privacy features Ethereum devs wanted, all of them live on Aztec. The infrastructure is in place. Build the thing.
Aztec is the blockchain that solved the privacy problem. Start at docs.aztec.network or read the architecture deep-dive on The Best of Both Worlds: How Aztec Blends Private and Public State.
Alpha is live: a fully feature-complete, privacy-first network. The infrastructure is in place, privacy is native to the protocol, and developers can now build truly private applications.
Nine years ago, we set out to redesign blockchain for privacy. The goal: create a system institutions can adopt while giving users true control of their digital lives. Privacy band-aids are coming to Ethereum (someday), but it’s clear we need privacy now, and there’s an arms race underway to build it. Privacy is complex, it’s not a feature you can bolt-on as an afterthought. It demands a ground-up approach, deep tech stack integration, and complete decentralization.
In November 2025, the Aztec Ignition Chain went live as the first decentralized L2 on Ethereum, it’s the coordination layer that the execution layer sits on top of. The network is not operated by the Aztec Labs or the Aztec Foundation, it’s run by the community, making it the true backbone of Aztec.
With the infrastructure in place and a unanimous community vote, the network enters Alpha.
Alpha is the first Layer 2 with a full execution environment for private smart contracts. All accounts, transactions, and the execution itself can be completely private. Developers can now choose what they want public and what they want to keep private while building with the three privacy pillars we have in place across data, identity, and compute.
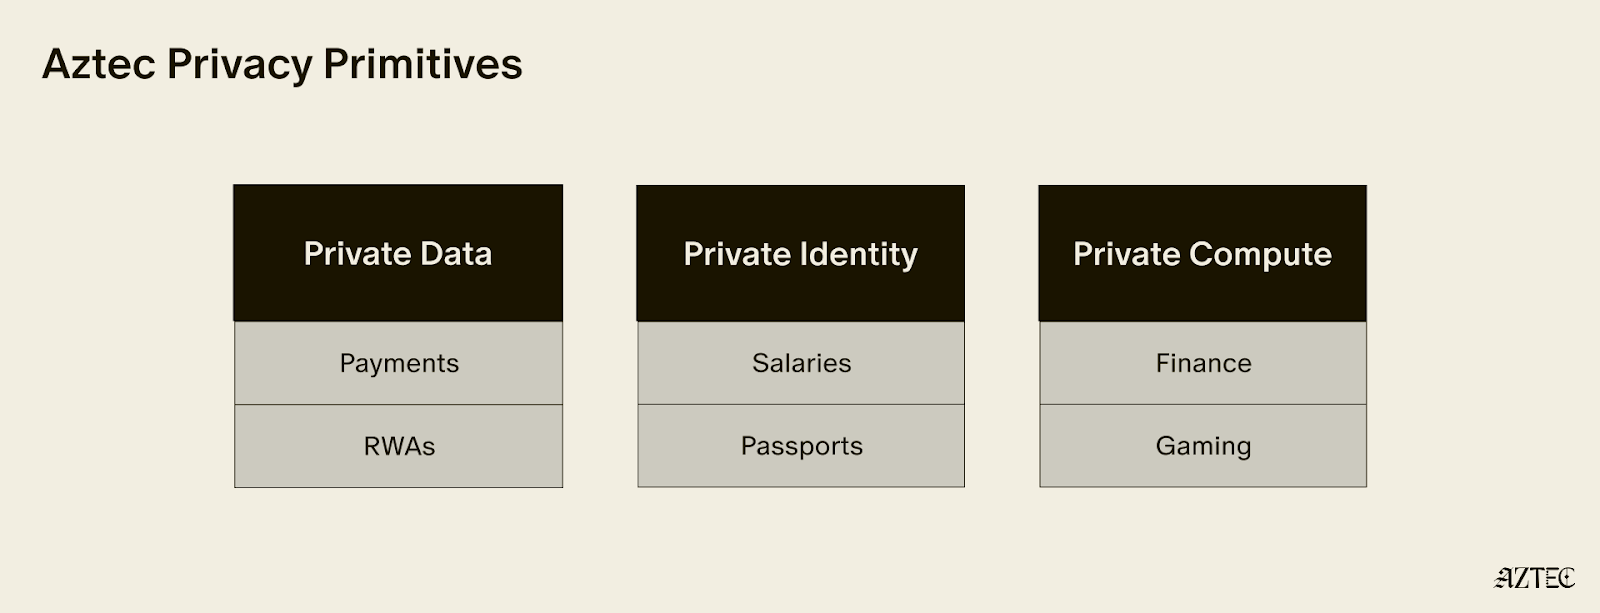
These privacy pillars, which can be used individually or combined, break down into three core layers:
Alpha is feature complete–meaning this is the only full-stack solution for adding privacy to your business or application. You build, and Aztec handles the cryptography under the hood.
It’s Composable. Private-preserving contracts are not isolated; they can talk to each other and seamlessly blend both private and public state across contracts. Privacy can be preserved across contract calls for full callstack privacy.
No backdoor access. Aztec is the only decentralized L2, and is launching as a fully decentralized rollup with a Layer 1 escape hatch.
It’s Compliant. Companies are missing out on the benefits of blockchains because transparent chains expose user data, while private networks protect it, but still offer fully customizable controls. Now they can build compliant apps that move value around the world instantly.
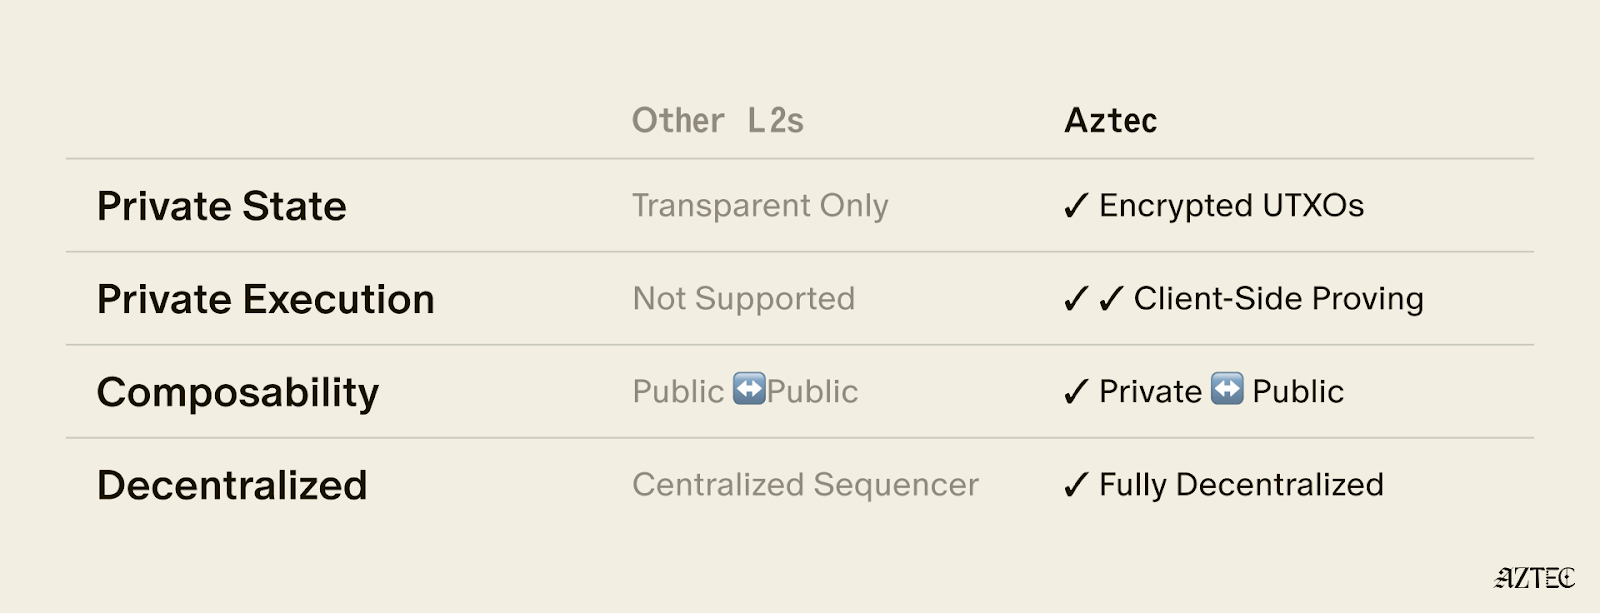
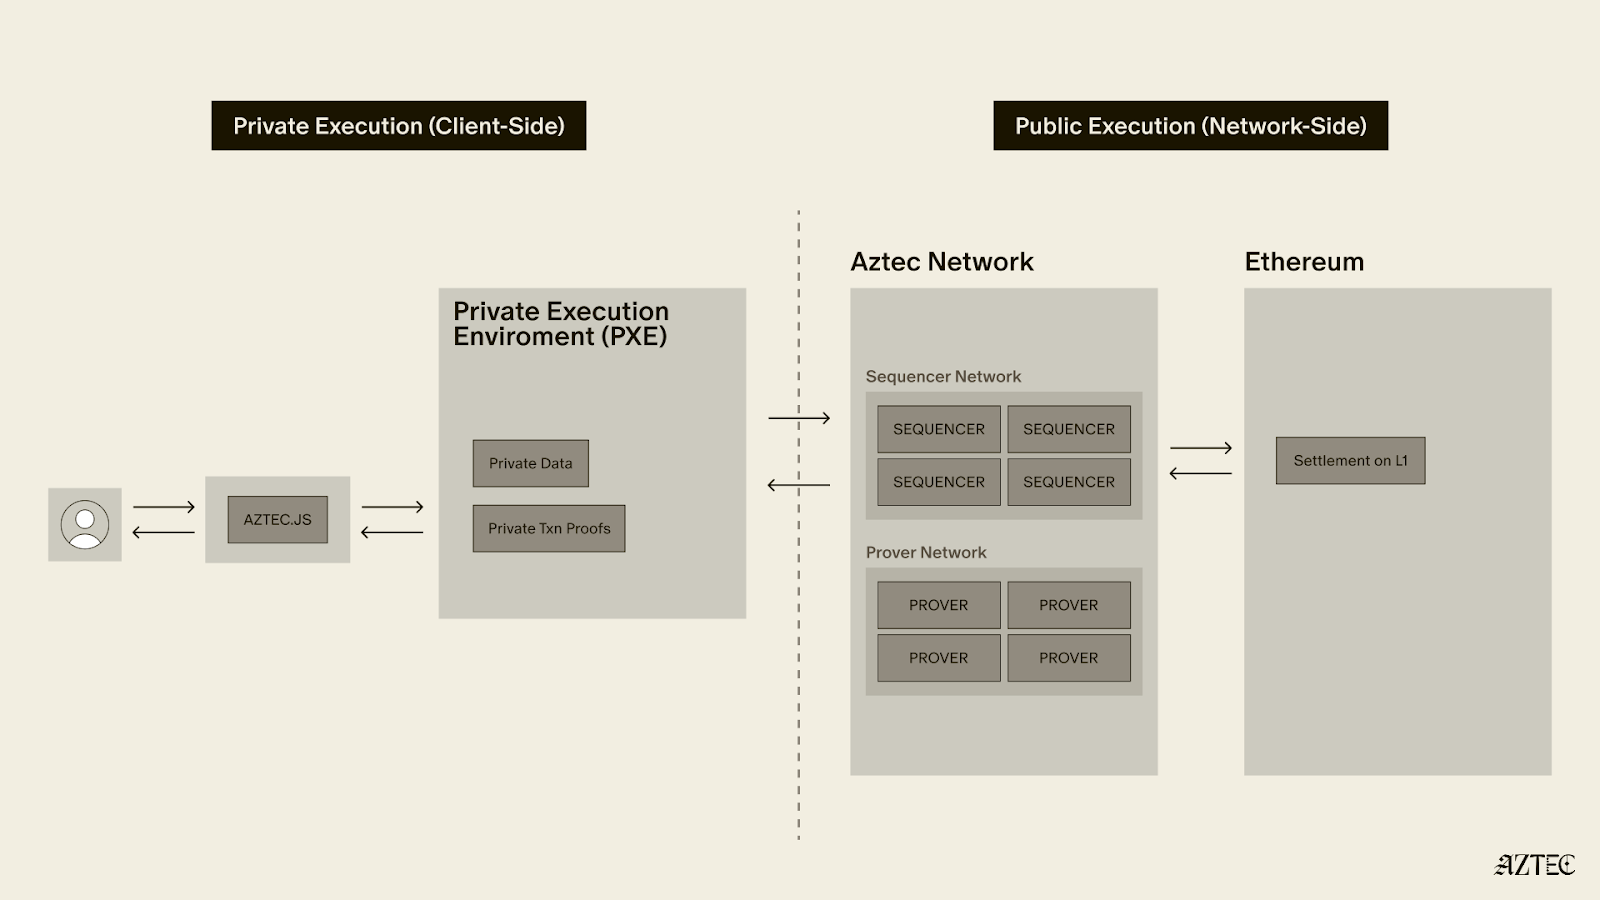
Developers can explore our privacy primitives across data, identity, and compute and start building with them using the documentation here. Note that this is an early version of the network with known vulnerabilities, see this post for details. While this is the first iteration of the network, there will be several upgrades that secure and harden the network on our path to Beta. If you’d like to learn more about how you can integrate privacy into your project, reach out here.
To hear directly from our Cofounders, join our live from Cannes Q&A on Tuesday, March 31st at 9:30 am ET. Follow us on X to get the latest updates from the Aztec Network.
On Wednesday 17 March 2026 our team discovered a new vulnerability in the Aztec Network. Following the analysis, the vulnerability has been confirmed as a critical vulnerability in accordance with our vulnerability matrix.
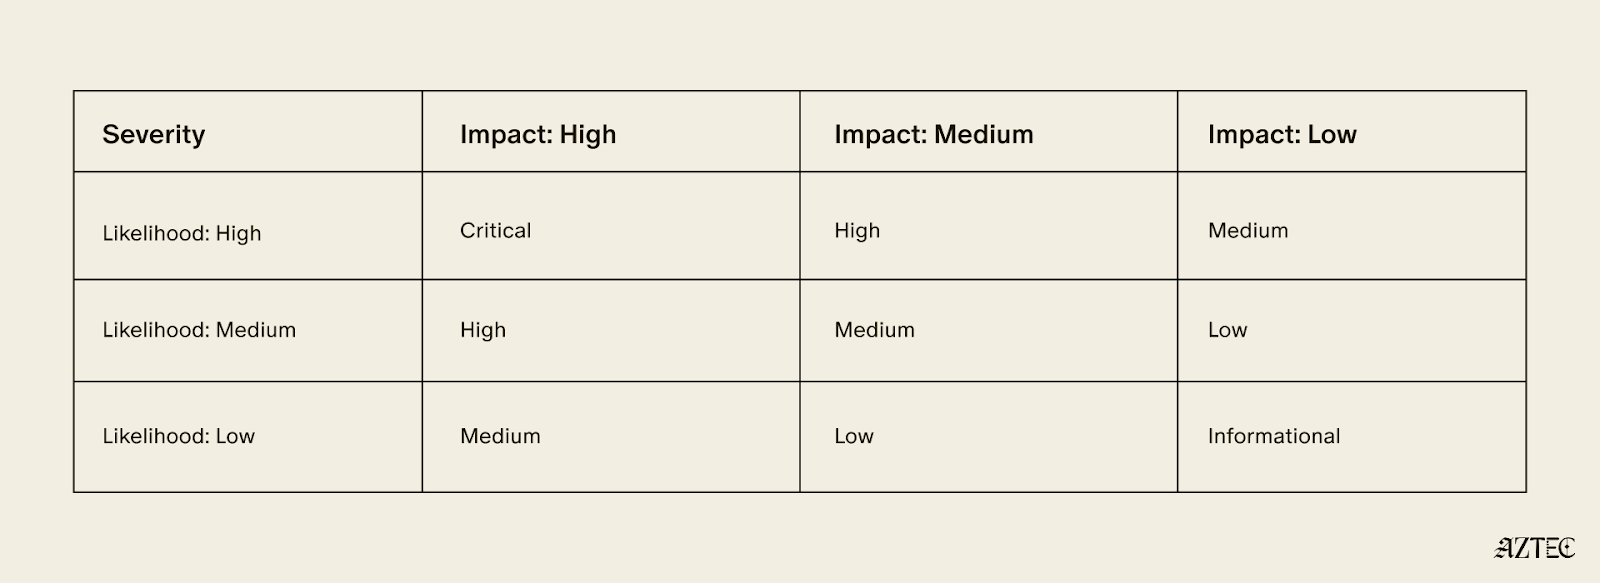
The vulnerability affects the proving system as a whole, and is not mitigated via public re-execution by the committee of validators. Exploitation can lead to severe disruption of the protocol and theft of user funds.
In accordance with our policy, fixes for the network will be packaged and distributed with the “v5” release of the network, currently planned for July 2026.
The actual bug and corresponding patch will not be publicly disclosed until “v5.”
Aztec applications and portals bridging assets from Layer 1s should warn users about the security guarantees of Alpha, in particular, reminding users not to put in funds they are not willing to lose. Portals or applications may add additional security measures or training wheels specific to their application or use case.
We will shortly establish a bug tracker to show the number and severity of bugs known to us in v4. The tracker will be updated as audits and security researchers discover issues. Each new alpha release will get its own tracker. This will allow developers and users to judge for themselves how they are willing to use the network, and we will use the tracker as a primary determinant for whether the network is ready for a "Beta" label.
We have identified a vulnerability in barretenberg allowing inclusion of incorrect proofs in the Aztec Network mempool, and ask all nodes to upgrade to versions v.4.1.2 or later.
We’d like to thank Consensys Diligence & TU Vienna for a recent discovery of a separate vulnerability in barretenberg categorized as medium for the network and critical for Noir:
We have published a fixed version of barretenberg.
We’d also like to thank Plainshift AI for discovery, reproduction, and reporting of one more vulnerability in the Aztec Network and their ongoing work to help secure the network.