Aztec Network
Oct 8th, 2025
•
## min read

Aztec: The Private World Computer

Building a fully decentralized, privacy-preserving network to unlock the next Renaissance.

Share
Written by
David Steinrueck
Rahul Kothari
Edited by
Kelsey Ruiz

Privacy has emerged as a major driver for the crypto industry in 2025. We’ve seen the explosion of Zcash, the Ethereum Foundation’s refocusing of PSE, and the launch of Aztec’s testnet with over 24,000 validators powering the network. Many apps have also emerged to bring private transactions to Ethereum and Solana in various ways, and exciting technologies like ZKPassport that privately bring identity on-chain using Noir have become some of the most talked about developments for ushering in the next big movements to the space. 

Underpinning all of these developments is the emerging consensus that without privacy, blockchains will struggle to gain real-world adoption. 

Without privacy, institutions can’t bring assets on-chain in a compliant way or conduct complex swaps and trades without revealing their strategies. Without privacy, DeFi remains dominated and controlled by advanced traders who can see all upcoming transactions and manipulate the market. Without privacy, regular people will not want to move their lives on-chain for the entire world to see every detail about their every move. 

While there's been lots of talk about privacy, few can define it. In this piece we’ll outline the three pillars of privacy and gives you a framework for evaluating the privacy claims of any project. 

The Three Pillars of Privacy 

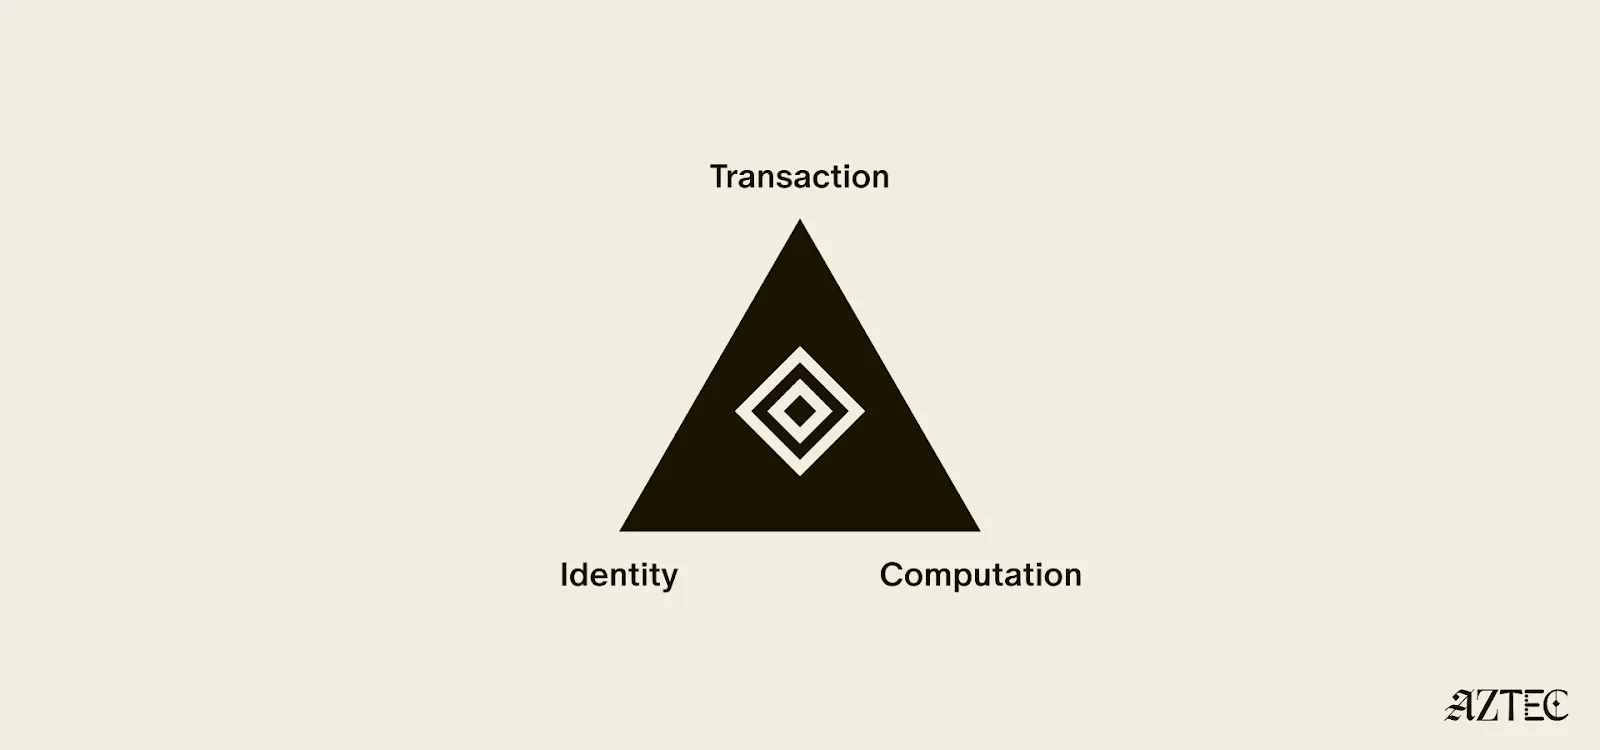
True privacy rests on three essential pillars: transaction privacy, identity privacy, and computational privacy. It is only when we have all three pillars that we see the emergence of a private world computer. 

Transaction: What is being sent?

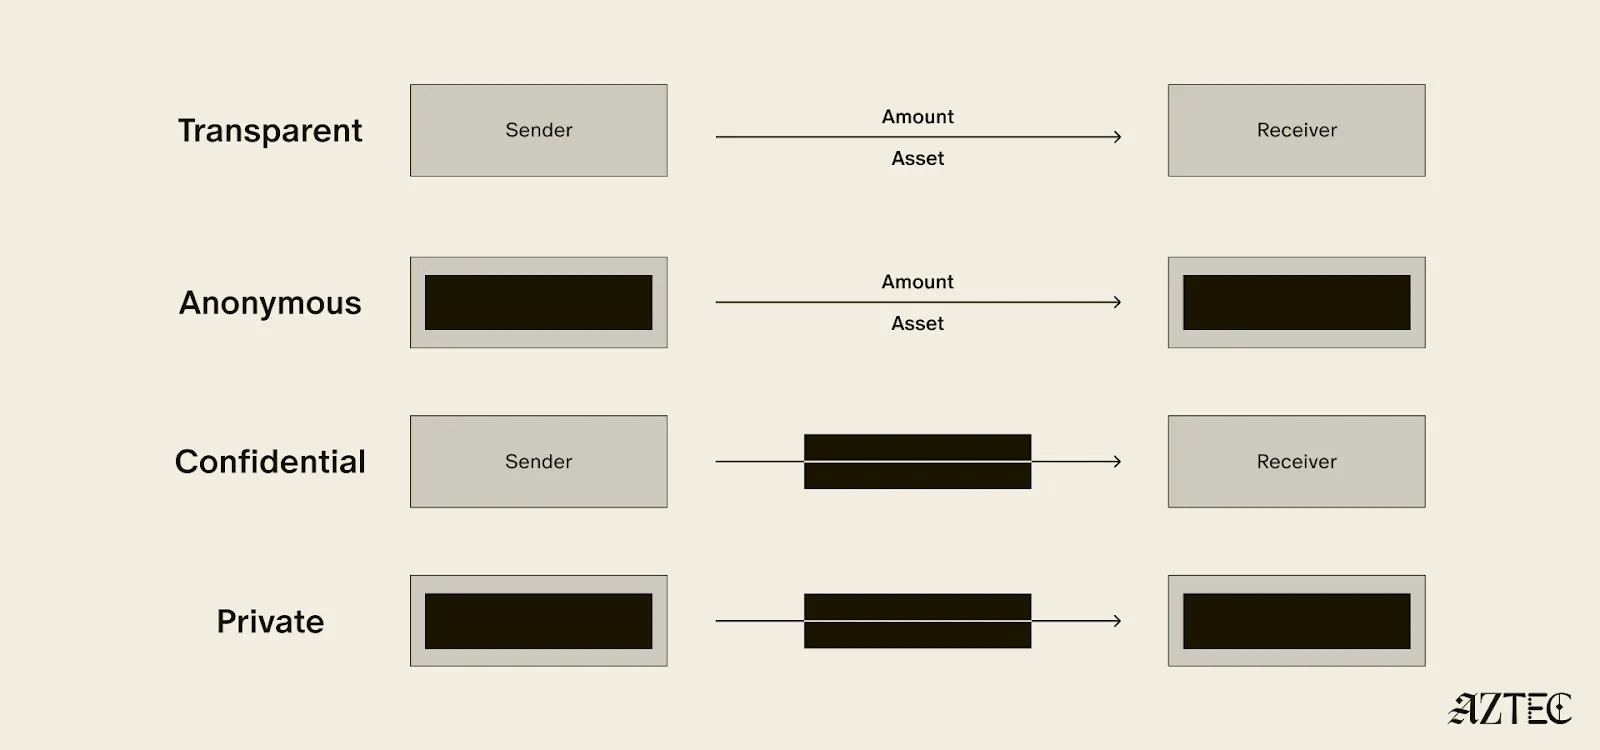
Transaction privacy means that both inputs and outputs are not viewable by anyone other than the intended participants. Inputs include any asset, value, message, or function calldata that is being sent. Outputs include any state changes or transaction effects, or any transaction metadata caused by the transaction. Transaction privacy is often primarily achieved using a UTXO model (like Zcash or Aztec’s private state tree). If a project has only the option for this pillar, it can be said to be confidential, but not private. 

Identity: Who is involved?

Identity privacy means that the identities of those involved are not viewable by anyone other than the intended participants. This includes addresses or accounts and any information about the identity of the participants, such as tx.origin, msg.sender, or linking one’s private account to public accounts. Identity privacy can be achieved in several ways, including client-side proof generation that keeps all user info on the users’ devices. If a project has only the option for this pillar, it can be said to be anonymous, but not private. 

Computation: What happened? 

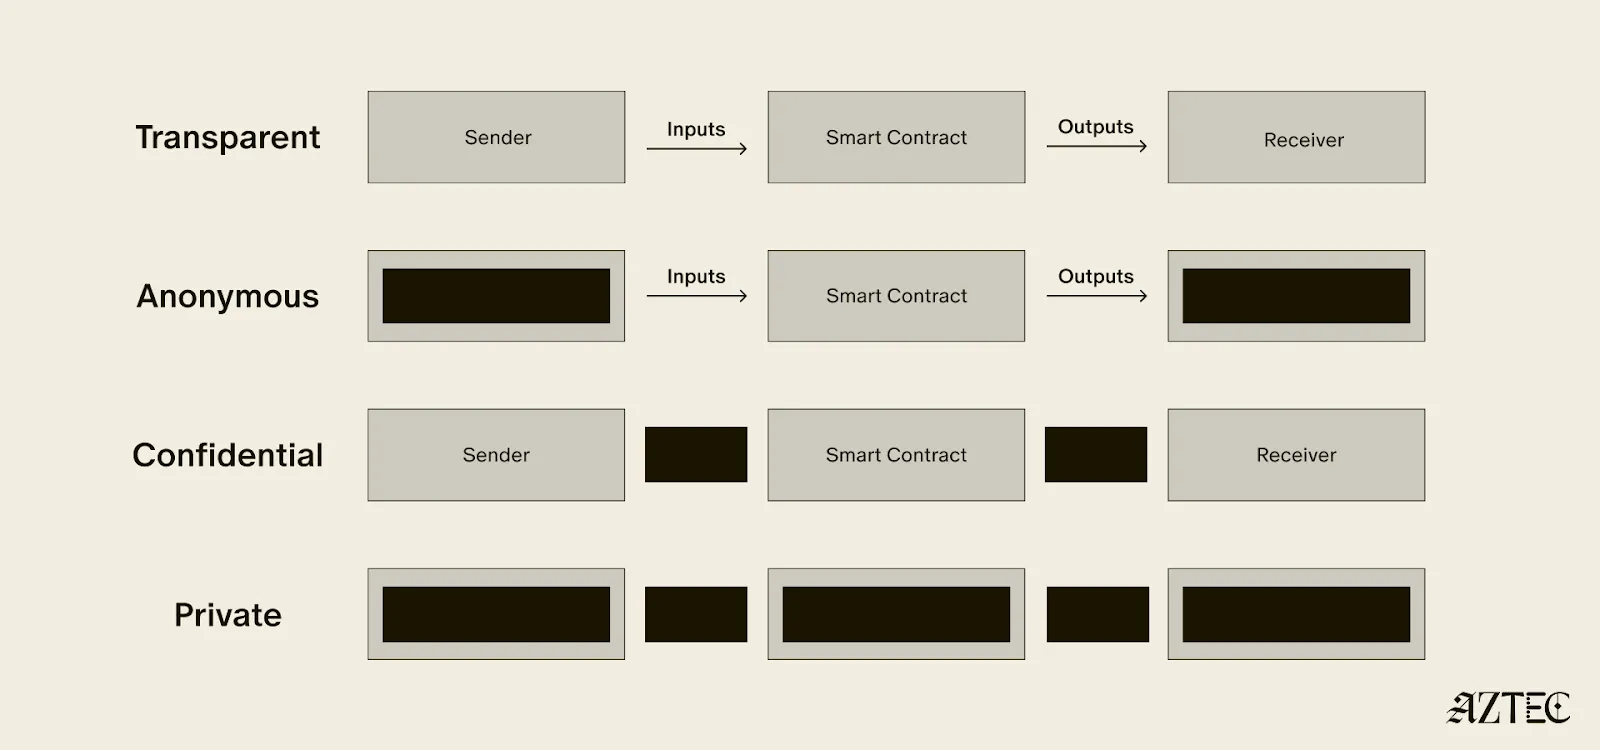
Computation privacy means that any activity that happens is not viewable by anyone other than the intended participants. This includes the contract code itself, function execution, contract address, and full callstack privacy. Additionally, any metadata generated by the transaction is able to be appropriately obfuscated (such as transaction effects, events are appropriately padded, inclusion block number are in appropriate sets). Callstack privacy includes which contracts you call, what functions in those contracts you’ve called, what the results of those functions were, any subsequent functions that will be called after, and what the inputs to the function were. A project must have the option for this pillar to do anything privately other than basic transactions. 

From private money to a private world computer 

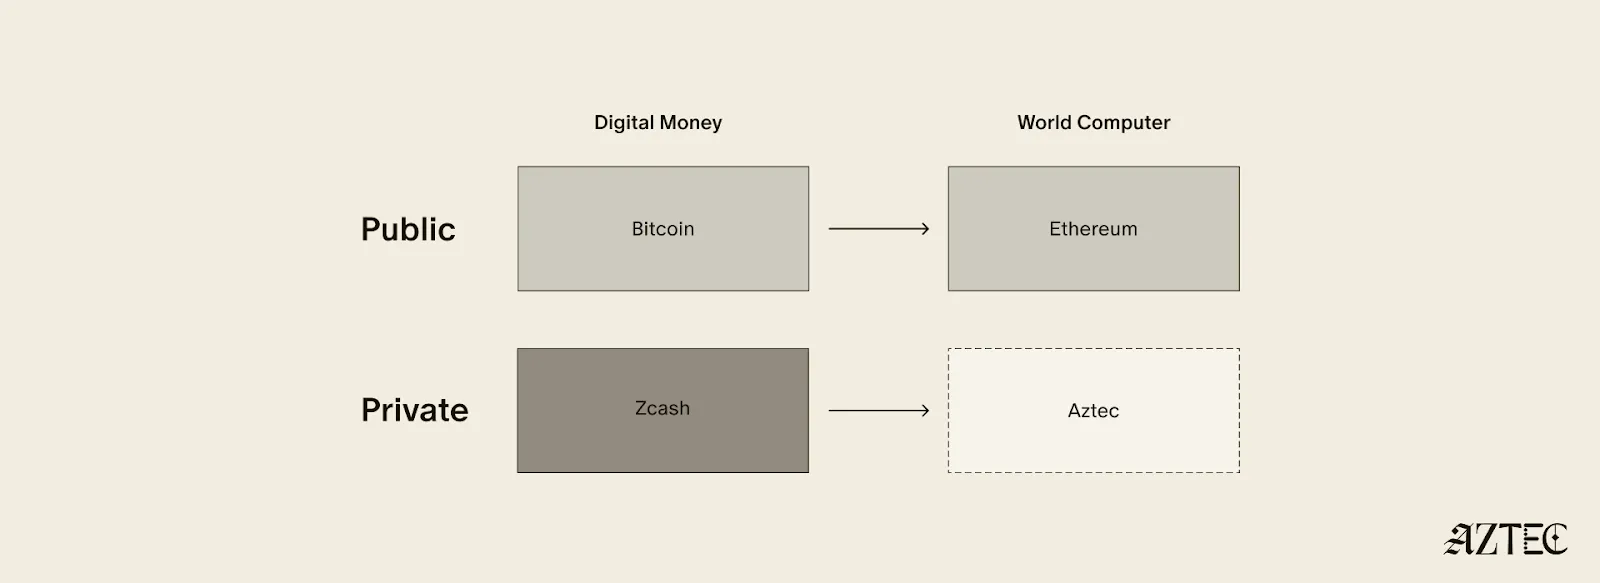
Bitcoin ushered in a new paradigm of digital money. As a permissionless, peer-to-peer currency and store of value, it changed the way value could be sent around the world and who could participate. Ethereum expanded this vision to bring us the world computer, a decentralized, general-purpose blockchain with programmable smart contracts. 

Given the limitations of running a transparent blockchain that exposes all user activity, accounts, and assets, it was clear that adding the option to preserve privacy would unlock many benefits (and more closely resemble real cash). But this was a very challenging problem. Zcash was one of the first to extend Bitcoin’s functionality with optional privacy, unlocking a new privacy-preserving UTXO model for transacting privately. As we’ll see below, many of the current privacy-focused projects are working on similar kinds of private digital money for Ethereum or other chains. 

Now, Aztec is bringing us the final missing piece: a private world computer.

A private world computer is fully decentralized, programmable, and permissionless like Ethereum and has optional privacy at every level. In other words, Aztec is extending all the functionality of Ethereum with optional transaction, identity, and computational privacy. This is the only approach that enables fully compliant, decentralized applications to be built that preserve user privacy, a new design space that we see as ushering in the next Renaissance for the space. 

Where are we now? 

Private digital money

Private digital money emerges when you have the first two privacy pillars covered - transactions and identity - but you don’t have the third - computation. Almost all projects today that claim some level of privacy are working on private digital money. This includes everything from privacy pools on Ethereum and L2s to newly emerging payment L1s like Tempo and Arc that are developing various degrees of transaction privacy 

When it comes to digital money, privacy exists on a spectrum. If your identity is hidden but your transactions are visible, that's what we call anonymous. If your transactions are hidden but your identity is known, that's confidential. And when both your identity and transactions are protected, that's true privacy. Projects are working on many different approaches to implement this, from PSE to Payy using Noir, the zkDSL built to make it intuitive to build zk applications using familiar Rust-like syntax. 

The Private World Computer 

Private digital money is designed to make payments private, but any interaction with more complex smart contracts than a straightforward payment transaction is fully exposed. 

What if we also want to build decentralized private apps using smart contracts (usually multiple that talk to each other)? For this, you need all three privacy pillars: transaction, identity, and compute. 

If you have these three pillars covered and you have decentralization, you have built a private world computer. Without decentralization, you are vulnerable to censorship, privileged backdoors and inevitable centralized control that can compromise privacy guarantees. 

‍

Aztec: the Private World Computer 

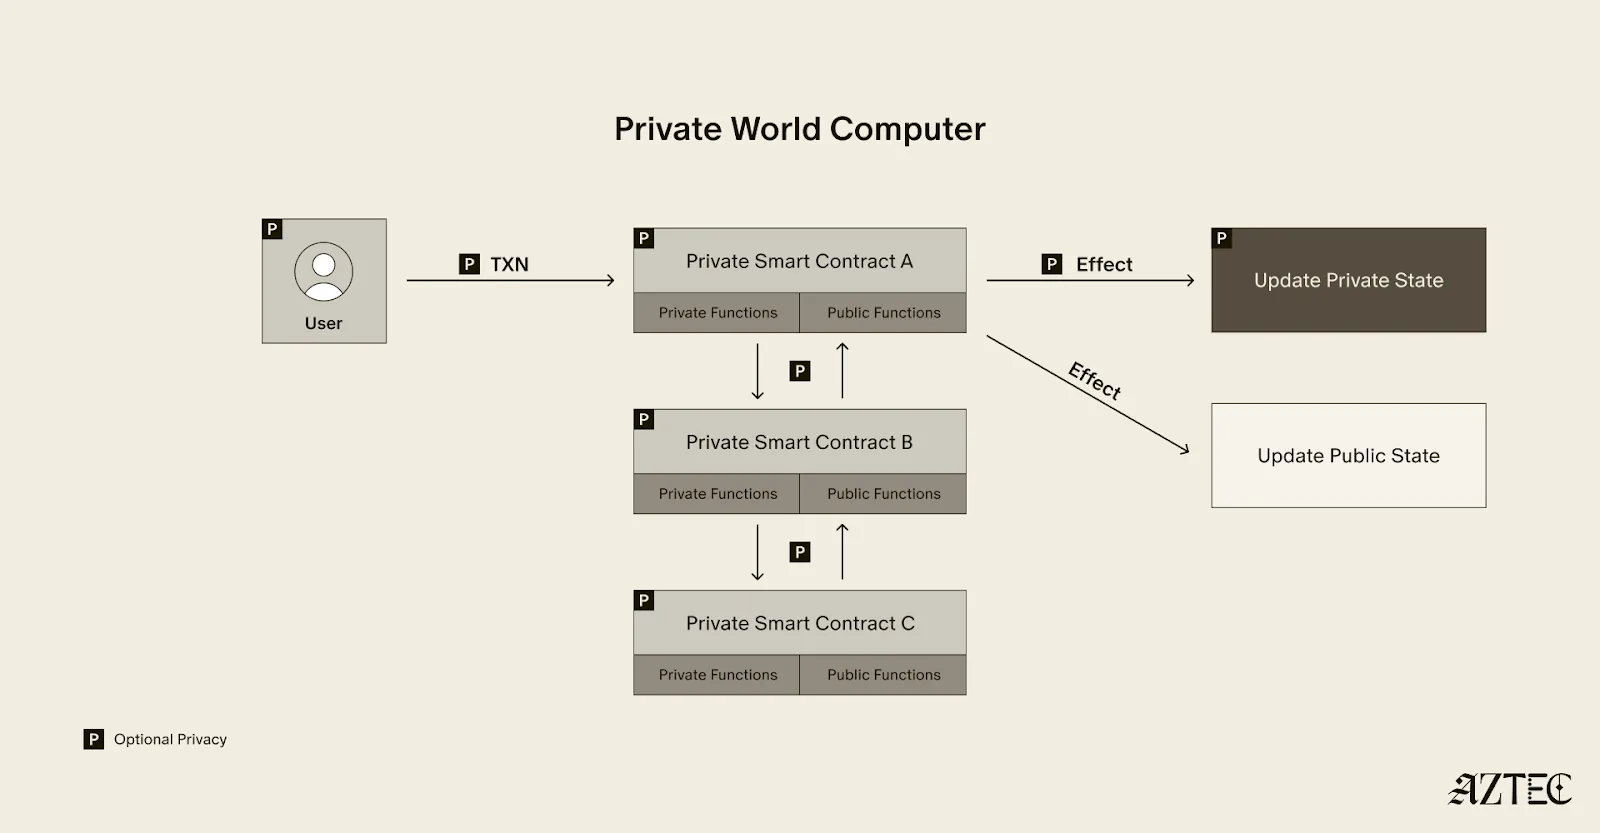
What exactly is a private world computer? A private world computer extends all the functionality of Ethereum with optional privacy at every level, so developers can easily control which aspects they want public or private and users can selectively disclose information. With Aztec, developers can build apps with optional transaction, identity, and compute privacy on a fully decentralized network. Below, we’ll break down the main components of a private world computer.

Private Smart Contracts 

A private world computer is powered by private smart contracts. Private smart contracts have fully optional privacy and also enable seamless public and private function interaction. 

Private smart contracts simply extend the functionality of regular smart contracts with added privacy. 

As a developer, you can easily designate which functions you want to keep private and which you want to make public. For example, a voting app might allow users to privately cast votes and publicly display the result. Private smart contracts can also interact privately with other smart contracts, without needing to make it public which contracts have interacted. 

Aztec’s Three Pillars of Privacy

Transaction: Aztec supports the optionality for fully private inputs, including messages, state, and function calldata. Private state is updated via a private UTXO state tree.

Identity: Using client-side proofs and function execution, Aztec can optionally keep all user info private, including tx.origin and msg.sender for transactions. 

Computation: The contract code itself, function execution, and call stack can all be kept private. This includes which contracts you call, what functions in those contracts you’ve called, what the results of those functions were, and what the inputs to the function were. 

Decentralization

A decentralized network must be made up of a permissionless network of operators who run the network and decide on upgrades. Aztec is run by a decentralized network of node operators who propose and attest to transactions. Rollup proofs on Aztec are also run by a decentralized prover network that can permissionlessly submit proofs and participate in block rewards. Finally, the Aztec network is governed by the sequencers, who propose, signal, vote, and execute network upgrades.

What Can You Build with a Private World Computer?

Private DeFi

A private world computer enables the creation of DeFi applications where accounts, transactions, order books, and swaps remain private. Users can protect their trading strategies and positions from public view, preventing front-running and maintaining competitive advantages. Additionally, users can bridge privately into cross-chain DeFi applications, allowing them to participate in DeFi across multiple blockchains while keeping their identity private despite being on an existing transparent blockchain.

Private Dark Pools

This technology makes it possible to bring institutional trading activity on-chain while maintaining the privacy that traditional finance requires. Institutions can privately trade with other institutions globally, without having to touch public markets, enjoying the benefits of blockchain technology such as fast settlement and reduced counterparty risk, without exposing their trading intentions or volumes to the broader market.

Private RWAs & Stablecoins

Organizations can bring client accounts and assets on-chain while maintaining full compliance. This infrastructure protects on-chain asset trading and settlement strategies, ensuring that sophisticated financial operations remain private. A private world computer also supports private stablecoin issuance and redemption, allowing financial institutions to manage digital currency operations without revealing sensitive business information.

Compliant Apps

Users have granular control over their privacy settings, allowing them to fine-tune privacy levels for their on-chain identity according to their specific needs. The system enables selective disclosure of on-chain activity, meaning users can choose to reveal certain transactions or holdings to regulators, auditors, or business partners while keeping other information private, meeting compliance requirements.

Let’s build

The shift from transparent blockchains to privacy-preserving infrastructure is the foundation for bringing the next billion users on-chain. Whether you're a developer building the future of private DeFi, an institution exploring compliant on-chain solutions, or simply someone who believes privacy is a fundamental right, now is the time to get involved.

Follow Aztec on X to stay updated on the latest developments in private smart contracts and decentralized privacy technology. Ready to contribute to the network? Run a node and help power the private world computer. 

The next Renaissance is here, and it’s being powered by the private world computer.

Read more
Aztec Network
Aztec Network
15 Oct
•
xx min read

Post-Quantum Aztec

All blockchains today – L1s, L2s, and shielded pools – make use of elliptic curves somewhere in their stack.

Elliptic curves are used in all sorts of places: signing transactions, validator attestations, data availability (such as blobs), zk-snarks, secret sharing, encryption, etc.

No cryptocurrency project today is 100% quantum-proof.

Nobody has a reliable date for when a quantum computer will break the elliptic-curve cryptography we use today, but we know it’s coming.

For a privacy network, some of the work cannot wait for that uncertainty to resolve. An attacker could collect encrypted data today and keep it until they have the means to decrypt it. This is the so-called “Harvest now; decrypt later” attack. Replacing an encryption scheme ten years from now would not protect the data an attacker already harvested under a classical encryption scheme.

Aztec is already quantum resistant against this type of attack. It was designed from the ground up to allow users to bunker-proof their accounts and data against quantum computers.

However, there is work to be done to make Aztec fully quantum secure and able to function with full privacy in the post-quantum world. 

Our roadmap to expand our quantum security has two targets:

  • February 2027: Hardened libraries and better off-the-shelf contract development patterns that protect against harvest-now-decrypt-later attacks
  • 2030: a full post-quantum migration.

The first requires changes to how applications handle private data. The second reaches into the proving system, account authentication, key derivation, validator signatures and Ethereum settlement. Understanding why these need different schedules requires getting into the cryptography.

‍

The risk of changing cryptography

Years of hard-won experience have taught us that the greatest risk to a network like Aztec is implementation bugs. Our AI audit harness has found critical vulnerabilities, including ones that months of expert human internal and external audits didn’t find. These have been patched in the upcoming v6 Aztec Network release. We have spent the past 18 months hardening our software and cryptography. That work has to continue while we develop their replacements.

AI also changes cryptanalysis. For example, the attack on HAWK (a post-quantum signature scheme) exploited structure specific to that signature scheme and reduced its security enough to end its candidacy for standardization. That is a reason to examine the assumptions and structure of each scheme with care.

Rushing headfirst into new cryptography that has not faced enough scrutiny would expose users to immediate risks, greater than the speculative risks of quantum computers. The Foundation has finite resources, and time spent on the post-quantum migration is time we have to balance against securing the software users depend on today.

Our default approach to changing cryptography is conservative. Any changes to our protocols must be justified, subjected to extraordinary cryptanalysis and have formally-verified implementations.

‍

Making Aztec post-quantum

To make Aztec post-quantum requires several pieces of cryptography. Aztec has an application layer (smart contracts), the Aztec protocol layer, and it settles on Ethereum itself. All three have responsibilities with respect to post-quantum security.

Protocol layer changes required:

1. Proving System

  • A post-quantum zero-knowledge proving system. Our unique requirements as a decentralized programmable privacy protocol present unique challenges, explained later.

2. Addresses & Keys

  • Changes to Aztec addresses and public keys, which are all elliptic curve points.
  • (These current addresses & keys can be used in a quantum-safe way today, though).
  1. Validator Keys & Signatures:
  • post-quantum digital signature scheme for Aztec’s decentralised validators’ attestations. 
  1. Adoption of the required Ethereum changes outlined below.

Application layer changes required:

  1. Post-quantum digital signature schemes.
  2. Post-quantum KEMs (secret sharing mechanisms).
  3. Post-quantum public-key encryption.

Ethereum changes required:

  1. DA
  • A DA layer that doesn’t use BLS12-381 KZG commitments.
  1. Verification Primitives
  • Cheap post-quantum snark verification primitives, as an alternative to the currently cheap de facto BN254 EVM precompiles.
  1. Public Keys & Signatures
  • Ethereum EoA public keys and signatures
  • Ethereum’s BLS keys.

The latter application layer requirements are not on Ethereum’s post-quantum roadmap as they’re a unique requirement of privacy protocols like Aztec and ZCash.

Notice that the bulk of the changes required for user privacy are dictated by the choices of Aztec smart contract developers at the application layer. Apps can adopt post-quantum encryption and signature schemes today on Aztec, and different Aztec smart contract developers can freely explore differing approaches as the state of the art in post-quantum advances.

‍

Protecting private data now

If and when quantum computers arrive, Aztec is already (uniquely for privacy protocols) protected in two key categories because of our existing design choices.

  1. A post-quantum proof system can securely use historical state created today 
  2. By default, historical state (including encrypted logs) is not vulnerable to “harvest-now-decrypt-later” attacks

‍

“Traditional” messaging in privacy protocols 

If I send you private tokens, there’s no onchain public balance update for you to see or query. Private state is stored in notes, so I need to tell you about the existence and contents of your new note for you to be able to use it.

A common solution is for me to publish an encrypted message to a public bulletin board that your wallet can find and decrypt. ZCash pioneered this approach.

Elliptic curve key exchange protocols are well-suited to this, because the amount of data I need to publish to convey “this is for you” and “here’s the ephemeral key you’ll need to decrypt this message” is a single ECDH ephemeral public key; an elliptic curve point; a tiny 32 bytes of info. We like this small communication overhead, because less data means faster tx throughput and cheaper DA costs passed on to users.

But elliptic-curve key exchanges can create a harvest-now-decrypt-later risk. The discrete log of such an ephemeral public key will one day be solvable by a quantum adversary. They could derive all ephemeral secret keys of all messages in the bulletin board. They’d then be able to brute-force combine the resulting list of ephemeral secret keys with a list of all known users’ viewing public keys to effectively derive all decryption keys on the network, to then decrypt all encrypted messages. They’d learn the contents of the note I sent you: the amount and that it belongs to you.

There are a few classical (pre-quantum) solutions to this. They follow from the observation that if an attacker doesn’t know one of: your public key or the ephemeral public key, then they won’t have enough information to decrypt any of your encrypted messages! Wallets are beginning to adopt the following:

  1. Don’t publicly share your public keys.
  • This is easier said than done. It defies the initial design intentions of public key cryptography. After all, you’d need to give me your public key for me to send you money! What if you share it with a dishonest counterparty, or an honest counterparty whose data leaks accidentally? This leads to another protection:
  1. Use a new public key for every new transaction.
  • That way, you stem any leakage if any of those public keys does leak. Some wallets of some privacy protocols already do this.
  1. Don’t broadcast any ephemeral public keys to a public bulletin board.
  • If ephemeral public keys aren’t seen by a quantum adversary, they can’t decrypt your messages, regardless of whether your address is public. Share this data through some private communication channel instead.

‍

Aztec Public Keys are hashed

Intentionally, most of the public keys in the Aztec protocol are hashed to reduce their leakage to a future post-quantum adversary. The public keys are not even exposed to Aztec smart contracts (which could be malicious).

(Private smart contract protocols even have a niche “harvest now; link later” attack to protect against, whereby a quantum adversary could link all your notes and nullifiers together to reconstruct your entire tx graph. Hashing the nullifier public key resolves this).

‍

Aztec is flexible, today

The Aztec Protocol is agnostic to the way in which users and applications (smart contracts) share private information between each other. It’s a beautifully flexible protocol because we knew times would change. Smart contract developers can adopt the above conventions today, and indeed many are doing so.

Aztec smart contracts can emit arbitrary bytes of data as “private logs”. These private logs are the intended delivery mechanism for sending encrypted notes. It’s up to smart contract developers how they populate those logs. I.e. they can choose:

  • Whether to use these private logs at all;
  • How to get the recipient’s attention;
  • How to convey the decryption key;
  • Which encryption scheme to use.

Aztec also supports offchain note delivery, which gives applications another secure option. A sender delivers the message through an off-chain side channel that is not visible to harvest-now-decrypt-later attackers.

All this flexibility in today’s Aztec Protocol enables Aztec smart contract developers to explore the tradeoff space in a way that best serves their users and use cases. Choices will need to balance: proving speed; DA costs; discovery of pertinent notes; post-quantum threats.

‍

Better libraries

Of course, most smart contract developers don’t want to think about such things, which is why the Aztec ecosystem has smart contract libraries with off-the-shelf solutions.

Our early 2027 work will focus on hardening these libraries and giving Aztec developers better patterns for protecting their users’ private data, with clear requirements for delivery and secret establishment.

‍

Post-quantum secret sharing

A more comforting solution to post-quantum worries would be for Aztec smart contracts to instead adopt post-quantum secret sharing and encryption schemes. 

We’re researching the best approaches and working on some tidy libraries. The good thing is, the agnosticism of the Aztec Protocol means multiple libraries for differing post-quantum secret sharing schemes can be written and adopted by different applications on Aztec.

‍

Constrained Delivery

In most other privacy protocols, the construction of an encrypted note is not constrained by any circuit.

For example, if I send you ZCash tokens, the ‘transfer’ function does not constrain that I have correctly encrypted your note, nor that I have attached the correct ephemeral public key that would enable you to discover and decrypt your encrypted note. I could technically broadcast garbage and you wouldn’t receive your funds. That’s arguably fine in a “simple” transfer protocol. It’s not in my interest to corrupt the encrypted notes that I create for you. After all, you can just claim I didn’t pay you until you do receive a valid and decryptable message. 

But when you generalise beyond simple transfers to private smart contracts, there are use cases whereby a sender might not be incentivised to deliver valid data to a recipient. The sender might actually prefer to corrupt a recipient’s data. Imagine a private swap. The contract should not complete the trade if one party receives a commitment to a note whose contents they cannot recover.

In such cases, the private functions (circuits) need to constrain that a recipient will be capable of discovering and decrypting a sender’s encrypted messages. Aztec’s smart contract libraries have rails for this so-called “constrained delivery”. If a use case assumes distrust between sender and recipient, the smart contract developer can enforce their correct adherence to the rules. The protocol then constrains that all private logs emitted by smart contracts are guaranteed to be broadcast – without tampering – to Ethereum blobs.

With this in mind, the constraints required to support post-quantum encryption then become a very important consideration. We’ll need post-quantum libraries that are efficient to prove.

Key and ciphertext sizes matter, but so does the cost of proving the key exchange, encryption and associated checks. A scheme can be fast as native software and expensive inside a circuit.

MIKE, published on 6 October, illustrates why this remains an active research question. It is an isogeny-based non-interactive key-exchange proposal. Its authors report 80-byte public keys and shared-secret computation, including key validation, in 4.9 milliseconds on a 3.3 GHz AMD CPU at their claimed NIST level 1.

Compact keys are attractive for note delivery. We still need to understand its circuit costs and give its security assumptions time to face scrutiny. Those native timings cannot tell us whether it is the right choice for Aztec.

The encryption and proving-system decisions therefore affect each other. Choosing encryption first and discovering that it is prohibitively expensive in the chosen prover would leave us rebuilding one of them.

Choosing the encryption scheme we will prove inside future post-quantum circuits is a separate, later milestone. Applications that need the contract itself to guarantee delivery impose harder requirements on that choice.

‍

Post-Quantum Proving

Ok, so Aztec provides flexibility for good post-quantum privacy today. And we have plans to roll out even better post-quantum libraries.

But what about the proving system? A post-quantum adversary might be able to forge proofs. Thankfully we have some more time to choose a post-quantum proving system.

Aztec has several proving system requirements that other projects aren’t encumbered by (due to our commitment to both privacy, decentralisation and programmability), which we’ll elaborate on.

  • Low memory and CPU requirements: proving must be possible on a phone, in the browser.
  • Actual zero-knowledge!
  • Fast client-side recursion.
  • Small client-side proof sizes.
  • Cheap L1 verification.
  • Simple, maintainable, and secure.

Common benchmarks for proving system performance don’t take into consideration all these requirements. Fast client-side recursion in particular is often overlooked.

‍

The problem with recursion

Aztec uses CHONK, an elliptic-curve and pairing-based proving system built around the requirements of private smart contracts. Users generate proofs on their own devices, and a transaction can involve several private contract calls. Recursion lets us combine those calls into a proof of the transaction without requiring the browser to handle the entire computation as one enormous circuit. CHONK’s design puts low memory use and recursive composition at its centre.

There are tradeoffs you can make to get a faster prover. Some give the verifier more work. A custom “precompile” circuit for an expensive operation can save the prover from executing that operation through thousands of VM instructions, but introduces additional commitments and checks that increases Verifier complexity.

The problem is that, in the recursive setting, your verifier is in your prover. The next proof has to establish that the verifier accepted the previous proof.

I have lost count of the conversations about new prover technology where recursion gets a handwave and a “we’ll deal with it later.” It is a complex, messy problem that is easy to postpone until you need users to generate private transaction proofs in a browser.

Some alternative designs might execute an entire function stack within a single VM instance. That might work for some bounded stack depth. But snarks are gaining traction in web2 too (see zkPassport for example). Bridging between chains also often requires snarks. Privacy protocols should be able to verify traditional snarks for as long as we remain in a pre-quantum world. 

Zero knowledge introduces another set of costs. I have heard the same assurances that adding it will be easy and will not affect performance. From personal experience, such claims often disintegrate on contact with reality.

We thought adding zero knowledge to CHONK would be easy. It took us six months and a re-architecture of our recursive proving stack. Modern proof systems have such complexity that throwing randomness into the execution trace and calling it a day almost never works. Adding ZK typically increases proof size and verifier work, which then increases the cost of recursion.

The result is that the real cost of recursion in a production proving system, with all of the edge-cases and exceptions and little additions that pile up, is never as fast as the initial proof-of-concept claims. For Aztec that is a problem because recursion is essential and not an afterthought - we won’t commit to a proving system that can’t meet our extremely tight recursion requirements.

Luckily there are some candidates, and the Ethereum Foundation is doing trailblazing work as one of the few teams that has started to take this problem seriously.

‍

Getting larger proofs through the network

Proof size matters because Aztec transactions travel through a peer-to-peer network. Every node that receives and forwards a proof pays its bandwidth cost. Aztec’s 20kb proofs are “ok”. If it ever becomes a bottleneck we can make them smaller with little effort because we use elliptic curves.

Post-quantum proof systems (the fast ones), on the other hand, have proofs of ~300KB, which is not ok.

Worse, there are zero post-quantum proving systems whose proofs are small enough to gossip across a p2p network whilst achieving acceptable transaction throughput. There are fundamental constraints which mean this is not likely to change!

Fast recursion offers another path. A node could receive two transaction proofs, produce one proof that establishes the validity of both, and forward the aggregate. Other nodes could repeat the process. Transaction data would still have to travel through the network, but the proof overhead could shrink across a batch.

Ethereum’s post-quantum research faces a related problem. Its proposed hash-based validator signatures lack BLS’s cheap native aggregation, so leanVM supplies a proof that many signatures pass verification. The draft EIP-8292 assigns that proving work to aggregators with suitable hardware. Their longer-term roadmap requires full virtual-machine proof aggregations which presents an extremely similar problem to ours.

For the Aztec approach to work on ordinary nodes, aggregation needs to be cheap. My working estimate is that two-to-one aggregation in roughly 20–100 milliseconds on a modern CPU could make it practical. 

Nodes receive different transactions at different times, so they will duplicate work. An attacker may try to exploit that duplication. We need to establish how many aggregations one malicious transaction can induce and what happens to throughput under that load.

This problem is currently under-explored and poorly parametrised and substantial work needs to occur before a definitive solution can be decided on.

‍

Which proving systems look promising?

The main candidates are hash-based systems over binary fields and small prime fields, lattice-based systems, and proposals that combine both prime-field and binary-field representations.

The Flock paper gives a good example of the progress in binary-field proving. Its authors report proving 660,000 BLAKE3 hashes per second on an M4 mac on ten cores. 

These are impressive numbers. Hashing is a major part of verifying hash-based proofs, so cheap hashing is good for recursion.

However, binary field systems are weak with regards to integer multiplication. Trustless access to Web2 data is one of the biggest untapped capabilities of blockchain. Private applications should be able to use passport signatures, credit credentials, TLS-based data proofs and signed web tokens without publishing the underlying information. That means dealing with ugly Web2 cryptography: RSA, large-field elliptic curves and integer arithmetic.

Binary-field arithmetic does not behave like integer arithmetic. In particular, integer addition has carries, and multiplication needs a representation and a circuit that handles them. A BLAKE3 benchmark tells us little about the cost of proving a 4096-bit RSA verification. We need to measure the operations our applications will use.

That is what makes hybrid approaches interesting to me: using one commitment both in a binary representation and a prime field representation depending on context. This is an active area of research with limited existing published work, which highlights how rapidly evolving this space is.

Lattice-based proving deserves serious attention too. The Jolt team’s September release replaced the elliptic-curve commitment scheme Dory with Akita, based on Module-SIS. The authors reported faster proving and verification and proofs below 100 KB. Their announcement also described zero knowledge as forthcoming, so those figures do not settle our comparison.

Lattice commitments retain algebraic structure that could be useful for the kinds of composition we rely on. That makes them attractive candidates to investigate, although translating CHONK’s techniques would require work. The field size is a design choice we need to evaluate within each construction; lattices do not impose one universal 128-bit-field requirement.

Much of the suspicion around lattice systems rests on vibes about whether the underlying structure is vulnerable to AI cryptoanalysis. There are good reasons to scrutinize a particular assumption, parameter set or reduction. “It uses lattices” does not supply that scrutiny.

Not all lattice crypto is equal. The fundamental short-integer-solution hardness assumption has had decades of cryptanalysis. Lattice crypto has a degraded reputation because some modern protocols layer on additional, weaker hardness assumptions that have shown to be broken by quantum adversaries. But there is no quantitative evidence to suspect the core harness assumptions of lattice crypto are vulnerable.

Either way, the rate of development gives me confidence that we will have good options. It also makes choosing a winner today premature. We need comparisons that include our applications, recursion, zero knowledge and security parameters together.

‍

Signatures

In Aztec transactions, digital signatures are private witnesses within private functions of smart contracts (zero-knowledge circuits), which helpfully means we don’t care so much about the size of an individual signature. This gives us more freedom than non-rollups e.g. Ethereum, where signature size directly contributes to their transaction size. This matters because post-quantum digital signatures are typically large.

‍

Baking Bad

Similar to other privacy protocols such as ZCash Sapling and Orchard, several Aztec keys are baked-into the preimage of an Aztec address. To enable ‘post-quantumification’ of the Aztec protocol, we’re exploring externalising those keys to a canonical keystore registry. An Aztec address would then cease to be an elliptic-curve public key, and instead would simply be a hash which serves as a lookup into this registry. The registry could store all manner of exotic post-quantum public keys for different use cases.

Hash functions belong in the migration too

Aztec uses Poseidon2 throughout the protocol. Poseidon2 is technically post-quantum secure. And while Poseidon2 is secure for our chosen domain, recent breaks over small-field Poseidon signal that we should move to a different hash function in the long-term.

We’re confident that Poseidon2 will remain practically secure for many years, but the writing is on the wall and it would not be wise to use this hash function in Aztec’s future post-quantum system. 

We will likely replace it with either Blake2s or Blake3. The Ethereum Foundation are also considering a canonical hash function for their post-quantum roadmap and we’ll more than likely follow their lead here. Binary-field proof systems can trivially handle BLAKE hashes so the need for Poseidon2 will have run its course.

‍

Why the roadmap extends to 2030

Our proposed selection milestones are:

  • March 2027: choose a post-quantum signature scheme.
  • July 2027: choose a post-quantum public-key encryption scheme, with constrained note delivery benchmarked in the leading proof systems.
  • November 2027: choose a post-quantum proving system.

The encryption milestone needs circuit measurements before we settle the proving-system choice. The proving-system decision needs working recursion and zero knowledge, alongside representative application workloads. These dates give us a sequence for answering those questions.

After selection, we need to replace the cryptography across the system. That includes addresses and key derivation, application-specific key checks inside the kernels, account authentication, validator authentication and the proof chain that ends on Ethereum. We also need to handle existing private state and give users and applications a migration path.

Ethereum supplies another dependency. Aztec’s final proof verification and blob commitments sit within Ethereum’s cryptographic infrastructure. A full post-quantum migration has to account for Ethereum’s upgrades as well as our own.

The roughly three years between the final selection milestone and end of year 2030 leave room for integration to expose problems that isolated benchmarks cannot. Development and integration of multiple novel post-quantum cryptographic primitives into Aztec will be neither simple nor fast. In addition, the entire tech stack will have to be formally verified due to the incredible threat that AI poses with regards to finding and exploiting bugs.

I think Q-day within four years is unlikely, and the roadmap is designed under the assumption that post-quantum work is not the sole focus and obsession of the Aztec Foundation. If there is evidence of faster progress in quantum hardware that would bring forward Q-day, we will be able to accelerate our roadmap by diverting resources to this project.

Developers will not have to wait for that full migration to make better choices about private data. The January work will provide hardened libraries and documented patterns to build against. A developer building a private application will be able to protect the data they create today to stand the test of time.
Aztec Network
Aztec Network
7 Aug
•
xx min read

Alpha V5 Proving System Vulnerability

Status

Core contributors identified a critical vulnerability affecting the V5 Alpha proving system on 27 July 2026 through internal AI-assisted auditing.

V5 remains Alpha software. Critical findings can arise during this phase, and the audit process exists to identify them before broader deployment. This finding places V5 funds, applications, and contract state at risk.

Treat funds and applications on V5 as exposed to a protocol-level failure until contributors complete incident response work and operators carry out the required network actions.

‍

What we are disclosing

An attacker may be able to exploit a flaw in the current V5 proving system by constructing a proof that passes verification for a transaction the network should reject. If accepted, that transaction could produce a state transition outside the rules V5 intends to enforce.

Contributors cannot determine whether anyone exploited the flaw before this finding. The affected system lacks the information needed to distinguish ordinary accepted transactions from transactions accepted through the flawed proving path. Historical chain activity cannot establish whether exploitation occurred or quantify its impact.

‍

Application safeguards

We expect application teams to prepare safeguards in the coming weeks.

Those safeguards may include changes to application controls, deployment procedures, user flows, and migration plans. We expect each team to assess its contracts and determine which protections fit its architecture and users.

We expect teams planning a V5 deployment to pause that work until contributors publish further guidance. We expect teams with live contracts to review their ability to limit user exposure, isolate affected functionality, and move users to fresh deployments if needed.

We expect applications that maintain administrative or emergency controls to assess whether those controls can reduce user risk during the incident timeframe.

‍

Next steps

Core contributors are working with operators, application teams, and bridge operators as applications add security guards around affected flows.

The findings from this incident will inform the V6 release, including circuit updates that prevent the network from accepting proofs tied to an affected proving system.

V5 launched as Alpha software, with V6 planned for later in 2026. Contributors will publish a security roadmap covering the remaining work and release path.

‍

Known vulnerability status

Reviewers have not identified other high-severity or critical V5 Alpha vulnerabilities at this time.

Internal and external human audits have completed, and contributors continue AI-assisted auditing. Alpha is the period for identifying faults before production deployment.

‍

Community
Community
4 Aug
•
xx min read

Dark Forest Aztec Game Goes Live

Dark Forest is a real-time strategy game played across a procedurally generated universe where most of the map is hidden. You cannot see rival players, their planets, or their fleets. You only know what you have explored. Everyone shares one universe, and nobody has the full picture.

In most onchain games, every position and every move is public, because the chain is public. Dark Forest used zero-knowledge proofs to break that assumption: players prove their moves are valid without revealing where those moves came from. The result is a game of hidden information running on a public network.

Dark Forest Aztec ports the original Dark Forest 0.6 to Aztec. It keeps the gameplay from the original and rebuilds the privacy layer on Aztec's programmable privacy.

A note before diving in: this is early, experimental software on Aztec Alpha V5. Treat it as an alpha and play accordingly.

The universe you cannot see

You start on a single home planet with almost the entire map dark. To find anything you mine the universe, running a client that explores coordinates and reveals what sits there: unclaimed planets, resources, and eventually the edges of other players' territory.

You are never handed a view of the board. You earn it one region at a time, and everyone else works under the same fog.

What is hidden on Aztec

Your home coordinates and your fleet movements are private state, expressed as first-class private notes on Aztec. Your location and where you send energy stay hidden, enforced in the contracts by zero-knowledge cryptography.

What sits onchain is a set of cryptographic commitments. Instead of storing every planet's full details in the open, the contracts store Poseidon2 hashes of entity state. When you make a move, your client supplies the full state, the contract checks it against the stored hash, applies the change under zero-knowledge constraints, and writes a new hash back. Full game state lives offchain and gets rebuilt from public logs by an indexer, which is what renders your map without exposing every player's position.

So you can prove you made a legal move from a planet you own without revealing where that planet is. Aztec applies the same principle to private payments and private contracts.

How you play

Four actions carry the game.

Explore. Your explorer sits in the bottom left. Set it running and it uncovers the map around you, surfacing planets, resources, and other players.

Send energy. Most planets produce energy. Click and drag from a planet you own toward a target to capture or weaken it.

Route silver. Asteroid fields produce silver. Move it to your planets and spend it on upgrades, or send it to a Spacetime Rip to convert it into score.

Hunt artifacts. Some planets hold artifacts. Your Gear ship discovers them. Once harvested, you deposit them on planets to boost stats.

Four stats drive most decisions.

Energy is the core resource. Planets generate it over time up to a capacity, and you spend it on everything: claiming planets, reinforcing your own, attacking rivals. Two details matter. Moves are taxed, so a flat percentage of a planet's total capacity burns every time you send energy, which discourages small frequent moves. And energy decays over distance, so send it too far and almost nothing arrives. A common rule of thumb is to let a planet fill to about 75%, then send it down to about 25%.

Defense reduces the damage incoming energy does when it lands. Higher-level planets often have lower defense, but they hold much more energy, so they still take more to capture. Defense matters most on front lines.

Range sets how far a planet can send energy. It governs how fast you expand and how efficiently you move energy inside your own empire, since shorter relative distances mean less decay. Good range also lets you strike deep into an opponent's territory.

Speed sets how quickly a move arrives. Usually secondary, though a fast strike can land before a rival reacts, and some playstyles reward capturing many nearby planets quickly.

Planets can also be upgraded with silver and enhanced with artifacts. Space types carry different multipliers, from mild Nebula to punishing Dead Space, so where a planet sits changes how it plays.

How scoring works

There is a scoreboard, and territory alone does not win it. This round scores two activities: discovering artifacts with your Gear ship, and withdrawing silver through Spacetime Rips.

Point values from the in-game help page:

  • Each unit of silver withdrawn: 1
  • Common artifact: 2,000
  • Rare: 10,000
  • Epic: 200,000
  • Legendary: 3,000,000
  • Mythic: 20,000,000

Silver accrues one point at a time. A single Mythic artifact is worth twenty million of them, so artifact hunting decides rounds and silver withdrawal sets your floor.

Silver has two competing uses. Spend it on upgrades and your planets get stronger, extending range and hardening defense. Withdraw it through a Spacetime Rip and it becomes scored points, but it is gone. Every unit is a choice between building the empire and banking points.

Upgrades tend to win early, since a stronger empire reaches more asteroid fields and finds more artifacts. Late in a round that calculation flips, because a planet you never use is worth less than points already scored.

Artifacts do both jobs at once. They score on discovery, and once deposited they boost a planet's stats, which makes the next expedition easier.

Why you explore

Nothing happens until you find something to act on. Your explorer turns dark space into planets you can capture, asteroid fields you can mine, and artifact-bearing planets you can raid. Sitting still means no new energy, no silver, no score.

Exploring also buys information. The map you have uncovered is an advantage nobody else holds. Knowing where high-level planets sit, which asteroid fields are unclaimed, and where space types shift lets you plan further ahead than someone still working through their starting region.

You find other players as a byproduct. There is no player list. You explore outward until your revealed region touches territory someone already owns: a planet in another player's colors, sitting where you were about to expand. Their home coordinates stay private, so you learn something narrow. Someone is here, roughly this direction, holding this much. You infer the rest, and you have no way of knowing whether they found you first.

What happens when you run into someone

You have three broad options.

Stay quiet and keep growing. Nothing forces you to engage. Keep exploring elsewhere, keep routing silver, keep upgrading. Your positions stay private, so silence costs you only time, which is what you want if they are stronger. The risk is that they are doing the same thing faster.

Fortify the border. If the contact sits somewhere you cannot lose, spend energy hardening the planets facing them. Defense is worth most where an attack will actually land. This keeps the option to fight without committing to one.

Attack. Send enough energy to overwhelm the target's defense and the planet becomes yours, along with its production and its position as a staging post. Higher-level planets are the prize and take proportionally more to crack.

Attacking costs more than energy. A move that lands tells your rival where you strike from, and that you are close enough to be worth answering. Retaliation can then come from directions you have not explored, launched from planets you cannot see.

Multiplayer in practice

Everyone plays one shared universe in real time. No turns, no lobbies. Energy regenerates whether you are watching or not, moves stay in flight while you sleep, and rivals expand while you are away from the screen.

Most strategy games let you watch a threat approach. Here you tend to see the consequences: a planet you owned this morning in someone else's colors, an incoming move you notice once it is already close.

That produces a particular kind of paranoia. You are trying to find everyone else while avoiding being found, and every expansion is a strategic bet that the space ahead is empty.

Information becomes tradeable, because it is scarce. Players compare notes, warn each other about aggressive neighbors, and agree who expands where, then break those agreements when the scoreboard makes it worth breaking.

Why it matters beyond the game

A fully onchain game where players cannot see each other's positions is hard to build, and building it well says something about the platform underneath.

Hidden state, private notes, and client-side proving are the same building blocks behind private applications across Aztec. Dark Forest is a way to watch them work.

Getting started

Dark Forest Aztec is playable now as an alpha. Expect a learning curve; the original was famous for it. DFArchon maintains onboarding material and a community for new players. Round One is live. The universe is dark, and everyone else is out there somewhere. Go find them, quietly.

Play Now

‍

Follow the Builders

DFArchon on X‍

Source and docs

Aztec Network
Aztec Network
22 Jul
•
xx min read

How Gas Works on Aztec

Gas on Aztec

Gas on Aztec is known as Fee Juice and is used to pay for transaction costs. This is the same as $ETH on Ethereum. Some apps will handle transaction costs for you under the hood, but if you are using a browser extension wallet, you will not be able to send transactions without it. Fee Juice can be obtained by bridging the $AZTEC token on Ethereum to the Aztec Network L2. This means that under the hood, all activity that happens on Aztec is underpinned by the $AZTEC token bridged into the network. Some bridges like Shield (by human.tech) handle this for you, allowing you to allocate a portion of your bridged transaction to convert into Fee Juice and land in your wallet automatically.

Public vs Private Assets

Assets and transactions on the Aztec Network can be either public or private. If you bridge publicly, your tokens will arrive as public, traceable tokens visible to all. Privately bridging, on the other hand, will give you private assets that are visible only to you. These assets can then be sent privately to another user or wallet without ever revealing who you are, what tokens were sent, how many, or who the recipient is.

Public vs Private Gas

Like tokens on the Aztec Network, Fee Juice (gas) can also be public or private. The reason for this is that even if what you are sending is private, the gas you spend to execute that transaction could still be visible if you are using public Fee Juice, potentially revealing transaction patterns and activity. Private Fee Juice keeps your entire transaction footprint hidden. When you send a private transaction, you can use private Fee Juice, and when you send a public transaction, you can use public Fee Juice, which means your transaction costs are always aligned with the type of transaction you're making.

Fee Juice in Apps

Aztec has native fee abstraction, which means apps could let you pay for transactions in any token you want, or cover your fees entirely. Apps like Nyx may choose to cover part or all of a user's transaction costs, or allow you to pay in tokens that are convenient for you. This means you will most likely never see Fee Juice in an app; instead, you'll pay in whatever makes sense for what you're doing, on your terms. Similarly, you might never even see an Aztec wallet at all, because the app itself becomes your interface that you connect to using your MetaMask wallet.

Fee Juice in Browser Wallets

If you're using a browser extension like Azguard, you'll manage Fee Juice directly in your wallet alongside your private and public balances, converting between tokens as needed to cover transaction costs.

When you bridge tokens in, you'll need enough Fee Juice to cover the cost of your first transaction, then you'll need to monitor how much Fee Juice you have available to make transactions. Browser wallets will allow you to send either publicly or privately to other users and will default to using either public or private Fee Juice depending on the type of transaction. Both private Fee Juice and public Fee Juice will appear by default in your token list.

Wrapping up

How you handle Fee Juice depends on where you're transacting: apps can abstract it away entirely and let you pay in any token, while a browser wallet like Azguard puts it in your hands to manage across public and private balances. Match your gas to your transaction, keep private activity private down to the fee, and you move on your terms.