
Menu
Contributors identified a critical vulnerability in Aztec's V5 Alpha proving system, the kind of finding Alpha testing exists to surface, with the fix planned for V6.
Core contributors identified a critical vulnerability affecting the V5 Alpha proving system on 27 July 2026 through internal AI-assisted auditing.
V5 remains Alpha software. Critical findings can arise during this phase, and the audit process exists to identify them before broader deployment. This finding places V5 funds, applications, and contract state at risk.
Treat funds and applications on V5 as exposed to a protocol-level failure until contributors complete incident response work and operators carry out the required network actions.
An attacker may be able to exploit a flaw in the current V5 proving system by constructing a proof that passes verification for a transaction the network should reject. If accepted, that transaction could produce a state transition outside the rules V5 intends to enforce.
Contributors cannot determine whether anyone exploited the flaw before this finding. The affected system lacks the information needed to distinguish ordinary accepted transactions from transactions accepted through the flawed proving path. Historical chain activity cannot establish whether exploitation occurred or quantify its impact.
We expect application teams to prepare safeguards in the coming weeks.
Those safeguards may include changes to application controls, deployment procedures, user flows, and migration plans. We expect each team to assess its contracts and determine which protections fit its architecture and users.
We expect teams planning a V5 deployment to pause that work until contributors publish further guidance. We expect teams with live contracts to review their ability to limit user exposure, isolate affected functionality, and move users to fresh deployments if needed.
We expect applications that maintain administrative or emergency controls to assess whether those controls can reduce user risk during the incident timeframe.
Core contributors are working with operators, application teams, and bridge operators as applications add security guards around affected flows.
The findings from this incident will inform the V6 release, including circuit updates that prevent the network from accepting proofs tied to an affected proving system.
V5 launched as Alpha software, with V6 planned for later in 2026. Contributors will publish a security roadmap covering the remaining work and release path.
Reviewers have not identified other high-severity or critical V5 Alpha vulnerabilities at this time.
Internal and external human audits have completed, and contributors continue AI-assisted auditing. Alpha is the period for identifying faults before production deployment.
Dark Forest is a real-time strategy game played across a procedurally generated universe where most of the map is hidden. You cannot see rival players, their planets, or their fleets. You only know what you have explored. Everyone shares one universe, and nobody has the full picture.
In most onchain games, every position and every move is public, because the chain is public. Dark Forest used zero-knowledge proofs to break that assumption: players prove their moves are valid without revealing where those moves came from. The result is a game of hidden information running on a public network.
Dark Forest Aztec ports the original Dark Forest 0.6 to Aztec. It keeps the gameplay from the original and rebuilds the privacy layer on Aztec's programmable privacy.
A note before diving in: this is early, experimental software on Aztec Alpha V5. Treat it as an alpha and play accordingly.
You start on a single home planet with almost the entire map dark. To find anything you mine the universe, running a client that explores coordinates and reveals what sits there: unclaimed planets, resources, and eventually the edges of other players' territory.
You are never handed a view of the board. You earn it one region at a time, and everyone else works under the same fog.
Your home coordinates and your fleet movements are private state, expressed as first-class private notes on Aztec. Your location and where you send energy stay hidden, enforced in the contracts by zero-knowledge cryptography.
What sits onchain is a set of cryptographic commitments. Instead of storing every planet's full details in the open, the contracts store Poseidon2 hashes of entity state. When you make a move, your client supplies the full state, the contract checks it against the stored hash, applies the change under zero-knowledge constraints, and writes a new hash back. Full game state lives offchain and gets rebuilt from public logs by an indexer, which is what renders your map without exposing every player's position.
So you can prove you made a legal move from a planet you own without revealing where that planet is. Aztec applies the same principle to private payments and private contracts.
Four actions carry the game.
Explore. Your explorer sits in the bottom left. Set it running and it uncovers the map around you, surfacing planets, resources, and other players.
Send energy. Most planets produce energy. Click and drag from a planet you own toward a target to capture or weaken it.
Route silver. Asteroid fields produce silver. Move it to your planets and spend it on upgrades, or send it to a Spacetime Rip to convert it into score.
Hunt artifacts. Some planets hold artifacts. Your Gear ship discovers them. Once harvested, you deposit them on planets to boost stats.
Four stats drive most decisions.
Energy is the core resource. Planets generate it over time up to a capacity, and you spend it on everything: claiming planets, reinforcing your own, attacking rivals. Two details matter. Moves are taxed, so a flat percentage of a planet's total capacity burns every time you send energy, which discourages small frequent moves. And energy decays over distance, so send it too far and almost nothing arrives. A common rule of thumb is to let a planet fill to about 75%, then send it down to about 25%.
Defense reduces the damage incoming energy does when it lands. Higher-level planets often have lower defense, but they hold much more energy, so they still take more to capture. Defense matters most on front lines.
Range sets how far a planet can send energy. It governs how fast you expand and how efficiently you move energy inside your own empire, since shorter relative distances mean less decay. Good range also lets you strike deep into an opponent's territory.
Speed sets how quickly a move arrives. Usually secondary, though a fast strike can land before a rival reacts, and some playstyles reward capturing many nearby planets quickly.
Planets can also be upgraded with silver and enhanced with artifacts. Space types carry different multipliers, from mild Nebula to punishing Dead Space, so where a planet sits changes how it plays.
There is a scoreboard, and territory alone does not win it. This round scores two activities: discovering artifacts with your Gear ship, and withdrawing silver through Spacetime Rips.
Point values from the in-game help page:
Silver accrues one point at a time. A single Mythic artifact is worth twenty million of them, so artifact hunting decides rounds and silver withdrawal sets your floor.
Silver has two competing uses. Spend it on upgrades and your planets get stronger, extending range and hardening defense. Withdraw it through a Spacetime Rip and it becomes scored points, but it is gone. Every unit is a choice between building the empire and banking points.
Upgrades tend to win early, since a stronger empire reaches more asteroid fields and finds more artifacts. Late in a round that calculation flips, because a planet you never use is worth less than points already scored.
Artifacts do both jobs at once. They score on discovery, and once deposited they boost a planet's stats, which makes the next expedition easier.
Nothing happens until you find something to act on. Your explorer turns dark space into planets you can capture, asteroid fields you can mine, and artifact-bearing planets you can raid. Sitting still means no new energy, no silver, no score.
Exploring also buys information. The map you have uncovered is an advantage nobody else holds. Knowing where high-level planets sit, which asteroid fields are unclaimed, and where space types shift lets you plan further ahead than someone still working through their starting region.
You find other players as a byproduct. There is no player list. You explore outward until your revealed region touches territory someone already owns: a planet in another player's colors, sitting where you were about to expand. Their home coordinates stay private, so you learn something narrow. Someone is here, roughly this direction, holding this much. You infer the rest, and you have no way of knowing whether they found you first.
You have three broad options.
Stay quiet and keep growing. Nothing forces you to engage. Keep exploring elsewhere, keep routing silver, keep upgrading. Your positions stay private, so silence costs you only time, which is what you want if they are stronger. The risk is that they are doing the same thing faster.
Fortify the border. If the contact sits somewhere you cannot lose, spend energy hardening the planets facing them. Defense is worth most where an attack will actually land. This keeps the option to fight without committing to one.
Attack. Send enough energy to overwhelm the target's defense and the planet becomes yours, along with its production and its position as a staging post. Higher-level planets are the prize and take proportionally more to crack.
Attacking costs more than energy. A move that lands tells your rival where you strike from, and that you are close enough to be worth answering. Retaliation can then come from directions you have not explored, launched from planets you cannot see.
Everyone plays one shared universe in real time. No turns, no lobbies. Energy regenerates whether you are watching or not, moves stay in flight while you sleep, and rivals expand while you are away from the screen.
Most strategy games let you watch a threat approach. Here you tend to see the consequences: a planet you owned this morning in someone else's colors, an incoming move you notice once it is already close.
That produces a particular kind of paranoia. You are trying to find everyone else while avoiding being found, and every expansion is a strategic bet that the space ahead is empty.
Information becomes tradeable, because it is scarce. Players compare notes, warn each other about aggressive neighbors, and agree who expands where, then break those agreements when the scoreboard makes it worth breaking.
A fully onchain game where players cannot see each other's positions is hard to build, and building it well says something about the platform underneath.
Hidden state, private notes, and client-side proving are the same building blocks behind private applications across Aztec. Dark Forest is a way to watch them work.
Dark Forest Aztec is playable now as an alpha. Expect a learning curve; the original was famous for it. DFArchon maintains onboarding material and a community for new players. Round One is live. The universe is dark, and everyone else is out there somewhere. Go find them, quietly.
Gas on Aztec is known as Fee Juice and is used to pay for transaction costs. This is the same as $ETH on Ethereum. Some apps will handle transaction costs for you under the hood, but if you are using a browser extension wallet, you will not be able to send transactions without it. Fee Juice can be obtained by bridging the $AZTEC token on Ethereum to the Aztec Network L2. This means that under the hood, all activity that happens on Aztec is underpinned by the $AZTEC token bridged into the network. Some bridges like Shield (by human.tech) handle this for you, allowing you to allocate a portion of your bridged transaction to convert into Fee Juice and land in your wallet automatically.
Assets and transactions on the Aztec Network can be either public or private. If you bridge publicly, your tokens will arrive as public, traceable tokens visible to all. Privately bridging, on the other hand, will give you private assets that are visible only to you. These assets can then be sent privately to another user or wallet without ever revealing who you are, what tokens were sent, how many, or who the recipient is.
Like tokens on the Aztec Network, Fee Juice (gas) can also be public or private. The reason for this is that even if what you are sending is private, the gas you spend to execute that transaction could still be visible if you are using public Fee Juice, potentially revealing transaction patterns and activity. Private Fee Juice keeps your entire transaction footprint hidden. When you send a private transaction, you can use private Fee Juice, and when you send a public transaction, you can use public Fee Juice, which means your transaction costs are always aligned with the type of transaction you're making.
Aztec has native fee abstraction, which means apps could let you pay for transactions in any token you want, or cover your fees entirely. Apps like Nyx may choose to cover part or all of a user's transaction costs, or allow you to pay in tokens that are convenient for you. This means you will most likely never see Fee Juice in an app; instead, you'll pay in whatever makes sense for what you're doing, on your terms. Similarly, you might never even see an Aztec wallet at all, because the app itself becomes your interface that you connect to using your MetaMask wallet.
If you're using a browser extension like Azguard, you'll manage Fee Juice directly in your wallet alongside your private and public balances, converting between tokens as needed to cover transaction costs.
When you bridge tokens in, you'll need enough Fee Juice to cover the cost of your first transaction, then you'll need to monitor how much Fee Juice you have available to make transactions. Browser wallets will allow you to send either publicly or privately to other users and will default to using either public or private Fee Juice depending on the type of transaction. Both private Fee Juice and public Fee Juice will appear by default in your token list.
How you handle Fee Juice depends on where you're transacting: apps can abstract it away entirely and let you pay in any token, while a browser wallet like Azguard puts it in your hands to manage across public and private balances. Match your gas to your transaction, keep private activity private down to the fee, and you move on your terms.
The Aztec Network today activated Alpha V5, a major protocol upgrade passed by token-holder governance and executed onchain. Alpha V5 reduces private-transaction proving times by more than 2x compared to the previous version, lowers the cost of a fully private transaction by roughly 50%, resolves the critical issues found in V4, and sees the first wave of apps go live. Users can now send private transactions and earn yield on Aave simply by connecting their Ethereum wallets on Nyx, bridge from Ethereum to Aztec using Shield or TRAIN, privately collect NFTs on RavenHouse, or play Dark Forest Aztec, a hidden-information strategy game in a universe that lives entirely onchain.
"Alpha V5 continues Aztec's work at the frontier of client-side proving, with cryptographic breakthroughs that cut proving times by more than half this release," said Zac Williamson, Co-founder, Aztec Foundation. "We believe Aztec is now the fastest system in the world for proving a fully private transaction entirely on a user's own device, and every release moves the industry closer to private transactions at public transaction speeds."
As the only decentralized privacy L2, Aztec is the credibly neutral privacy layer for Ethereum. Aztec allows anyone to write smart contracts that include both private and public aspects – every private transaction is proven on the user's own device, so no operator, sequencer, or intermediary can see the data. The Alpha V5 proving improvements come from cryptographic advances that make this client-side proving faster than any prior release. The network remains in alpha, but with V5 it is ready for teams to begin building and deploying applications.
Making private transactions practical comes down to how quickly a proof can be generated on a user's own device, without offloading that work to a server that would learn what the user is doing. On Alpha V5, proving a private token transfer natively now takes approximately 2.5 seconds on a consumer laptop, down from 5.2 seconds on V4, and about 6.8 seconds in a browser, down from 12.5 seconds. Across every measured transaction flow, client-side proving times improved by approximately 2x compared with V4.

Alpha V5 lowers ECDSA signature-verification cost by approximately 2x, speeds up Poseidon2 hashing by approximately 3x, and reduces the protocol circuit gate count by approximately 50% (gate count is the number of individual operations a proving circuit must perform, and it is the main driver of how long a proof takes to generate). Each of these lowers the amount of work a device performs to prove a transaction, and the reduction in gate count in particular compounds across every proof the network generates.
Alpha V5 launches the first wave of apps on a network where privacy is built into the protocol rather than managed by an operator. On other networks that claim privacy, transactions still pass through an operator or node that reads them in plaintext, or depend on a viewing key that a third party holds, so users rely on someone else to protect their data and to decide when it gets disclosed. On Aztec, every private transaction is proven on the user's own device, so the app, the sequencer, and any operator never need to see the underlying data. Nyx is one of these apps, allowing users to privately send transactions and privately earn yield on Aave.
"On Ethereum, everything you do is public. That's why we built Nyx: a private account governed by your Ethereum wallet", said Nikhil, Co-founder of Nyx. "Now you can send, receive and earn in private. Nyx was the first app live on the Aztec Alpha, and we're excited to expand participation to more users with the added stability of Alpha V5."
Other apps on Alpha V5 include Azguard and Nethermind (wallets), Shield, TRAIN, and RavenHouse (bridges), and the Aztecscan block explorers. Also launching is Dark Forest Aztec, a game where users explore a universe, control planets, manage planetary energy, expand territory, and launch attacks through strategic play with private state and hidden actions.

Transaction fees on Aztec come from two main sources: the cost of proving a transaction and the cost of verifying the rollup proof on Ethereum. Alpha V5 reduces both. It lowers the network's proving-cost parameter by 50%, and it reduces the L1 gas required to verify a rollup proof by approximately 40%. Because rollup proofs are verified on Ethereum and that cost is shared across all transactions in a batch, the L1 reduction lowers fees for every user, while the lower proving-cost parameter reduces the per-transaction proving fee directly. Together, these bring the average cost of a fully private token transfer to under a $0.05 transaction cost.
Alpha V5 also hardens the network on several fronts. It resolves critical vulnerabilities found in Alpha V4 along with additional bugs discovered since launch. Aztec's bug bounty program on Cantina also drew more than 234 security researchers to participate. The network remains in alpha, and further bugs may surface as usage grows, but each release has closed the issues found in the last and strengthened the protocol against new ones. With the critical V4 issues resolved and these safeguards in place, Alpha V5 is stable enough for teams to begin building and deploying applications.
Alpha V5 is live now, view the Alpha V5 landing page for a full list of features, performance updates, and live apps to explore.
Aztec is the only decentralized, privacy-first Layer 2 on Ethereum. Developers write private and public logic in the same smart contract, and private functions are executed and proven on the user's own device, so no operator sees the underlying data. The protocol is upgraded through onchain governance, and the network settles to Ethereum. For more information, visit aztec.network.
On Ethereum today, each transaction reveals everything publicly. The token you moved, the size, the timing, the wallet it came from, every action you take. Given the limitations of this type of transparent network, the industry is now focusing on bringing privacy onchain as a top priority. The response to this has mostly been to enable private transactions that shield transfers in various ways. But when we look at how privacy works on Web2, it’s clear that users and developers need granular privacy controls: the ability to decide what is public or private and who is able to see different types of data.
Aztec was built so that one transaction can carry two halves. A private half that runs on your own device and never leaves it, and a public half that the network runs in the open. Apps can choose which aspects are private or public, and users can choose what they want to reveal and when.
This article will follow an example transaction on Aztec: a vote in an onchain election built on Aztec, where who you are and which candidate you chose stay private, while the running tally for each candidate stays public for anyone to verify.
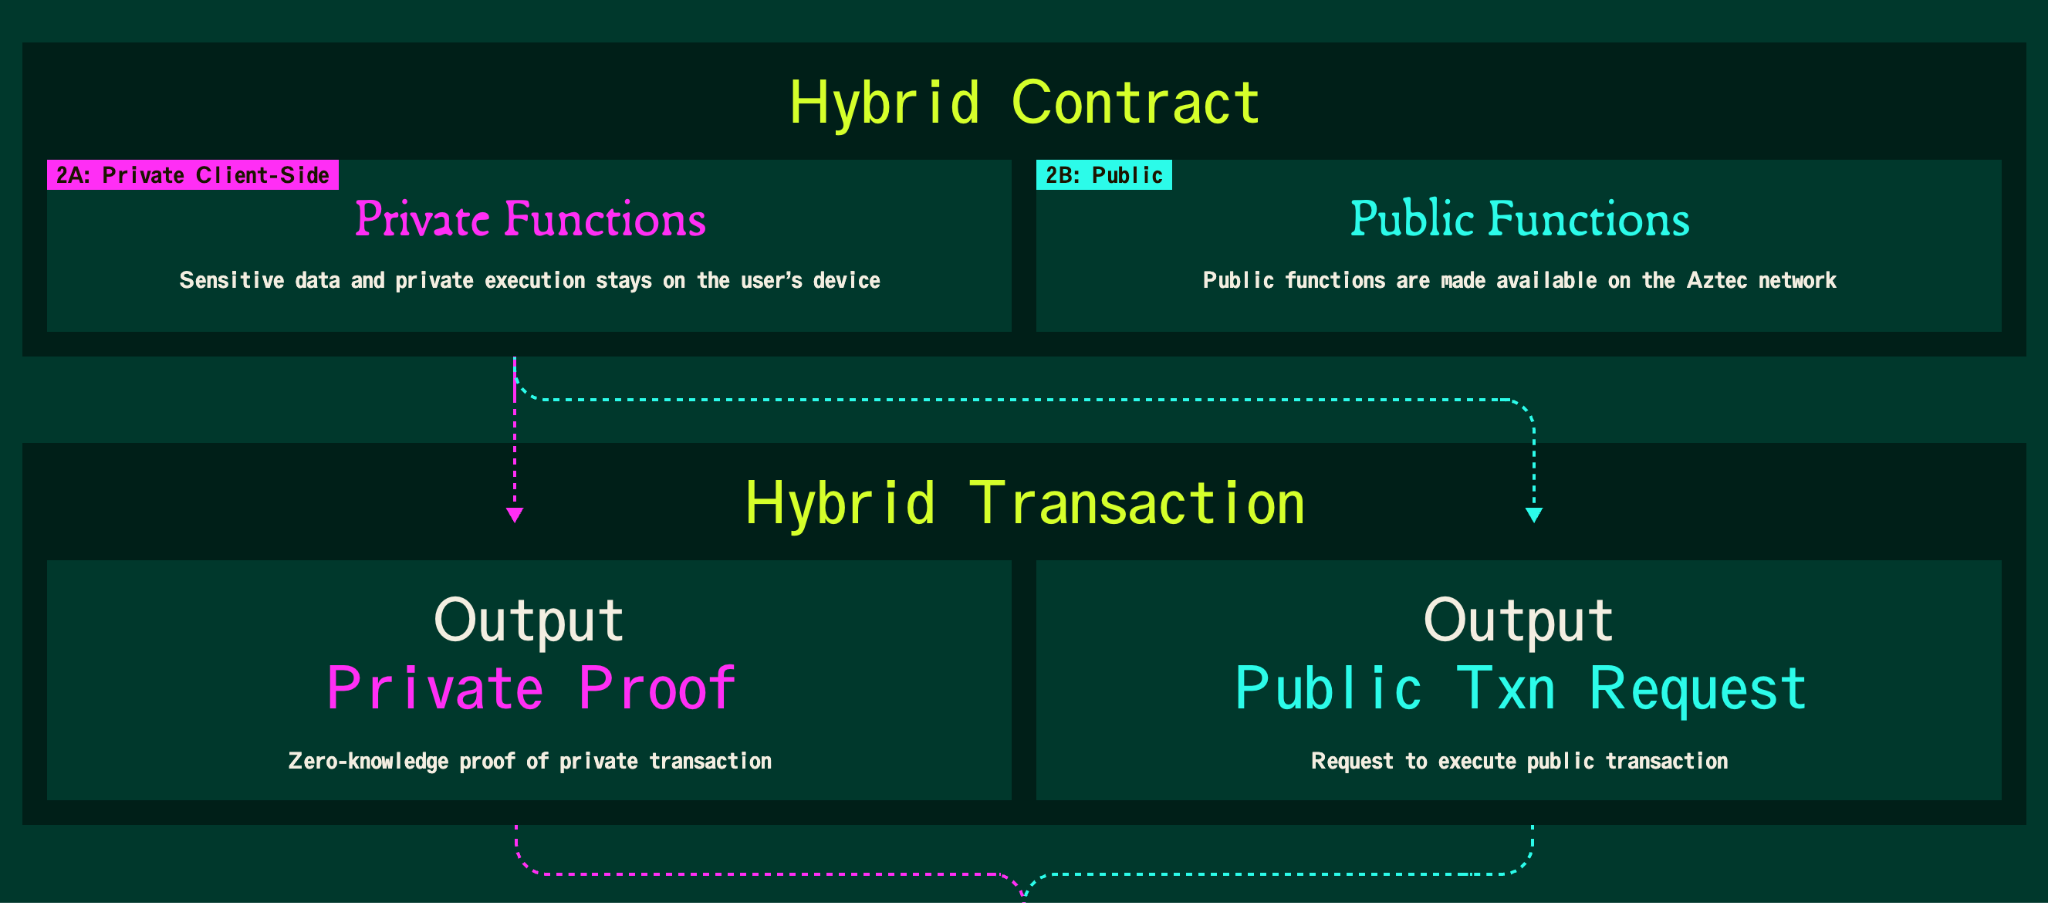
Picture the vote you cast in our example as two aspects that seamlessly weave together. In the first step, you act in private: an app records your vote on your device and hands the network a proof that the vote is valid without revealing it. In the second, the network acts in public: it checks that proof, then adds one to the chosen candidate's public tally. It is one transaction: one part stays with you, one part goes to the network. Both parts end up recorded onchain, in two separate state trees, one private and one public. The walkthrough below follows how these two aspects work together and what this means for how your transaction lands onchain.
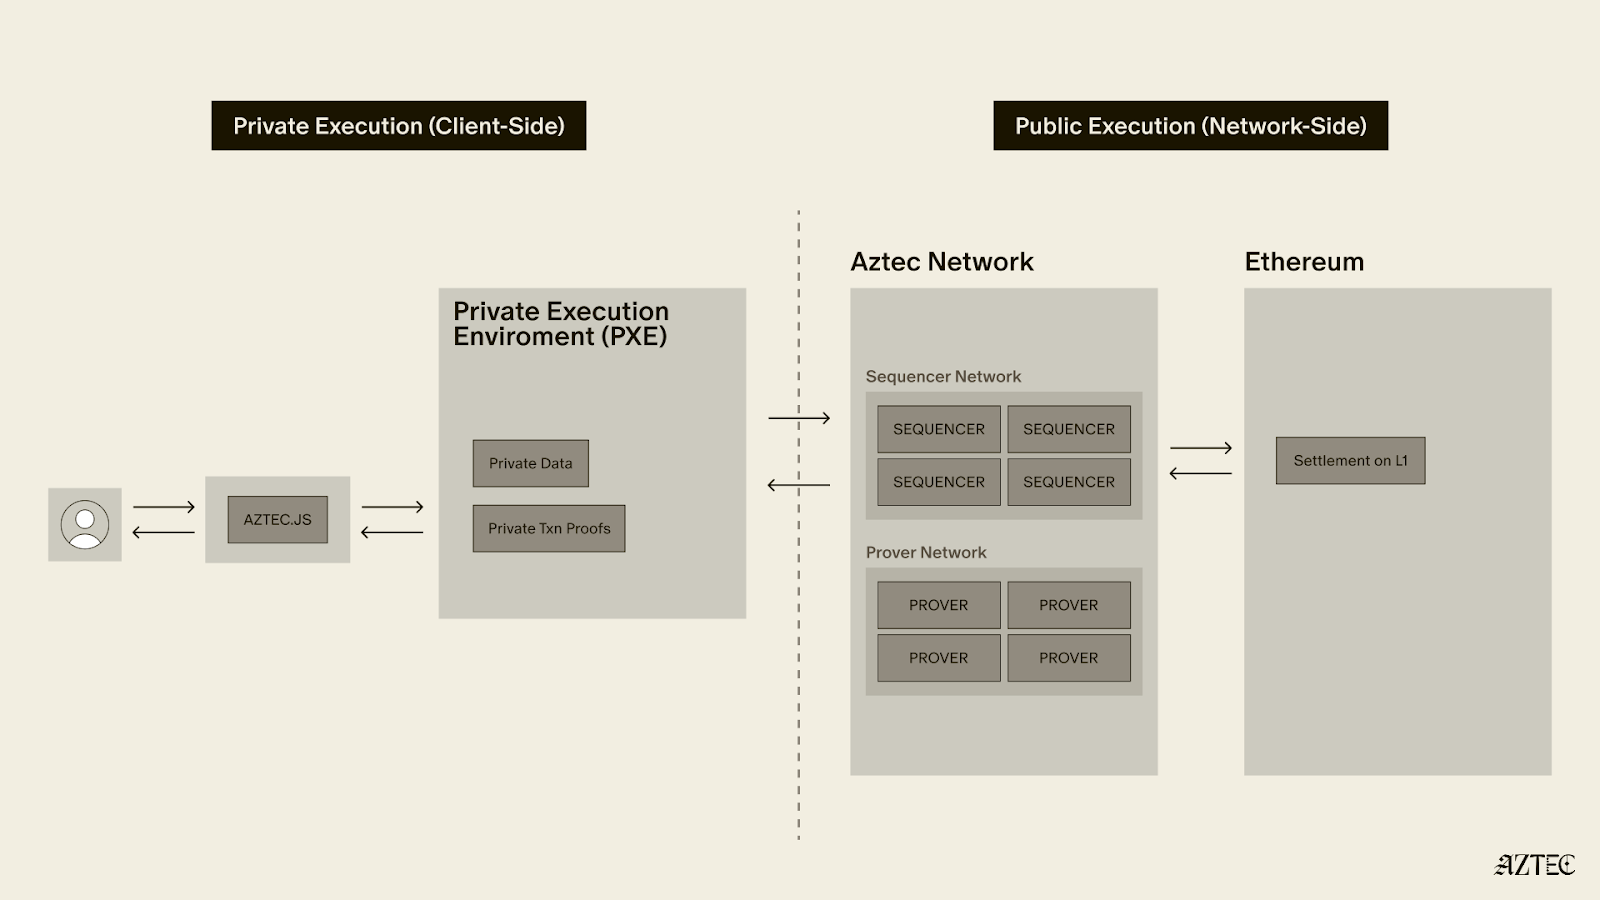
You open the voting app and connect an Aztec wallet. That first step looks like any onchain app. The difference is inside the wallet. An Aztec wallet carries a private execution environment, the PXE, pronounced "pixie", which runs on your phone or in your browser. The PXE is where the private half of your transaction executes, and where the proof of that work gets made, on your hardware, under your exclusive control.
Every account on Aztec is a smart contract rather than a bare key. That design, account abstraction, allows a wallet to authorize a transaction however its owner chooses without writing an identity onto the network for everyone to read. The wallet is the front door, and on Aztec you can decide if the door is open or closed, who you share your information with.
The voting app is a smart contract with two kinds of functions. The private functions run first, and they run inside your PXE. Your identity and the candidate you picked are the private inputs, and they stay on your device.
The only thing to leave your device is a proof confirming the legitimacy of your vote. Aztec's client-side proving system, Chonk, takes the private execution and produces a zero-knowledge proof: a compact cryptographic receipt that your vote followed the rules, that you are eligible, and have not voted before, while revealing nothing about who you are or who you voted for. Think of it as a sealed ballot the network can confirm is valid without opening it. The network learns only that a legitimate vote happened. It does not learn how you voted, or even which account voted.
This is the part that used to be too slow to be practical. Generating a proof on a phone was the bottleneck every privacy app hit. Aztec’s Chonk is purpose-built for fast proving on low-memory devices, both natively and in the browser, so the private half runs on the device in your hand instead of on someone else's server.
Some elements of a vote should be public. The tally is shared infrastructure, the number everyone relies on to trust the result. Thanks to programmable privacy on Aztec, the app marks that part public. Public functions live on the network and run in the open, the way functions do on Ethereum.
On Aztec, private and public logic live in the same contract, and the developer decides which is which, function by function and variable by variable. Programmable privacy is a dimmer, not a switch. The voting app turns it up on the individual ballot and turns it down on the running tally. That boundary is a design decision written into the contract, and it is the thing no transparent chain and no fixed-privacy chain can offer.
Your vote leaves your device as a bundle: the zero-knowledge proof of the private half, plus the call to the public function that updates the count. It goes to Aztec's sequencers, a decentralized set of thousands of independent operators, with more than 3,500 of them running the network today.
The sequencers do two jobs at once. They verify the proof of your private vote, confirming it is valid and eligible without seeing the choice behind it, and they run the public function that adds one to the chosen candidate and updates the public tally. Your ballot stays sealed. The count goes up by one for everyone to see. The same proof guarantees you cannot vote twice, even though no one learns which ballot is yours.
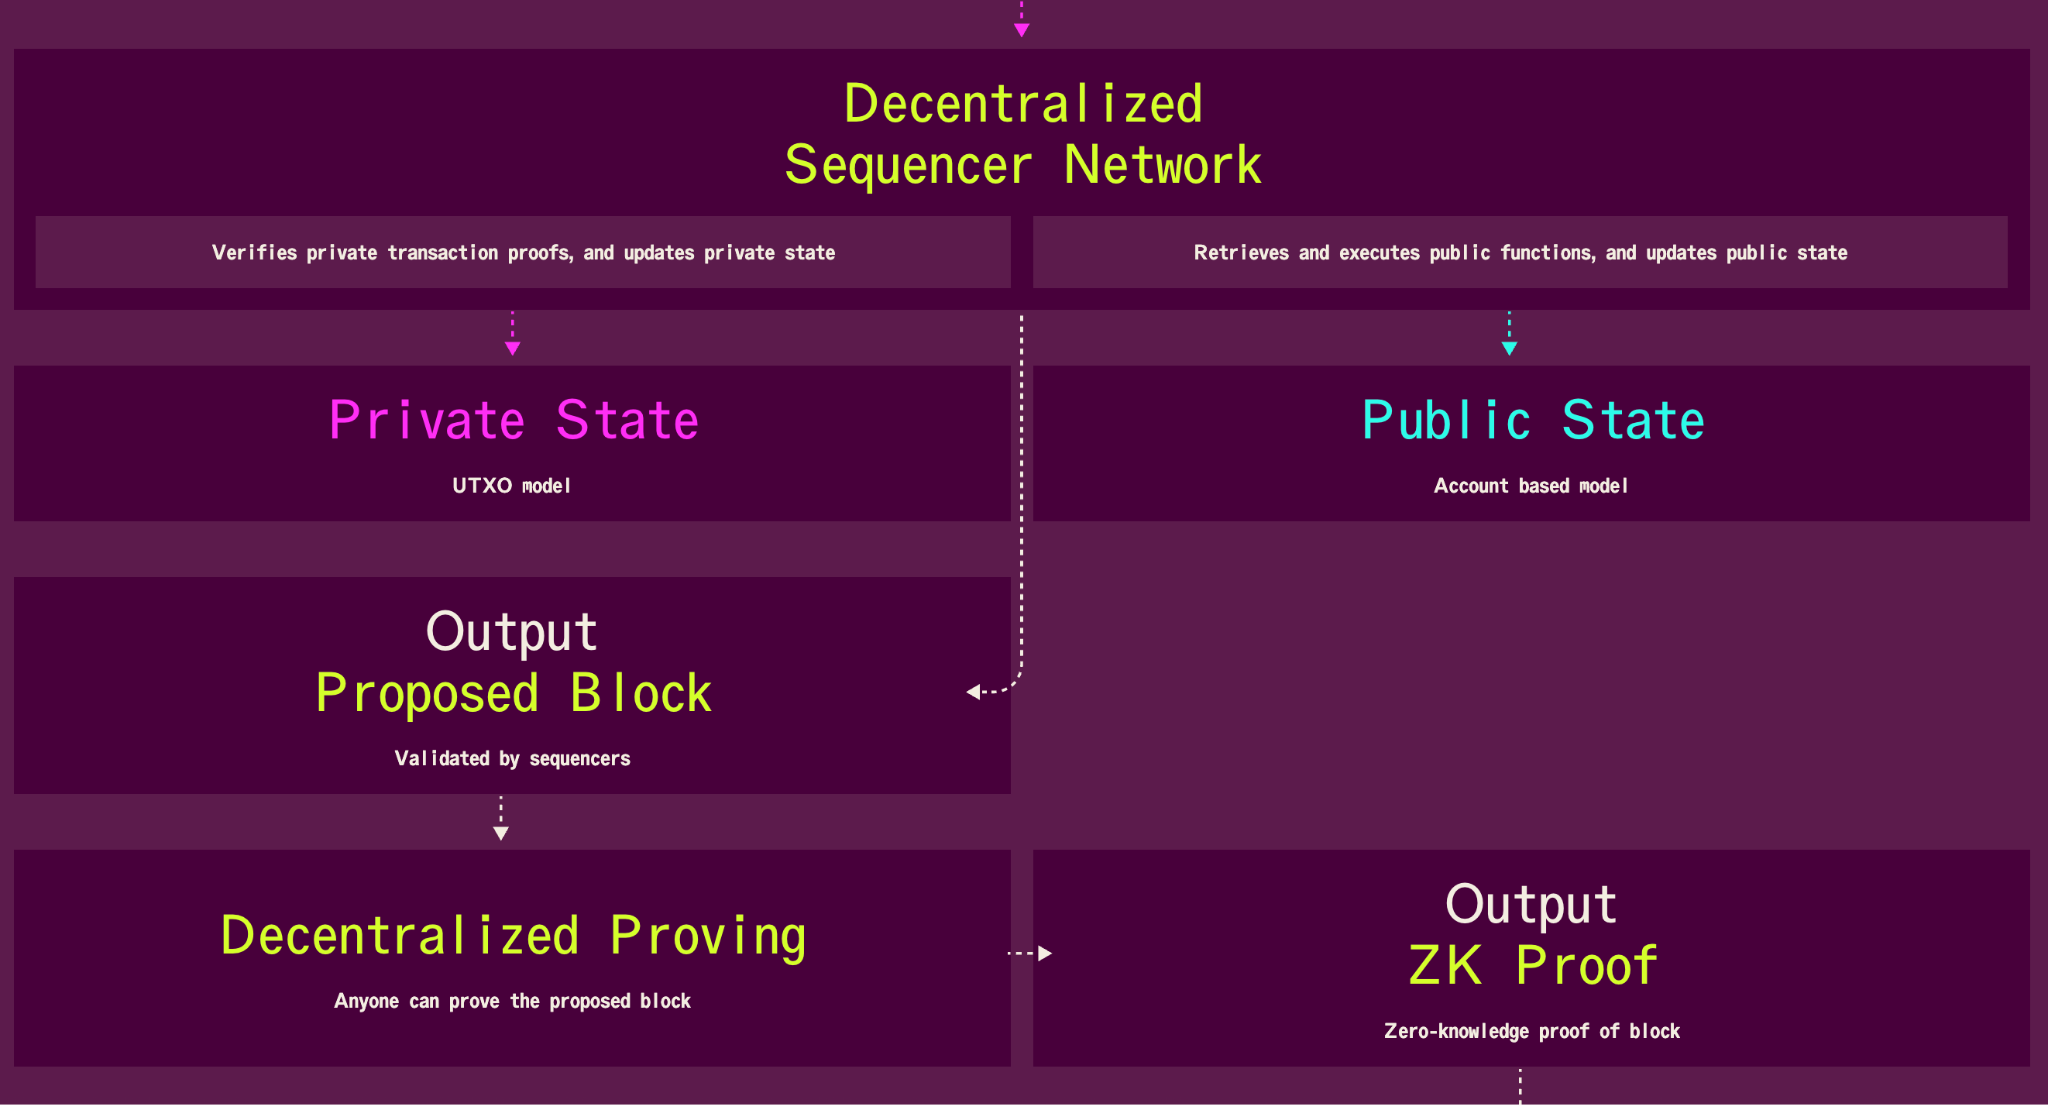
Aztec has two main state trees, and both live onchain. One holds private state, the other holds public state, so the full record of what happened sits on the network rather than on any one person's laptop. The two trees store each record in two different ways depending on if it needs to be private or public.
The private tree uses a UTXO model, the same note-based design used by Zcash. In this model, state is written as commitments: each entry is a sealed record that a valid vote was cast, with the voter and the choice kept private. Just like with Zcash or Bitcoin, you do not edit a private entry in place. You write a new one, and the design stops the same vote from being cast twice (old state is nullified). The vote stays private, and the record of a legitimate vote happening is onchain for the network to check.
The public tree uses an account-based model, the same shape Ethereum uses: values that update in place, readable by anyone. This is where each candidate's tally lives.
One transaction wrote information to both trees. The private tree recorded that you voted, sealed. The public tree recorded the new totals, in the open. Everything is onchain. The difference between the two trees is how much each one reveals.
Every private app on Aztec writes into that same private tree. A vote, a payment, and a payroll run all land in one shared record of activity, so each user's privacy grows stronger as the network grows, instead of splitting into a separate pool for every app.
Aztec is an L2 on Ethereum, so everything settles to Ethereum L1. A sequencer on Aztec gathers transactions into a proposed block. Other sequencers validate it before it goes to Ethereum's pending chain. At that point the block sits on Ethereum, ordered and recorded, waiting for its proof. The network has agreed on what happened and the proposed block is just waiting a final proof.
Proving a block is its own job, and on Aztec, it belongs to no one in particular. A decentralized, permissionless set of provers competes to take a full epoch, a 32-block stretch of the chain, and compresses it into a single zero-knowledge proof of the entire epoch. Anyone with the hardware can run a prover and bid for the work. There is no privileged operator, no committee you have to trust, no outside network holding a key.
That openness is the whole point of a privacy layer. A system that protects your data but routes it through one trusted server has only moved the exposure rather than removed it. Aztec keeps proving permissionless and your private inputs on your device, thereby avoiding any exposure.
The economics land in the voter's favor too. As an L2 network, Aztec spreads the cost of that one L1 proof across thousands of transactions in the rollup, so a vote costs pennies, not the millions of gas a private proof would cost verified alone on Ethereum.
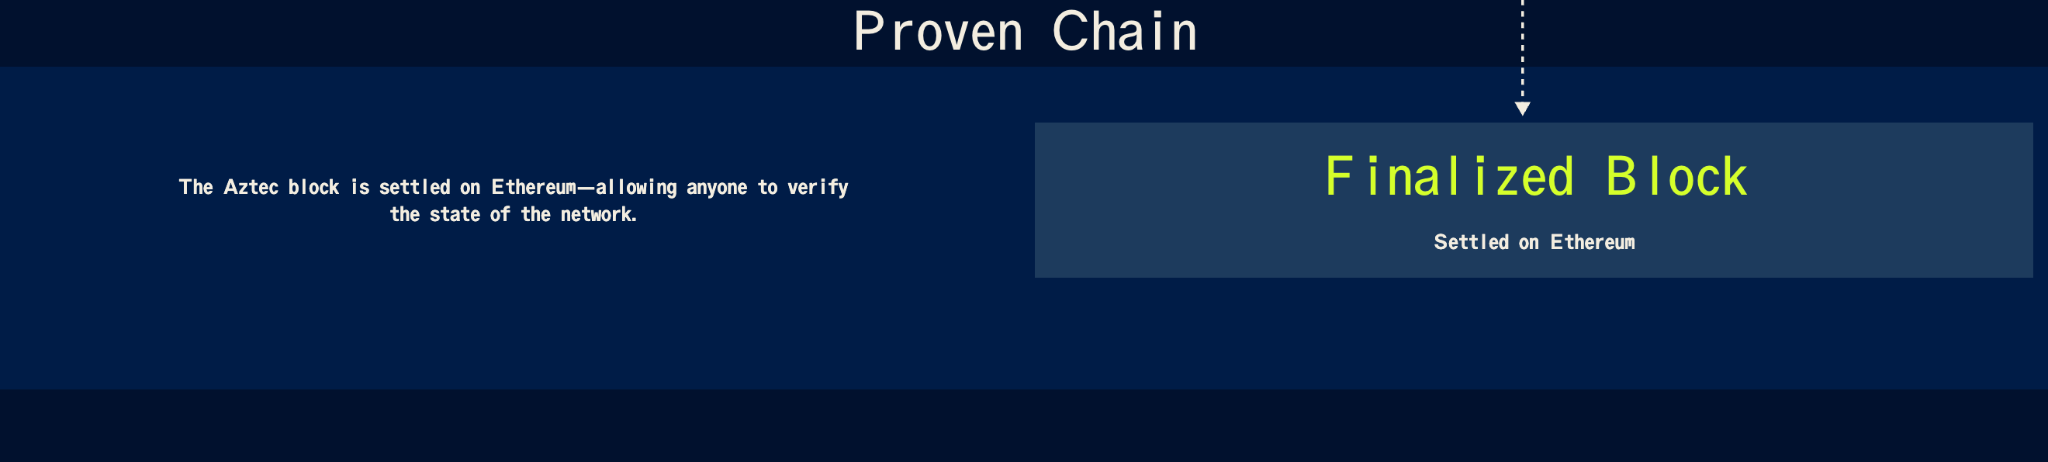
A prover then posts the epoch proof to Ethereum's proven chain, and the Aztec state is final. Ethereum verifies one proof and inherits the correctness of everything inside it. Aztec extends Ethereum and settles to Ethereum, so your hybrid transaction carries Ethereum's security without carrying Ethereum's enforced transparency.
Anyone can now verify that the result is valid and that every counted vote was legitimate. No one can see how any individual voted. The tally is on the shared ledger where it belongs, and your ballot stayed yours the whole way through.
For the voter, their ballot was never a broadcast. The candidate you chose stayed yours, with no record tying your wallet to a name for anyone to read later, and you can still check that your vote was counted and the result is honest. You took part without your choice becoming data for systems built to act on it.
For a founder, the election app in this walkthrough is easy to implement without needing to build extensive custom code. Secret ballots with a public, verifiable count, in one contract, is a product category that opens up only because the boundary is programmable. You can build governance, elections, and polls where people vote without fear and the result still proves itself. And of course you can build anything that requires both public and private state to work seamlessly together.
For an infrastructure provider, the same machinery serves clients who need a result they can stand behind without exposing the people who produced it. Selective disclosure lets a client prove exactly what a counterparty needs to see, the count and the integrity of the process, and protect everything else, on their own terms. That is a guarantee a transparent chain cannot make.
A real vote needs two things at once: a secret ballot and a count anyone can check. A transparent chain makes you give up the first to get the second. On Aztec, you get both. The tally settled on Ethereum for anyone to verify, and how you voted stayed yours. The infrastructure is in place, what will you create with it?
The Aztec Network today activated Alpha V5, a major protocol upgrade passed by token-holder governance and executed onchain. Alpha V5 reduces private-transaction proving times by more than 2x compared to the previous version, lowers the cost of a fully private transaction by roughly 50%, resolves the critical issues found in V4, and sees the first wave of apps go live. Users can now send private transactions and earn yield on Aave simply by connecting their Ethereum wallets on Nyx, bridge from Ethereum to Aztec using Shield or TRAIN, privately collect NFTs on RavenHouse, or play Dark Forest Aztec, a hidden-information strategy game in a universe that lives entirely onchain.
"Alpha V5 continues Aztec's work at the frontier of client-side proving, with cryptographic breakthroughs that cut proving times by more than half this release," said Zac Williamson, Co-founder, Aztec Foundation. "We believe Aztec is now the fastest system in the world for proving a fully private transaction entirely on a user's own device, and every release moves the industry closer to private transactions at public transaction speeds."
As the only decentralized privacy L2, Aztec is the credibly neutral privacy layer for Ethereum. Aztec allows anyone to write smart contracts that include both private and public aspects – every private transaction is proven on the user's own device, so no operator, sequencer, or intermediary can see the data. The Alpha V5 proving improvements come from cryptographic advances that make this client-side proving faster than any prior release. The network remains in alpha, but with V5 it is ready for teams to begin building and deploying applications.
Making private transactions practical comes down to how quickly a proof can be generated on a user's own device, without offloading that work to a server that would learn what the user is doing. On Alpha V5, proving a private token transfer natively now takes approximately 2.5 seconds on a consumer laptop, down from 5.2 seconds on V4, and about 6.8 seconds in a browser, down from 12.5 seconds. Across every measured transaction flow, client-side proving times improved by approximately 2x compared with V4.
Alpha V5 lowers ECDSA signature-verification cost by approximately 2x, speeds up Poseidon2 hashing by approximately 3x, and reduces the protocol circuit gate count by approximately 50% (gate count is the number of individual operations a proving circuit must perform, and it is the main driver of how long a proof takes to generate). Each of these lowers the amount of work a device performs to prove a transaction, and the reduction in gate count in particular compounds across every proof the network generates.
Alpha V5 launches the first wave of apps on a network where privacy is built into the protocol rather than managed by an operator. On other networks that claim privacy, transactions still pass through an operator or node that reads them in plaintext, or depend on a viewing key that a third party holds, so users rely on someone else to protect their data and to decide when it gets disclosed. On Aztec, every private transaction is proven on the user's own device, so the app, the sequencer, and any operator never need to see the underlying data. Nyx is one of these apps, allowing users to privately send transactions and privately earn yield on Aave.
"On Ethereum, everything you do is public. That's why we built Nyx: a private account governed by your Ethereum wallet", said Nikhil, Co-founder of Nyx. "Now you can send, receive and earn in private. Nyx was the first app live on the Aztec Alpha, and we're excited to expand participation to more users with the added stability of Alpha V5."
Other apps on Alpha V5 include Azguard and Nethermind (wallets), Shield, TRAIN, and RavenHouse (bridges), and the Aztecscan block explorers. Also launching is Dark Forest Aztec, a game where users explore a universe, control planets, manage planetary energy, expand territory, and launch attacks through strategic play with private state and hidden actions.
Transaction fees on Aztec come from two main sources: the cost of proving a transaction and the cost of verifying the rollup proof on Ethereum. Alpha V5 reduces both. It lowers the network's proving-cost parameter by 50%, and it reduces the L1 gas required to verify a rollup proof by approximately 40%. Because rollup proofs are verified on Ethereum and that cost is shared across all transactions in a batch, the L1 reduction lowers fees for every user, while the lower proving-cost parameter reduces the per-transaction proving fee directly. Together, these bring the average cost of a fully private token transfer to under a $0.05 transaction cost.
Alpha V5 also hardens the network on several fronts. It resolves critical vulnerabilities found in Alpha V4 along with additional bugs discovered since launch. Aztec's bug bounty program on Cantina also drew more than 234 security researchers to participate. The network remains in alpha, and further bugs may surface as usage grows, but each release has closed the issues found in the last and strengthened the protocol against new ones. With the critical V4 issues resolved and these safeguards in place, Alpha V5 is stable enough for teams to begin building and deploying applications.
Alpha V5 is live now, view the Alpha V5 landing page for a full list of features, performance updates, and live apps to explore.
Aztec is the only decentralized, privacy-first Layer 2 on Ethereum. Developers write private and public logic in the same smart contract, and private functions are executed and proven on the user's own device, so no operator sees the underlying data. The protocol is upgraded through onchain governance, and the network settles to Ethereum. For more information, visit aztec.network.
Crypto is in a long night. It is no secret that the industry is facing challenging circumstances and there has been a clear consolidation of the industry. Right now we are seeing a focus on real traction, demonstrable value projects shipping practical solutions that will meaningfully reach users.
Some of that discipline is overdue. However, in times like these the properties that made crypto structurally different begin to look expendable. Decentralization slows you down. It makes upgrades harder. It makes institutional sales harder. It removes the control surfaces that the existing financial world knows how to buy.
We used to accept those costs as the price of building something durable. But, in a famine, they look like unaffordable affectations. Discarding them wholesale, however, is like selling the land out from under our feet.
Permissionless, uncensorable transaction networks with rich composability - this is the clay from which our industry was grown. The long term commercial health of our industry depends on preserving these properties in an age of privacy and institutional adoption.
These trade-offs become more challenging and pernicious when privacy is involved. Privacy is the narrative for crypto in 2026, and for good reason. It’s the missing piece that will deliver the traction and real use-cases that the industry so desperately needs.
The challenges of decentralization multiply under the constraints of privacy and what we are seeing in the industry is not a pivot, but a complete capitulation of all of the differentiable value that made crypto valuable.
I have spent nearly a decade building a network that marries programmable privacy with decentralization. A network where users keep their data, where applications are composable with one another, where transactions can settle without a privileged party learning everyone’s business or deciding which products are allowed to exist. That required new cryptography, new programming models, new state architecture, new wallets, and a fairly insane number of tradeoffs that are invisible until you try to build the thing yourself. There are easier products to ship.
A centralized privacy service can give institutions something legible quickly, replicating how the existing financial sector works: a responsible operator, a viewing key, a way to block transactions, a way to explain the whole thing to a risk committee. Some of these products will be useful. Some will be good businesses. But they are not the thing we came here to build.
Institutional and enterprise adoption is one of the core growth areas in this crypto-winter and the playbook is simple: use the language of crypto as a skin-suit to sell products and services that pattern match onto existing financial rails, with their need for complete visibility, censorship, centralized network operators and all of the liabilities this incurs.
This is a tempting bargain because it shortens the path to adoption. It gives buyers and regulators a shape they understand. A company. A contract. A switch. But the moment you accept that bargain, the system changes character. It may still be encrypted. It may still contain proofs. It may still call itself private. But, it now behaves like and is an operated service.
There is a party with privileged knowledge and privileged control. Builders must shape themselves around it. Institutions negotiate with it. Regulators may pressure it. Attackers target it. Users ultimately depend on it. By a backdoor I mean something specific: a network or protocol-level viewing key where the product developer does not control who can see their users’ data, especially when paired with network-level controls that can block transactions or ban smart contracts entirely. I do not mean application-level controls. I do not mean user-authorised disclosure. I do not mean a dapp deciding that users must prove something before using it. Regulated applications will need rules. The issue is that the disclosure boundary of your application belongs to somebody else, and the same layer that sees can also decide whether your users are allowed to transact. In short, users lack a platform that has credible neutrality.
Privacy on top of centralized rails is fatal. If one party can see everything and stop anything, that party may be treated as responsible for seeing and stopping.
This compounds into substantial platform risk. If an entity builds on top of such a system they must surrender visibility and control to the network operator to satisfy their liabilities without consideration for yours. Decentralization and ultimately credible neutrality is the difference between whether you own durable infrastructure or are renting a service whose rules can change on a whim. Worse, you cannot “just build things”. For novel transaction flows approval must be sought and granted. Tell me, would Ethereum have grown if every smart contract deployment required approval from the Ethereum Foundation?
Privacy needs the same freedom. A private credit market, for example, touches identity, collateral, repayment history, payment flows, liquidation logic, lender disclosures, auditor access and borrower privacy. If every component lives inside a different permissioned service, each with its own operator and viewing assumptions, that is a bureaucratic friction that negates blockchain’s core value proposition; composability.
A decentralized and credibly neutral privacy network prevents the settlement layer from becoming the single place where all surveillance and censorship obligations naturally accumulate. It allows product developers to scope their code to satisfy their own narrow requirements without consideration for the obligations of a centralized operator.
A lot of today’s privacy narrative treats architecture as if it were a detail. It is not. You cannot take a transparent ledger, staple confidentiality onto the edge, add a viewing key for comfort, and expect to get programmable private infrastructure.
If the state model is not private from the ground up you get wrappers, third party tools, data custodians, ad hoc disclosure paths and a pile of assumptions that every application drags into the next. Developers do not get a normal programming model where private contracts can call private contracts and users keep state on their own devices. They do not get composability.
The difference matters. In a real private execution environment, users generate transactions locally. They do not outsource their intent to a third party who learns what they are doing. Private contracts interact through a state model designed for privacy. The network settles proofs without becoming the party that knows everyone’s business. Privacy is part of the architecture.
This is why Aztec has taken so long. We built something that makes programmable private state and decentralised settlement live inside the same system. That means proving systems that run on consumer hardware, a transaction architecture built around local private execution, and a programming model where privacy is idiomatic and just works out of the box.
A centralized service can skip much of this. It can hold the key, run the prover, approve the flow and call the result privacy. It gets to market faster because it is not trying to arrive at the same place.
Adding decentralization does not make obligations disappear. Applications, issuers, frontends, custodians and regulated businesses will continue to exist in a web of obligations and responsibilities. Anyone pretending otherwise is unserious.
The question is where those obligations live. If they are pushed into the settlement layer, the settlement layer is no longer credibly neutral. It needs visibility into everyone and controls over everyone.
The better answer is selective disclosure. Users and applications should prove specific facts to specific parties for specific purposes. A regulated application may need to know that a user passed a check, that a transaction satisfies a policy, or that an auditor can inspect a particular flow. None of that requires the base network to hold a permanent key into everyone’s activity.
This will be harder to explain to the existing world. New infrastructure always fails to fit the categories built for the old infrastructure. Bitcoin did not arrive as a neatly regulated bank product. Ethereum did not wait for every lawyer to understand smart contracts. Stablecoins and DeFi forced institutions, regulators and users to develop new language around rails that kept existing.
If the standard for privacy infrastructure is to plug into the old world without changing anything, the answer will always be a service with a backdoor. And the result will be to catch crumbs falling from the tables of the old world.
The market we should be building is, well, a market. A private financial system that compounds: assets, liquidity, identity, credentials, credit and applications interacting through a shared settlement layer without forcing users to surrender their data to whoever sits in the middle.
Traditional finance is built out of vertically integrated information silos. Those silos are its moat. Banks, exchanges, custodians, payment processors and data brokers all benefit from controlling the information that flows through them. A global private settlement layer attacks that advantage directly. It lets liquidity and credentials move while outsourcing information custody to neutral cryptographic infrastructure.
A company wants a moat. A settlement layer wants surface area. A permissioned privacy provider can ration access, raise fees, exclude applications, shape disclosure rules and define acceptable use around its own risk tolerance. These are products pretending to be networks, and not durable financial infrastructure. What bothers me is this compounding category confusion. Networks adding protocol-level viewing keys and transaction controls are using the same language as decentralised programmable privacy, and commentators are treating them as variations of the same thing. They are not.
We have spent nine years walking the hard road. Now, just as we are close, the market has lost faith. Everyone is reaching for whatever lifeline looks immediate. Some of those lifelines will be real. Some will make money. But if crypto responds to its long night by rebuilding financial privacy as permissioned services, then we will have survived by surrendering the property that made the industry worth building.
Markets can grow when the platform is removed from the position where it can dictate the rules. It would be perverse to forget that lesson while building privacy, the domain where control over information matters most.
Crypto is in a famine. The land is struggling. We could sell our land for a pittance and survive the season. But the famine will pass, and when it does the land will blossom again. Without the land we are nothing.
We have struggled immensely to create a permissionless network that can marry privacy with decentralisation: an indestructible network whose users cannot be surveilled and whose transactions cannot be censored. This is the soil we have to grow our crops. To surrender a backdoor or a centralized operator for temporary relief is to sell our land for the price of a stablecoin. And we cannot sell the land.
Follow Zac on X to get more insights
Follow Aztec on X for updates & breaking news
Privacy has become a baseline requirement for L1s and L2s who care about bringing real-world users onchain. Users don't want their activity broadcast to competitors or the general public, but applications operating at scale also need some form of auditability, whether for regulators, compliance requirements, or tax reporting. Selective disclosure resolves that tension: privacy by default, with the ability to prove specific facts when required. What separates these networks is not whether they offer that switch, but who gets to hold it.
Aztec, Canton, Starknet, Tempo, and zkSync all offer some form of privacy with selective disclosure, but under the hood they make fundamentally different architectural decisions about who can see your data and who can turn your privacy off. Those decisions determine whether your privacy stays under your own control or sits behind a switch that someone else operates.
Three questions reveal where these networks actually diverge:
The answers determine whether your privacy off-switch is held by a policy, by an operator's good behavior, or by you alone through a cryptographic proof. As you'll see in this post, there are legitimate reasons to use each one with different tradeoffs. Aztec is the only network, however, where that switch stays in the user's hands, answering all three questions without putting a permissioned set of operators or a standing viewing key in control of your privacy. That gives developers the flexibility to build apps that comply with applicable laws while still keeping full privacy under the user's control.
This article will compare the privacy approaches of Aztec, Canton, Starknet, Tempo, and zkSync to give developers insight into the privacy tradeoffs of each network.
Here’s how each network handles the selective disclosure privacy off-switch, and who has control over your privacy:
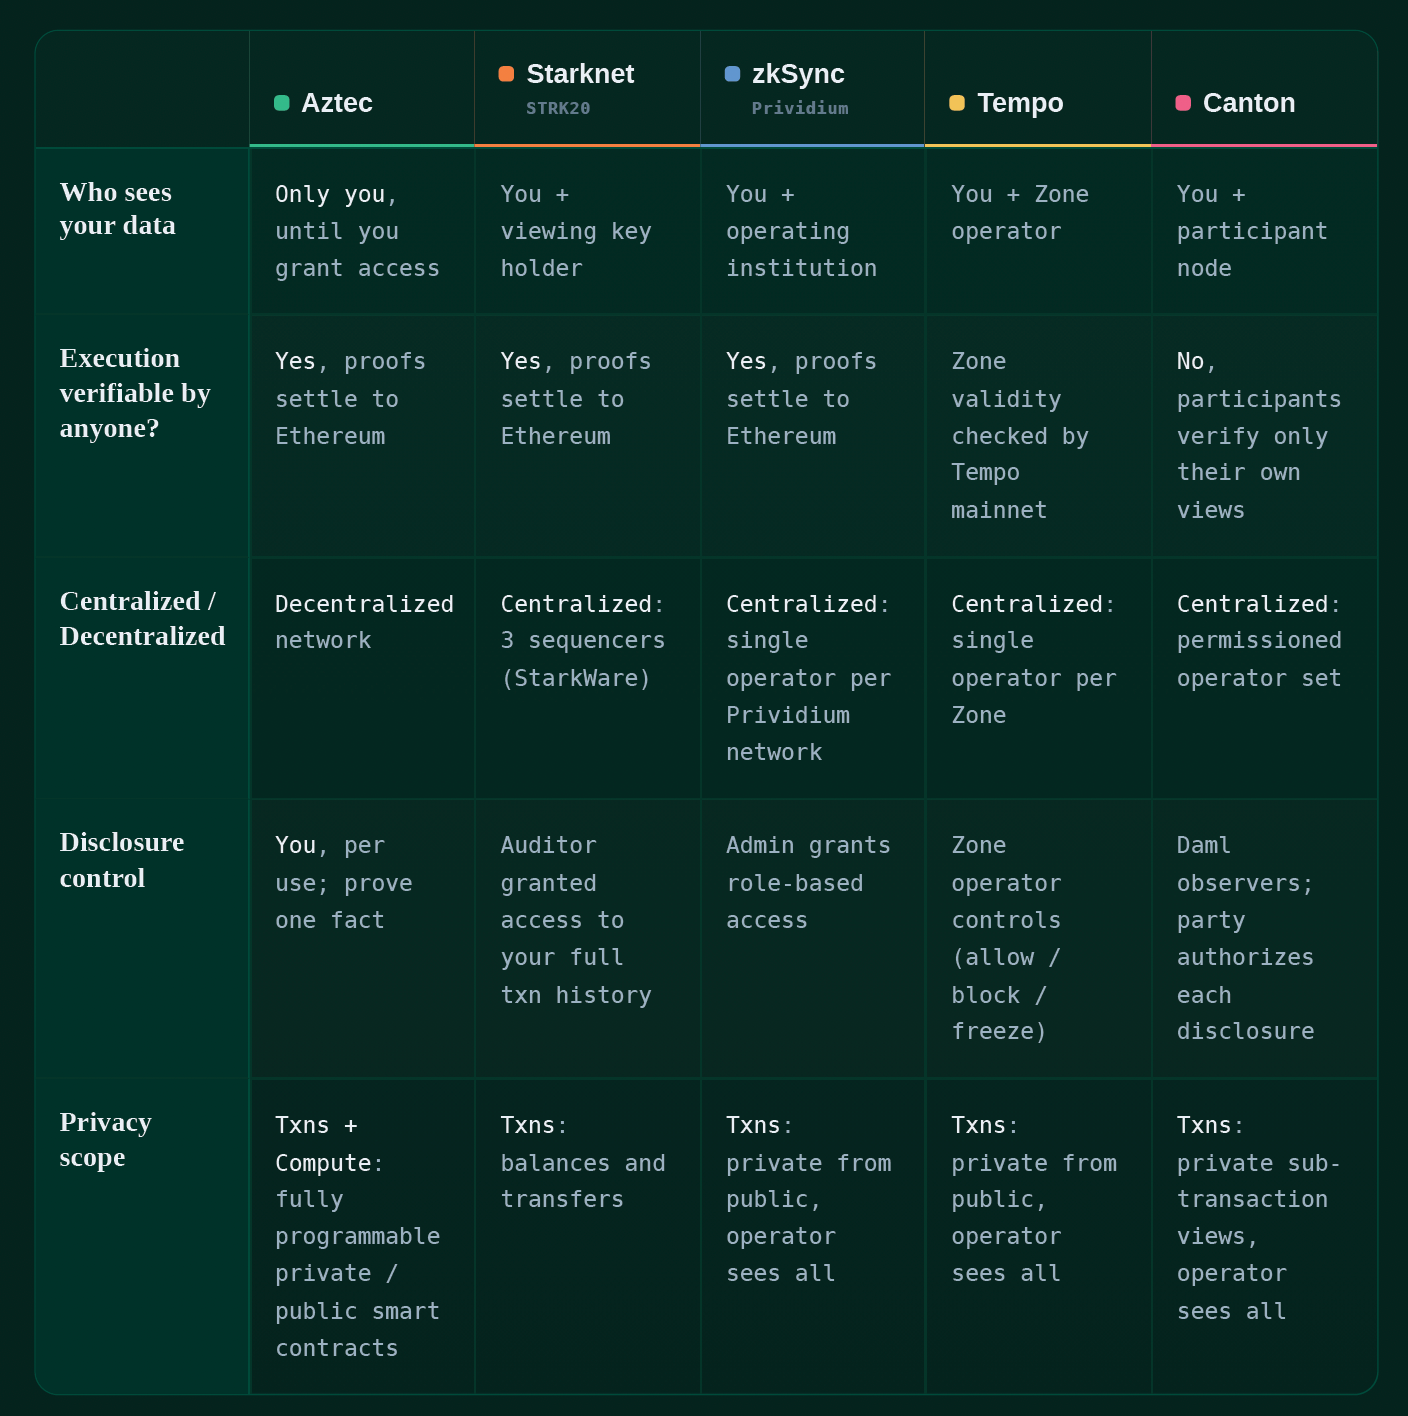
Each of these networks offers privacy with selective disclosure, but each rests on a different network design with its own tradeoffs. We have ordered them by who holds your privacy off-switch, starting with designs where a third party controls access to your data and ending with designs where that control stays with you. At the top, the switch sits behind a policy promise and an honest operator, and further down it is replaced by proofs that the user generates and controls.
Canton keeps data private by controlling viewing permissions for the various actors on its network. A transaction splits into per-participant views, so each party receives only the sub-transactions that name it, and the parts it is not entitled to never reach it. The sequencer and mediator move those views without reading them, which is real privacy against those roles.
However, the data is still read in plaintext by the participant nodes that host the relevant parties, and in the common regulated-asset pattern where the issuer is a signatory on its own token, the issuer's node sees every transfer. The harder gap is verification, because no third party can reconstruct the global ledger, so correctness rests on the confirming nodes staying honest and their keys staying safe. In practice the off-switch sits with those nodes rather than with you, since you cannot see when your data is read and cannot stop it.
Tempo is designed for payments and uses validity proofs to verify that each zone is executing correctly, while still giving the zone operator full plaintext visibility into every transaction within that zone. Privacy comes from Tempo Zones, which are parallel execution environments connected to the Tempo mainnet.
By design, the zone operator has visibility into all transactions within the zone, while users see only their own and the public sees only a proof that the zone is valid. Token issuers set compliance controls, allowlists, blocklists, and freezes, enforced across zones. The mainnet checks each zone's validity, so execution is verified, while the operator still reads every transaction in plaintext and holds the off-switch over what is revealed. Your privacy is from the public, not from the operator.
zkSync Prividium adds the verifiability piece that Canton lacks. Every batch produces a validity proof settled to Ethereum, so a compromised operator cannot forge state or mint tokens from nothing without also forging a proof, which it cannot do. The tradeoff is that the operator processes every transaction in plaintext and decides who sees what, which means the off-switch stays with the operator and your privacy is from the outside world rather than from the operator itself.
This tradeoff has legitimate uses in high-trust institutional environments. If Bank of America, JPMorgan, and Wells Fargo are transacting on a shared network, a zone where BofA's infrastructure processes BofA-originated transactions satisfies internal control requirements while still delivering genuine ZK privacy from the other banks and the rest of the world. Where this model breaks down is in lower-trust environments where giving an operator full plaintext access and the switch that comes with it holds back product design possibilities.
Starknet's STRK20 breaks from relying on an operator for privacy. It shields ERC-20 balances and transfers in a privacy pool, and every private transaction carries a zero-knowledge proof generated client-side, so no operator sees your plaintext in order to build it.
Disclosure is where STRK20 diverges from Aztec. To join the Starknet Privacy Pool, you register an encrypted viewing key onchain, and it sits there for the life of your participation. On a regulatory request, a designated auditing entity can decrypt that key and trace your complete transaction history, forwards and backwards. StarkWare calls this ‘not a backdoor’ but a carefully scoped access mechanism, and the safeguard is a policy promise that the auditor decrypts only when required. The privacy is cryptographic, but the off-switch is a standing key that someone else holds and can flip whether or not you are watching.
On Aztec your private state lives as encrypted private data that only you can decrypt. The contract developer can choose what state is public and what is private, and whether your encrypted private data is emitted onchain as a private log or shared off-chain instead.
Your transactions get proven client-side on your own device, so no sequencer or operator sees your unencrypted private data. Those proofs settle to Ethereum, which gives the same integrity anchor marketed by Prividium, with every transaction verified and no forged state, but without a single operator who reads your data. The base protocol decentralizes sequencing, proving, and governance, so there is no operator to choose and trust in the first place.
Disclosure is your choice too: you decide who learns your private data, and whether they learn it in encrypted or decrypted form. To grant discovery without readability, you share an app-specific tagging secret that lets an auditor find your data in encrypted form without being able to decrypt and read it. This is enough to prove things calculated from that data, such as a tax basis or a profit and loss figure. Granting permission to actually read the data works differently. There's no per-contract read key you can hand out, because decryption uses your master viewing key, which would unlock all your data across every contract. So instead of sharing a key, you share the data itself, plus a proof that your plaintext is what encrypts to the on-chain ciphertext.
Aztec has true selective disclosure in that you can selectively share it, and nothing else you don’t need to. This is app specific, meaning that private data discoverability access on one app does not grant access on another. Most importantly, the off-switch stays in your hands, and you never need to trust the network to handle access to any of your private data and activity.
This is not just conceptual: here is a working proof-of-concept of this model on Aztec. PrivPNL takes you from private DEX trades through a tagging-key disclosure to a browser-generated ZK proof of your PnL. The auditor verifies a proof while the prover only has to reveal the amount they owe, and your portfolio stays private.
Canton keeps the switch with the participant nodes that read your data in plaintext, so disclosure rests on those nodes staying honest rather than on anything you control. Tempo similarly gives the off-switch to a zone-based node operator, but allows you to verify the correctness of transactions using validity proofs. Prividium hardens that promise with a proof settled to Ethereum, a real improvement, but the operator still reads every transaction and still decides who sees what. This can work well for large institutions, but small to medium sized enterprises are left with the same privacy as their current banks unless they run their own Prividium nodes. STRK20 moves the switch into a standing viewing key and asks you to trust that a designated auditor reaches for it only when needed. In each of these models the real question is not whether your privacy can be switched off, but who gets to do the switching, and whether you would even know it happened.
Aztec takes the operator and the standing key out of the question entirely. You keep the data, you generate the proof, and you disclose the result, one fact at a time and only when you choose to. The off-switch never leaves your hands, and no operator, auditor, or node can reach it on your behalf. This is one of the benefits of a network that offers fully programmable, privacy-preserving smart contracts that put you in control.
Selective disclosure is how privacy survives contact with a regulator, and the model you pick decides who can open your history when you are not looking. On Aztec, that answer is no one but you.
Dive into the technical details: Try a live demo of selective disclosure on Aztec and read the technical article on how it was built.
Integrate with Aztec: Reach out if you are interested in integrating privacy into your project.
Alpha is live: a fully feature-complete, privacy-first network. The infrastructure is in place, privacy is native to the protocol, and developers can now build truly private applications.
Nine years ago, we set out to redesign blockchain for privacy. The goal: create a system institutions can adopt while giving users true control of their digital lives. Privacy band-aids are coming to Ethereum (someday), but it’s clear we need privacy now, and there’s an arms race underway to build it. Privacy is complex, it’s not a feature you can bolt-on as an afterthought. It demands a ground-up approach, deep tech stack integration, and complete decentralization.
In November 2025, the Aztec Ignition Chain went live as the first decentralized L2 on Ethereum, it’s the coordination layer that the execution layer sits on top of. The network is not operated by the Aztec Labs or the Aztec Foundation, it’s run by the community, making it the true backbone of Aztec.
With the infrastructure in place and a unanimous community vote, the network enters Alpha.
Alpha is the first Layer 2 with a full execution environment for private smart contracts. All accounts, transactions, and the execution itself can be completely private. Developers can now choose what they want public and what they want to keep private while building with the three privacy pillars we have in place across data, identity, and compute.
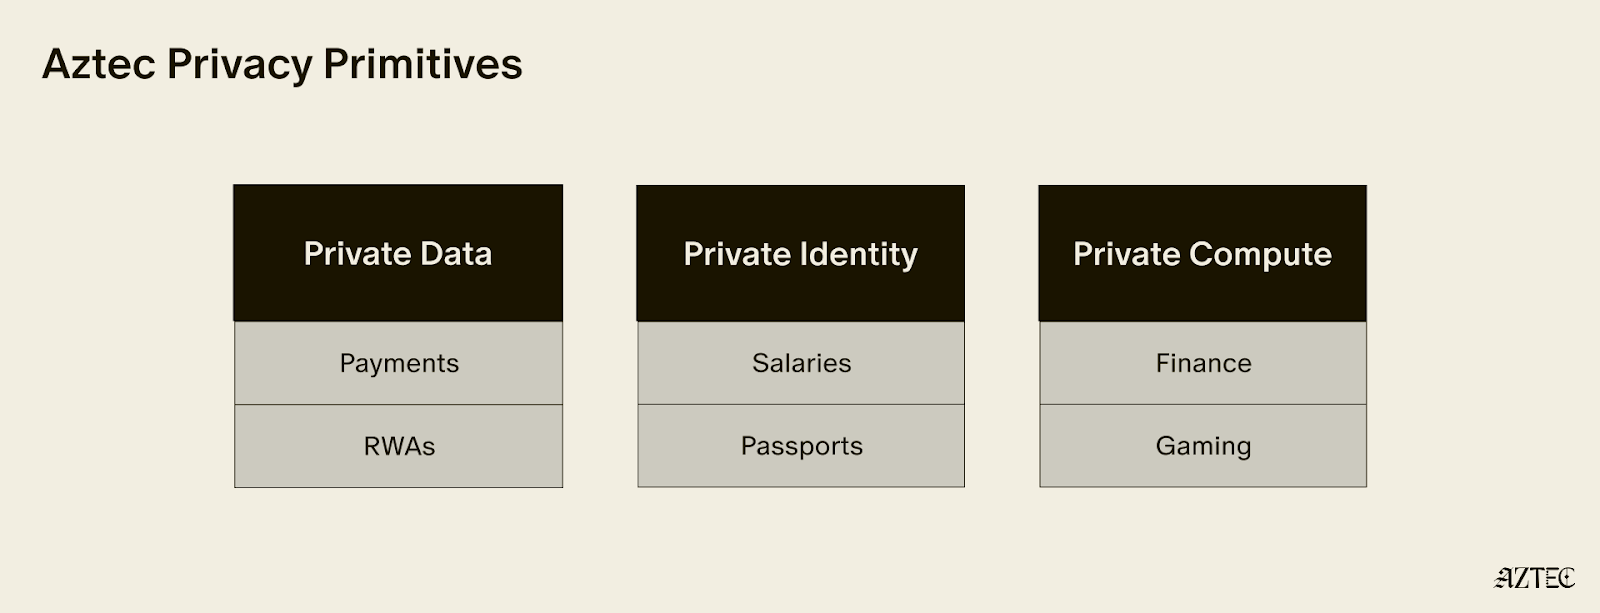
These privacy pillars, which can be used individually or combined, break down into three core layers:
Alpha is feature complete–meaning this is the only full-stack solution for adding privacy to your business or application. You build, and Aztec handles the cryptography under the hood.
It’s Composable. Private-preserving contracts are not isolated; they can talk to each other and seamlessly blend both private and public state across contracts. Privacy can be preserved across contract calls for full callstack privacy.
No backdoor access. Aztec is the only decentralized L2, and is launching as a fully decentralized rollup with a Layer 1 escape hatch.
It’s Compliant. Companies are missing out on the benefits of blockchains because transparent chains expose user data, while private networks protect it, but still offer fully customizable controls. Now they can build compliant apps that move value around the world instantly.
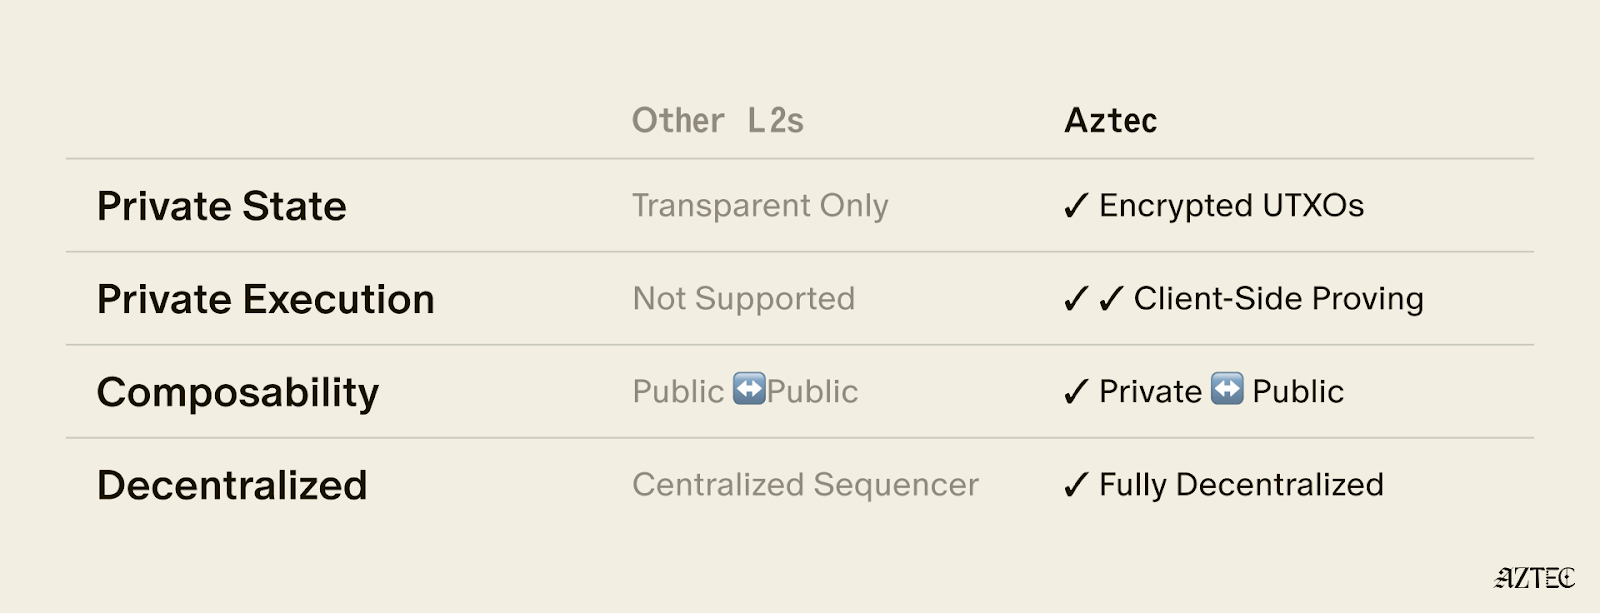
Developers can explore our privacy primitives across data, identity, and compute and start building with them using the documentation here. Note that this is an early version of the network with known vulnerabilities, see this post for details. While this is the first iteration of the network, there will be several upgrades that secure and harden the network on our path to Beta. If you’d like to learn more about how you can integrate privacy into your project, reach out here.
To hear directly from our Cofounders, join our live from Cannes Q&A on Tuesday, March 31st at 9:30 am ET. Follow us on X to get the latest updates from the Aztec Network.
The following is written by Zac Williamson, with inspiration and advice from Arnaud Schenk.
My fellow companions, my decentralized brothers and sisters. I wish to tell you a story, about complicated people and their struggles to resolve the wreckage of their contradictions. It is a story of humanity.
We are at a unique point in history and stand at the threshold of two worlds. One world is a propagation of our present, a status quo antebellum with all of its associated joys and sorrows.
There is another door, one hidden from view except for those with the sight to see it. You and I are here because we see a unique vision of the future, one of high technology and high ideals, that advance human beings from their status as a commodity resource in a globalized world, to free actors imbued with autonomy and purpose, who bow to no one.
I want to articulate this vision and examine the forces that drive us. Despite our successes and dedication it is clear that our current achievements fall short of our aspirations. We must reconcile this.
Bitcoin is not yet a credible threat to traditional currencies. Paying for goods and services with cryptocurrency is a niche luxury for the technologically well-connected. Decentralized autonomous organizations (DAOs) are yet to govern anything that is not a cryptocurrency project. A notable exception was ConstitutionDAO, which immediately failed in its goals due to the intrinsic limitations of trustless blockchain networks.
There are missing pieces in the technological armaments we have fashioned. I want to show you the missing pieces. I want to go back to the roots: what are the systems and frameworks we want to disrupt? Which properties do blockchain networks need for us to forge a conspiracy against the present, and fight for our vision of the future?
Reaching back into prehistory, humanity has been waging a war against itself – a war that pits the freedom and autonomy of individuals against the safety and control of institutions.
We want to be free. We want to be safe. This is the eternal contradiction.
To acquire safety we bind ourselves to institutions. Within these institutions, control factions form. They metastasize and act to entrench their power and influence by monopolizing human agency. This triggers inevitable conflict and revolt, which acts to reset the equilibrium.
How best we can resolve the contradiction between freedom and safety is a function of social organization, the quality of which is gated behind technological innovation.
Blockchain is one such technology. To identify what we need, we must identify the weaknesses of the institutions we seek to undermine, and tailor our strengths against them.
Control factions have a fatal weakness: they reject competence.
Competent people threaten individuals within entrenched power structures. A competent subordinate is a threat to your power and privileges. This is the so-called “dictator trap”, but the mechanics at play extend to all power structures, from the boards of mega-corporations to the local residents association. But it’s not a dictator trap, it is an institution trap.
Power craves legibility and predictability and will act on these desires by exerting control – limiting agency and freedom of action.
We want to undermine institutional control, and redistribute control down to smaller units of organization.
Blockchain technology enables such radical new forms of social organization that fall outside the frameworks of traditional institutions.
We possess a keystone technology that enables mass peer-to-peer coordination, initially of cryptocurrency assets but this can be generalized to anything with perceived value that can be given a digital fingerprint.
Blockchain networks have radically different incentive mechanisms to traditional modes of social organization.
Because blockchains are coordination engines. They enable individuals to coordinate on how to deploy their collective resources. This type of mass-coordination of personal resources is unique and will subtly act to profoundly re-distribute the existing power structures of the present.
Why? Blockchains weaken the fundamental value propositions of vertically integrated companies that extract a profit from information asymmetries. Individuals whose skills serve large institutions can more easily decide for themselves how best to apply their skills, without the need for the institution’s support frameworks. As a coordination engine, blockchain networks can efficiently combine the skills and capital required to execute grand ideas, as well as provide a digital market for resulting products.
A global marketplace of programmable money is one with profound information transparency. The ability of independent groups to analyze the market enables great efficiency and reduces information asymmetries. Though, does not delete them entirely.
In short, blockchain networks are pro-competency. They allow individuals to decide for themselves how their skills can best be utilized and deployed, instead of having that decided for them by a control faction. Competent people add value to the network and in doing so, provide another composable brick that others can use in their constructions. The raw incentives create a positive-sum game.
What are the missing pieces?
The great difficulty in realizing our vision is the limited ability of current blockchains to reach into the real world.
We are not our online avatars. We exist in a physical space and we have physical needs that must be satisfied. We are bound to networks of obligation and responsibility that societies depend upon to maintain social order. We cannot live in an NFT.
The real world matters. Without a way of linking real-world identities to blockchains, the grand cypherpunk vision for blockchain can never be fully realized – only a neutered form of primitive electronic sovereignty.
The new information networks we are building lack a key ingredient: composable privacy.
By using novel cryptography, we can turn blockchains into encrypted ledgers where transactions hide their execution from observers. Identities can be encrypted, but still used to prove statements about the user, and without involving an additional institutional third party. e.g. “I have a U.S. passport”, “I have a digital driving license”, “I have a Twitter account with over 1,000 followers”, “I signed in with a Google account”.
The effect of this is to build trust infrastructure that allows human beings to iteratively build trust between themselves and to do so rapidly and at scale.
Programmable private blockchains stand to usher in a revolution in how distributed systems can be used. Without strong identity guarantees, the only workable governance mechanisms for distributed on-chain organizations are autocracy and plutocracy.
However, if past actions can be uniquely tied to a cryptocurrency account, it is possible to identify key stakeholders and to give them an accelerated role in governance. That enables a much more democratic architecture of governance systems.
Privacy technology is required to turn blockchains into the coordination engines they were always destined to be.
The future we are building does not outright destroy existing systems of control – it breaks them apart and replicates these systems on a smaller scale. Lower barriers to entry lead to greater competition and market fragmentation and act to limit the ability of distributed organizations to consolidate power.
Because coordination engines are pro-competency.
There is a phrase I think we will hear much of over the coming years: privacy for the user, transparency for the protocol.
The capabilities of private programmable blockchains and the outcomes they enable are not commonly understood. A private blockchain is not one where all information and data are intrinsically hidden. They are hybrid systems where public and private data coexist. Application designers and users can choose which data is hidden.
Efficient markets require data transparency. Data relating to identity requires data confidentiality. The solution is applications where information that relates to assets is public, and information relating to users (e.g. who owns said assets) is private.
To create a privacy-preserving ecosystem it must be possible for confidential, transparent, and hybrid applications to directly interact with one another. Privacy is not an aftermarket add-on to be bolted onto a few select applications. Full composability is essential to develop a rich ecosystem.
Composability enables trust-building networks by allowing individuals to put core aspects of themselves on-chain, disclosing it only selectively and enabling distributed protocols to use these capabilities in a composable permissionless manner, without leaking information. Who are you? What have you done? What do you want to do? With privacy, we can disclose this information to smart contracts and hide it from people. These will form core primitives of our new information networks.
I have spent the last 6 years building exactly this, through building Aztec. Crafting the missing ingredient, privacy, via cutting-edge cryptography, zero-knowledge proofs, and raw engineering.
Networks have values that are independent of their creators. Networks live or die on the quality of their network effects. This incentive gives network participants a shared motivation to expand the network. The more nodes that exist, the greater the value individual nodes can extract from the network. The manner in which the network changes itself to act on these motivations defines its intrinsic values.
What are the intrinsic values of permissionless programmable privacy networks like Aztec? We can derive these from the fundamental value proposition – to expose a rich ecosystem of composable, confidential applications, and to do this as a permissionless, decentralized network. This enables individuals and small groups to compete in industries dominated by large players leveraging large information asymmetries.
Such networks are, at their very core, pro-competency. If you have something useful to add to the network, you can. If you want to use existing network components in your product, go right ahead. No need to ask for permission from the network.
From this starting point we can anticipate the cycles of action and reaction that will drive networks like Aztec to adopt the following values over their lives:
Blockchain networks grow by harnessing the industry and enterprise of as many human souls as they can get their hands on.
Without mechanisms of coercion to fall back on, the network must ensure a positive-sum game for network participants who add value. These also happen to be values that I believe I strongly hold. This is not a coincidence. I started in web3 seven years ago building a marketplace for corporate debt on Ethereum and by degrees ended up building a distributed programmable privacy network on Ethereum. This was not due to some grand design but, I think, the cumulative effects of seven years of following my impulses. To find a place of belonging.
This feeling is something you may share – that the frameworks and systems produced by our societies offer none of us a true sense of belonging and purpose. But here, amongst our companions, we have found belonging through building a shared vision of a radical new world.
There is a long road to walk to realize the ambitions of the new information networks. The technology is barely capable and challenging to build. The architecture is novel and challenging to design. Convincing people to build on radical foundations to bootstrap a market is challenging. Building competitive infrastructure and tooling is challenging.
The challenge is irrelevant. We cannot become a generation scorned by our descendants for squandering the opportunity of a lifetime.
We will build and deploy the new information networks and by degrees will learn how to use them to chip away at the inequities of the status quo, and the social order that upholds it.
Equipped with such armaments and driven by our ideals, we will pull our ideas into reality. Together, we will forge our digital Eden.
Kev Wedderburn is the father, architect, and team lead of Noir, a universal zero knowledge circuit writing language funded by Aztec Labs.
We're excited to bring you this interview and profile of the man and mystery behind the DSL creating a step-function change in the accessibility of ZK programs.
Alyssa: Hey Kev! Thanks so much for your time, I’d love to give readers a snapshot of your journey into web3 and Aztec Labs, as well as your focus on the Noir team.
Kev: Sure! Let’s jump in.
Alyssa: Can you start by sharing your web2 background?
Kev: Yes. I started out as a front-end developer, then moved into app development.
I built a social media site for books. Then, a janky music-sharing app that would check your playlist, then check my playlist, then if our playlists overlapped enough, it would recommend each of us songs on each other's playlist (this was before Spotify became Spotify I think).
Alyssa: How’d app development lead you to going full-time web3?
Kev: While transitioning to crypto, I made a tax app that scanned your bitcoin QR code and told you how much tax you owed.
From there, I started doing tutorial videos focused on smart contracts. I wanted to do one for a particular blockchain, and it turned out that they didn’t have a well-functioning wallet. So that’s actually what led to my entry into the web3 space. I didn’t end up finishing that tutorial, I just went on to build the wallet myself.
Alyssa: And this work led to your first formal web3 role?
Kev: Eventually, yes. While I was working on an improved wallet, I noticed the node that the original wallet was interacting with wasn’t that great either. So once the new wallet was finished, I moved on to creating a node in Golang (the wallet was also originally built in Golang).
After I finished the node, I got recruited by a privacy-focused project. And they asked me to build a node for their privacy network.
Once I dug deeper, it turned out they didn’t have a proving system. So then I started learning cryptography to implement a type of ZK proof called bulletproofs — state of the art at the time.
Alyssa: And you’ve primarily worked on privacy within web3 ever since, is that right?
Kev: Yes, I worked for several other privacy blockchains prior to Aztec, such as Monero. At Monero, I pivoted from implementing Bulletproofs to Plonk for increased proving speed, but noticed it was very challenging to program on top of Plonk.
The Plonk constraint system and proving system both have nice properties, but the UX was really bad. So Kobi Gurkan from Geometry Research, and Barry Whitehat from the Ethereum Foundation asked if I wanted to make a compiler — I guess they saw that I was pretty active within Plonk and cryptography in general.
Alyssa: Had you built one before?
Kev: At the time, I didn’t know much about compilers at all, so it was exciting to figure out what the compiler I’d build would look like, what other compilers were doing, and how to make a compiler with the safety guarantees needed for zero knowledge proofs.
That was the beginning of what we now call Noir, and I’ve been at Aztec since.
Alyssa: Wow, okay, so you’ve been with the Noir project since the beginning of Noir’s existence?
Kev: Yeah, exactly.
Alyssa: Amazing, congrats on all the progress you and the team have made. And what about getting into web3 in the first place? Was it through engineering, or your own interest in cryptocurrency? How did that look?
Kev: I first looked at Bitcoin in university, but was deterred by the codebase being challenging to read. But I wanted to learn Bitcoin and teach people about it. Back then, everything was a bit scammy. I even created a Bitcoin book…
Alyssa: Going back to Noir, how do you feel about the experience of learning the language you helped build? Is it intuitive for developers?
Kev: I can tend to over-criticize the things I do. But Noir’s in a solid place. There’s not much to really compare it to….there are other zkDSLs, but they give different guarantees for the most part. For example, Noir provides devs with a high-level language that aims not to sacrifice performance and safety, while Circom gives devs very little safety but allows them to do anything. There are pros and cons to both of these approaches.
The more control you give to a developer, the more powerful things they can do, but they can also easily make mistakes because the compiler is no longer holding your hand or stopping you from doing something potentially dangerous.
But yes, Noir is in a good place for developers to use. There’s still a lot we want to put into the language to make it comparable to common programming languages in terms of UX. But we’re well on our way.
Alyssa: And what about just being on the Aztec Labs team in general, and maybe even the Noir team within Aztec Labs? What’s that like? What do you enjoy about it?
Kev: The Aztec team is cross-functional and fluid, meaning that even though you’re on the Noir team, or the tooling team, or the engineering team, you can touch other parts of the stack. So that’s great about being at Aztec.
The fun thing about the Noir team in particular is that there are so many challenges we have yet to solve. We’ve solved quite a lot of them, but there’s still a lot we’re excited to work on like continuing to improve the UX, as I mentioned.
Alyssa: Love that answer as I know there’s a job opening on the Noir team, so someone joining can have exposure beyond understanding their specific role.
Kev: In fact, we encourage that, if you’re on tooling and you want to create something and the compiler just doesn’t seem to be fit to do what you want, feel free to start some print or tasks to modify the compiler. We’re always open to new ideas.
Alyssa: Really cool, that’s great. And what about beyond web3, any general interests or hobbies?
Kev: Generally speaking, I really like maths. I also used to sing and play guitar for quite a while, and I exercise a lot these days.
Alyssa: Thanks again for the chat, great learning a bit more about your work, Kev!
Kev: Thank you!
We think Noir has the best syntax, most modularity, and best ecosystem of any ZK language. But don't take our word for it.
Get started with Noir at noir-lang.org.
Today Aztec Labs is proud to announce that Aztec’s core circuits have been rewritten in Noir.
Aztec’s core circuits were previously written in C++. The circuits spanning private execution, public execution, and proof recursion are now in Noir. We didn’t undertake this decision lightly, but we made the call based on a single fact:
It was always our goal to achieve Aztec-Noir alignment, unifying our cryptography stack and making our code safer, simpler, and easier to audit.
We’re there now, in the era of unabashed Noir maximalism.
💻 You can find the open Noir circuit repos here.
The Noir circuits are merged and passing Aztec’s stringent protocol test suite–huge achievement for Noir as a language.
Writing your code in a domain-specific language (DSL) does not make it safer than writing it in a library.This may not be apparent – a DSL is just a language made for a specific problem. One could create a DSL that makes writing circuits easier, but does not improve on performance. One could even create one that makes writing circuits harder, but it’s very performant. Noir makes writing circuits easier and safer than our cpp library with little sacrifice to performance.
As a startup you want to be able to write code fast, but also safely. If you take too long to ship, you may just die. If you write code that is unsafe or brittle, you may lose the trust of your target audience.
We could say that all developers need to do better. Skill issue. However, this approach doesn’t scale beyond. Developers love to write smart, elegant, clever code, i.e. code that’s subject to bugs. In Noir, you need to opt into writing unsafe code.
So what’s wrong with using Barretenberg as a C++ library?
Nothing.
In fact, a library inherits a lot of adoption from its host language; a Solidity library can be picked up quickly by Solidity developers, for example.
Aztec’s constraint system library is written in C++, and while this allows developers to do anything they want, it also allows developers to do anything they want.
Developers need to be aware of quirks with C++ whenever they use Barretenberg. This can lead to subtle bugs due to the inherent compounding of quirks specific to C++ and quirks specific to the library. In other words, more gotchas or footguns.
Library writers also need to be careful because in some places they are reasoning about constraints. In other places, they are reasoning about unconstrained code or non-constraint system code.
The overarching problem here is that in order to write safe circuits, you need to be able to write C++ code and also be a good circuit writer. These are two different skill sets that Noir reduces to one because Noir is specifically designed as a circuit writing language.
In March, a team of cryptography engineers developed Aztec’s core cryptography circuits under the guidance of Aztec Labs CEO Zac Williamson. Developing in C++ required significant onboarding and technical overhead, including:
In the meantime, the Noir team has built a comprehensive toolchain that makes ZK development significantly smoother:
In addition to developer tooling like performance profiling, syntax highlighting, and auto-formatting.
With Noir, we built the fast and safe DevEx we wanted for ourselves, resulting in a full rewrite of all Aztec core circuits from C++ to Noir in less than a month of three engineers’ time.
Here’s a side-by-side code snippet comparison of our private kernelbase rollup circuit in C++ and Noir, highlighting the legibility and simplicity of Noir.
C++:
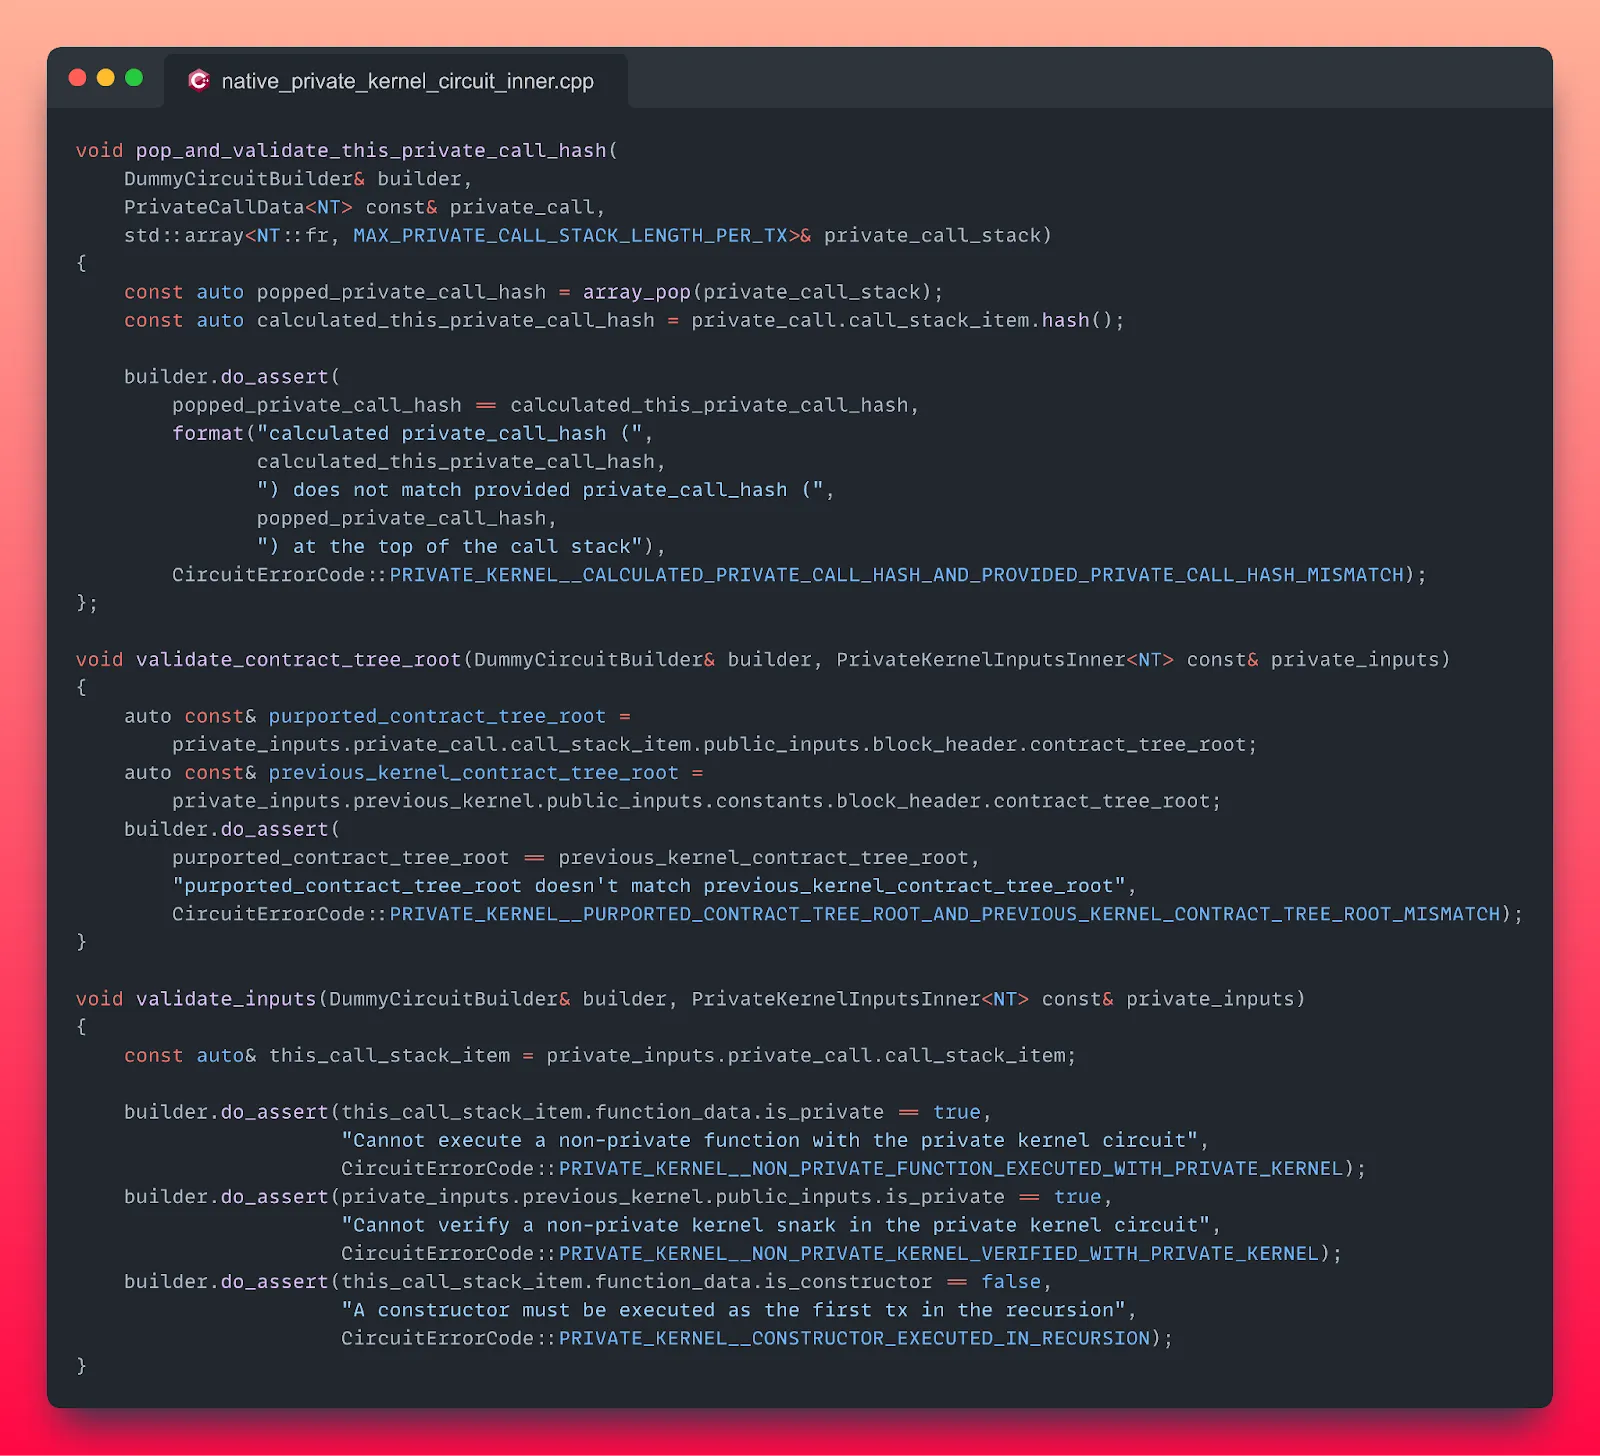
Noir:
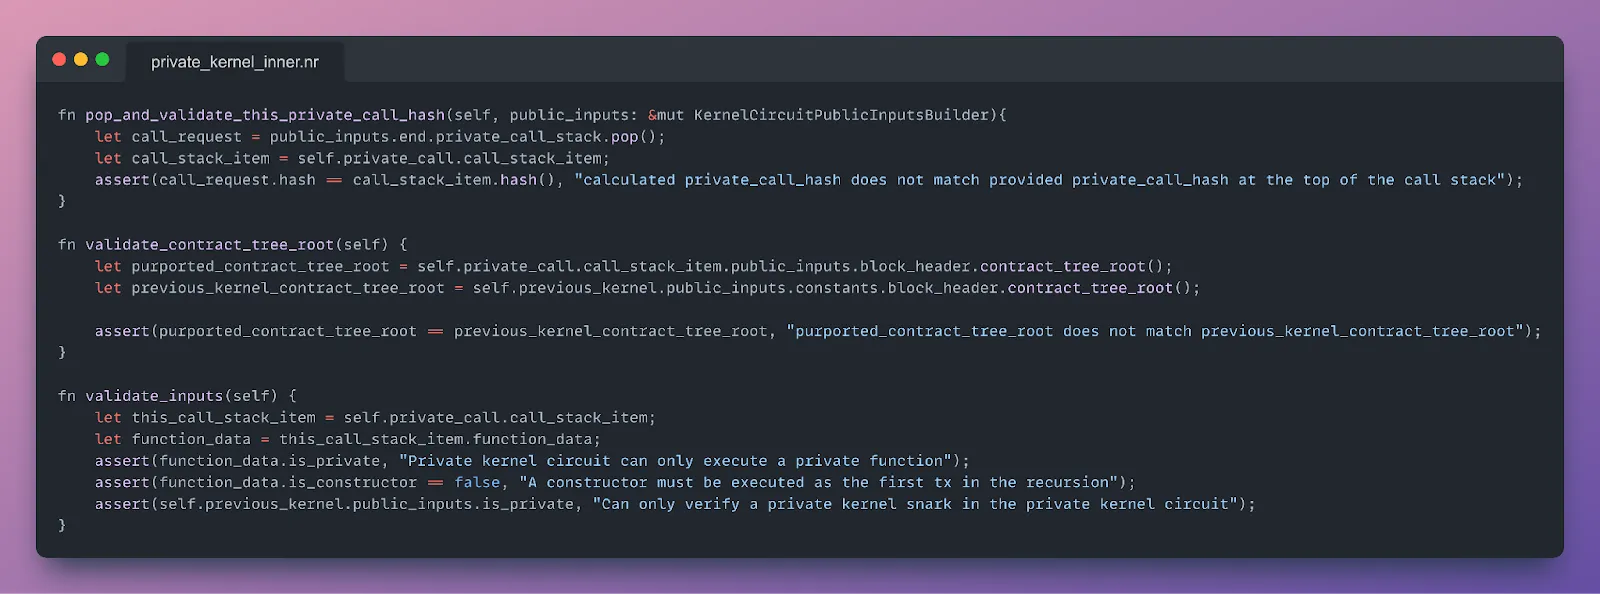
Finally, Aztec Labs gets to more fully participate in Noir’s vibrant ecosystem.
The community continues to develop new tooling that improves code analysis. Developers building in the Noir ecosystem and discovering bugs continuously battle-test the compiler. And Aztec is now fully aligned with the many developers building applications and protocols on Noir.
We too would like to share in the fruits of the Noir community.
Noir maximalism is open-source maximalism.
While Noir is still Beta software and isn’t fully production-ready until it is audited, the language is progressing towards an implementation freeze by the first half of 2024, and a completed audit by the back half of the year.
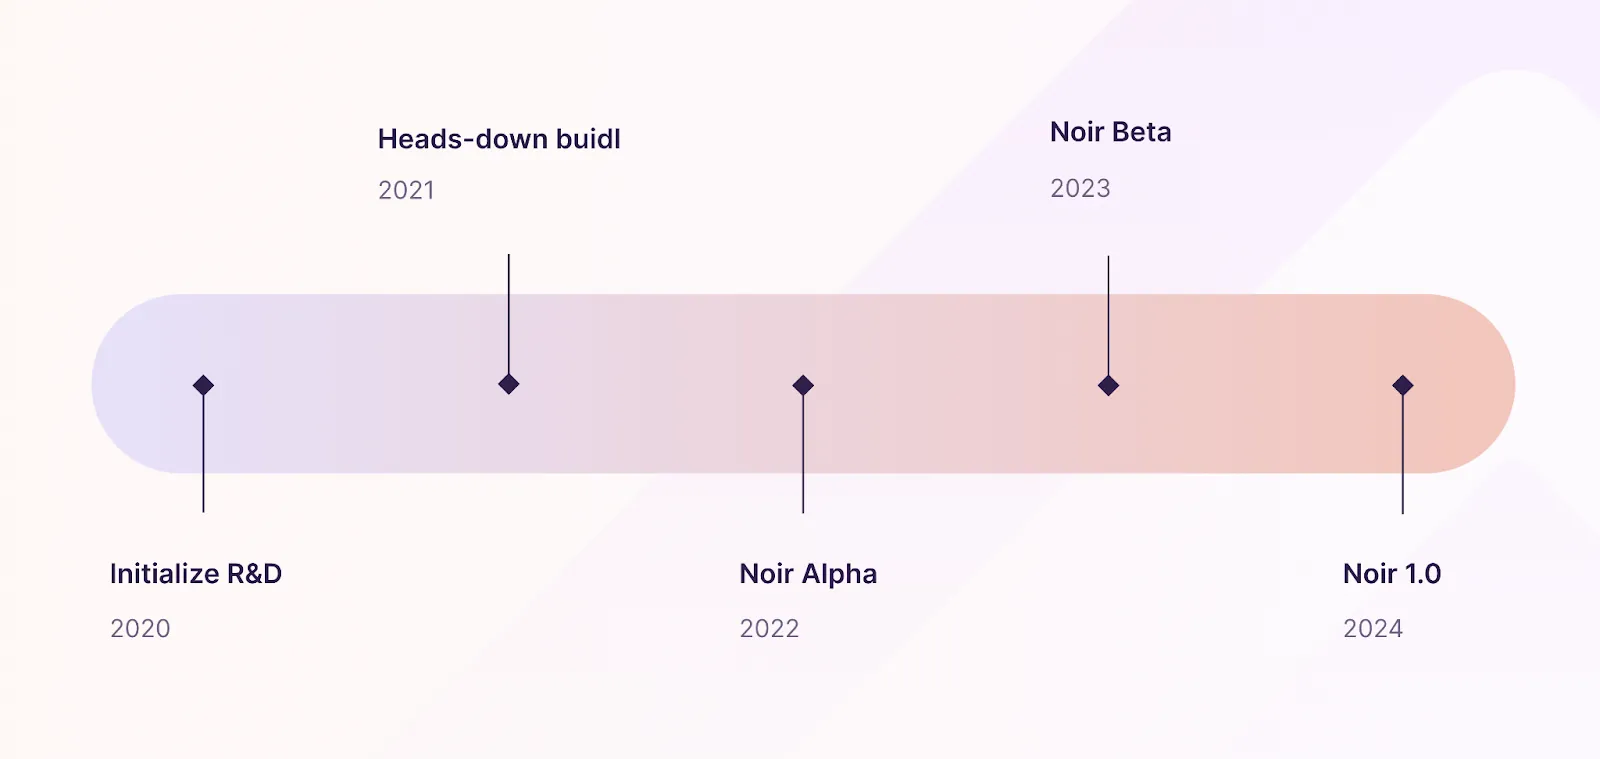
🏗️ Start building with Noir at noir-lang.org.
In addition to basic optimizations required for the kernel circuit to run on low-powered mobile devices, we intend on integrating Noir with the arsenal of novel cryptography in our development pipeline:
Building Aztec in Noir has been a long time coming.
As a result of adapting our core circuits to Noir, testing a wide array of features, and having Noir code pass extensive test suites, we have dramatically more confidence in its stability.
The collaborative approach between our internal Aztec and Noir teams demonstrates a commitment to advancing the capabilities of zero-knowledge proof technologies in an integrated fashion.
Improving Noir now improves Aztec.
The truth of the matter is: you cannot escape potentially dangerous code.
You can still write unsafe code in Noir.
You can only move the responsibility of writing dangerous code to folks who are least likely to make a mistake. And with Noir, you make it Aztec Labs engineers’ responsibility to write compiler code and optimizations. And with our stack, we make it the cryptographers’ responsibility to write absolutely unhinged cryptographic proving systems.
You are free to rebuild all of this yourself in C++. But Noir makes it so you don’t need to.
Where we cannot help you is unsafe business logic. If your application was meant to choose a random number between 1 and 10 and it instead chooses a random number between 0 and 1, then that’s on you.
But that’s as it should be! That’s the sort of code that you should be responsible for, and Noir aims to make it such that that’s the only thing you are responsible for.
If that sounds good to you, you might consider making the switch, as we have.
⭐ Get started with Noir today at noir-lang.org.
Today we’re releasing NoirJS– a Javascript package for Noir developers who want to build real applications that generate zero knowledge proofs in the browser.
Web development within the Noir ecosystem has historically been, uhm, complex. Practically, that meant Noir developers couldn’t really build applications that ran in the browser. And we want people to build applications with our software!
A browser is an application used to access the World Wide Web and interact with Internet applications. It turns out most people like using browsers.
Before today, Noir didn’t really let you build applications that could run in-browser. Instead, developers were forced to run applications locally in a CLI.
In simple terms, that meant Noir couldn’t actually support real applications.
But now Noir does support applications with NoirJS.
The goals of NoirJS are simple:
Noir is a zero knowledge circuit-writing language that works with multiple crypto proving back-ends. That means the front-end (the language) remains the same but Noir can be modularized to support the latest and greatest in zero knowledge proving research.
We do this through the ACIR (abstract circuit intermediate representation). Learn more about the ACIR here.
NoirJS lets developers build around the core concept of client-side compute: the ability to harness user hardware–phones, laptops, tablets–through the browser in order to compute proofs of execution.
And client-side compute in turn allows for fully private and trustless blockchain systems.
…sound familiar??
That’s the core philosophy of Aztec–giving developers the tools to develop programs with private data and compute while remaining fully trustless.
In English: do blockchain things without anyone knowing! Cool, right?
And for developers’ convenience, NoirJS is packaged with Barretenberg–the same Plonkish backend used by Aztec Labs in the Aztec rollup. No need to go shopping for a proving system unless you like, really want to.
NoirJS does a lot of other things, too! Developers were previously burdened by the need to manage multiple components like `bb.js`, `acvm`, `noirc_abi`, and future components like `noir_wasm`.
But managing component libraries and balancing version compatibility is not our idea of fun.
To install NoirJS you simply run `npm i @noir-lang/noir_js` in your Javascript directory
Install your proving backend of choice (ahem, probably Barretenberg), and you’re good to go.
NoirJS handles all Noir dependencies, exposing them through one clean interface, allowing you to focus on building rather than fiddling with packages.
Here are some other advantages:
Immediate Access: Browser-based applications don’t require additional software, making it easier for developers to reach a wider audience.
Improved User Experience: By enabling Noir functionality in the browser, users can interact with applications in real-time. That means fast apps.
Enhanced Security: Operating in the browser allows for client-side cryptography, offering an additional layer of security for applications that require cryptographic proofs.
Developer Flexibility: NoirJS enables developers to build rich, client-side applications with cryptographic functions, providing a broader toolkit for web development.
Community Building: Browser-based Noir enables rapid prototyping and sharing among the developer community. This is especially useful for teams who focus on in-browser applications and use-cases.
In-Browser Tooling: NoirJS fits seamlessly with in-browser IDEs like VSCode for web, allowing for a streamlined development process in which Noir programs can be compiled and proven directly in the browser.
So to summarize, by bringing Noir to the browser, we’re:
Siiick.
Less development pain means more time for building new applications. Here are some use-cases we’re excited to see:
NoirJS lets you build real Noir applications that run in the browser. It also makes your life easy breezy beautiful CoverGirl.
If you don’t know what Noir is, read this announcement, scan these docs, and watch this video.
If you do know what Noir is, install NoirJS right now. Right now. Right now.
And if you end up building something cool, come ask us for money.
